Aurora reporting puts AI coding agents inside the intrusion workflow
Researchers describe an Aurora operator using Cursor during attacks. Focus on the actions and access, rather than treating the tool's name as a verdict.
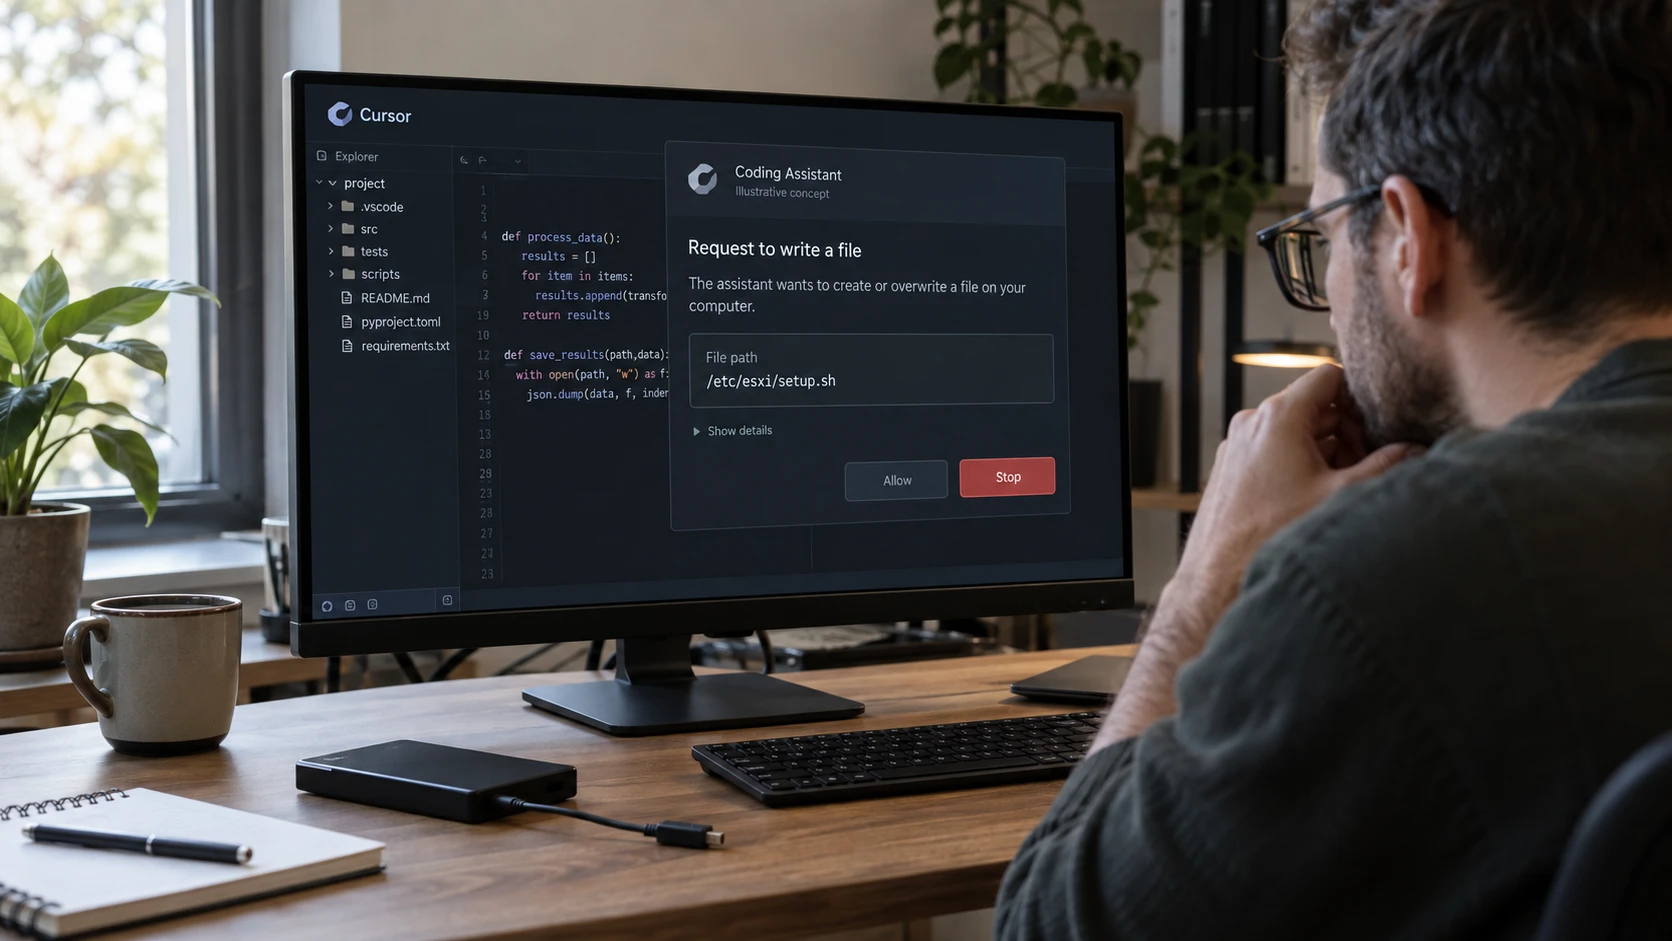
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
A commercial coding assistant can be part of an attacker’s toolkit without being malicious software itself. Gambit Security reports that an Aurora operator used Cursor Agent to assist hands-on exploitation across ten organisations between 8 April and 21 May 2026.
CloudSEK’s separate analysis of the exposed Aurora material describes the operator’s tooling and plans. Together, the accounts give defenders a reason to include coding-agent activity in investigations, rather than assuming it belongs only to legitimate development.
Judge the action in context
The presence of an approved application is not proof that its current use is approved. Ask which account launched it, what it accessed and whether that activity fits the machine’s purpose.
A development tool making changes on an expected workstation is a different case from the same tool appearing on a server where nobody authorised it. The process name alone will not resolve that distinction.
We recommend including agent-launched activity in detection reviews. Can the investigation connect a command or network connection to the process and identity behind it? Can the responder tell whether the action was part of an agreed task?
Review the permissions before the incident
For legitimate coding agents, limit the credentials and systems available to the task. Avoid making broad production access an incidental consequence of running an assistant on a developer’s machine.
For response teams, define how to restrict the affected account or device while preserving evidence. Removing the assistant does not necessarily remove other access obtained during an intrusion.
The lesson is not that every installation of Cursor should be treated as an attack. It is that familiar software can perform unfamiliar work. Good visibility should let you investigate that work without relying on the application’s reputation.