CrowdStrike links PhantomRaven malware to likely AI-written code
CrowdStrike's new PhantomRaven report connects likely AI-written malware, npm packages and bug bounty activity. Here is what the findings establish.
In brief: CrowdStrike assesses that PhantomRaven, malware distributed through npm software packages, was probably written with AI. Its new report links the operator to bug bounty activity.
CrowdStrike published its analysis on 15 September. The company develops security software and investigates cyberattacks. This report concerns the creation and distribution of malware, rather than an AI model independently conducting an intrusion.
How a software package becomes an entry point
Developers use npm to obtain reusable software packages. A package can depend on other packages, which are downloaded as part of installation.
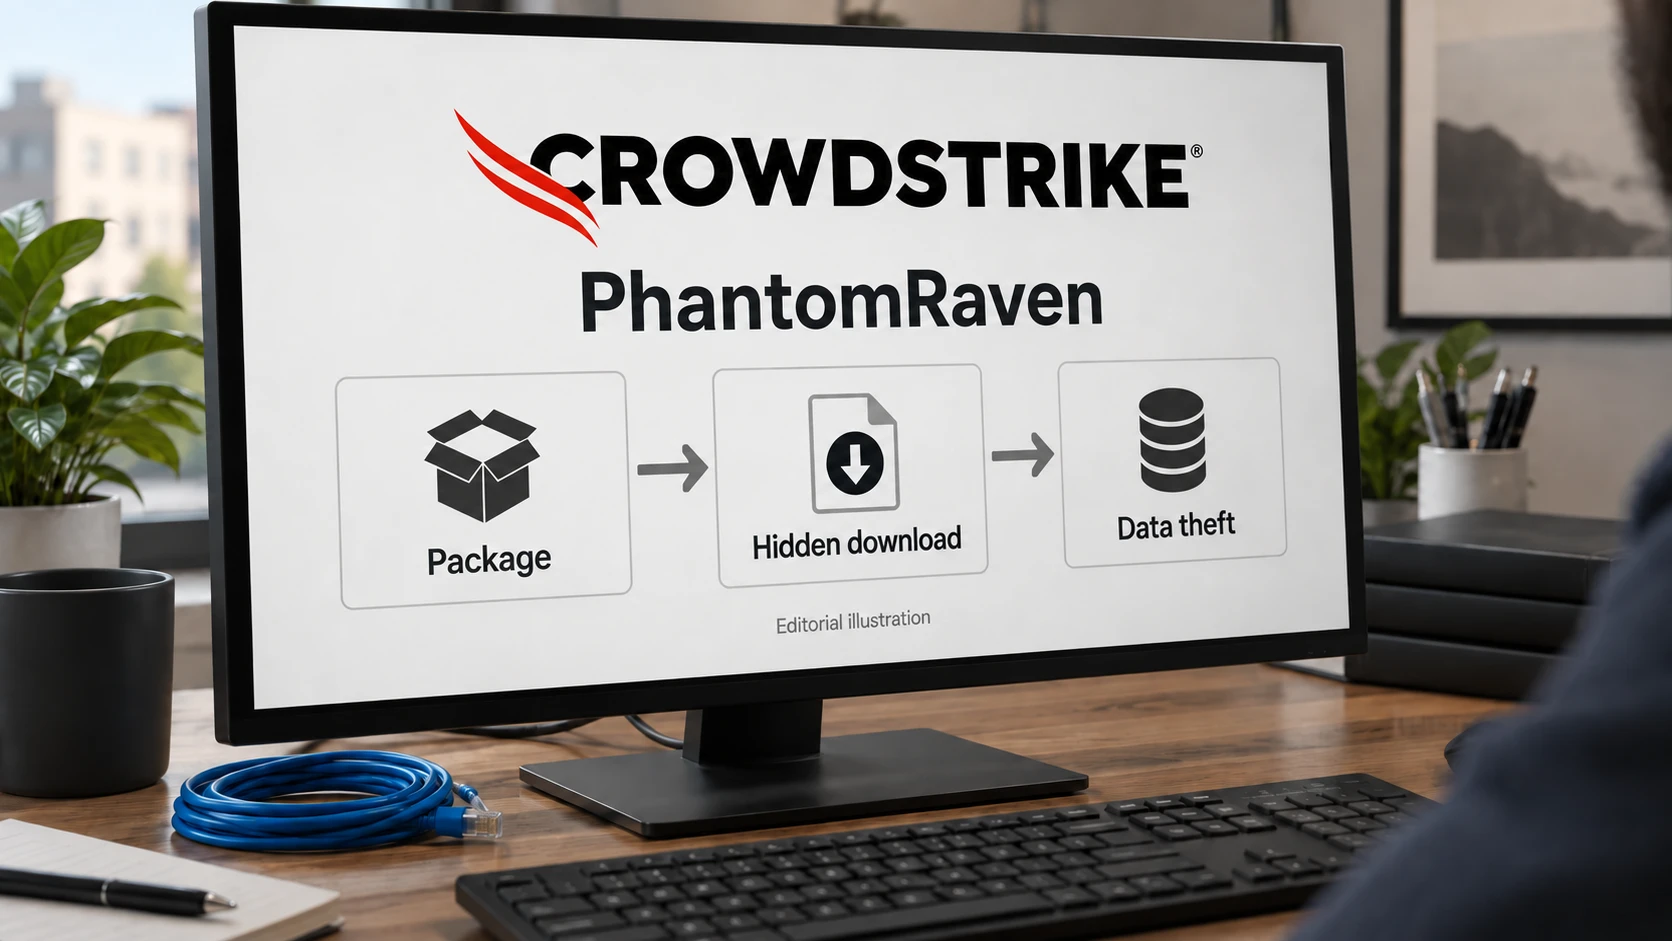
Endor Labs’ earlier investigation describes PhantomRaven packages that fetched additional code from external servers. That code collected information about the computer and its software development environment. The external download matters because the package initially inspected is only part of what reaches the machine.
For a business, a development environment is where applications are built and prepared for release. An intrusion there concerns the machinery behind its software, even if the customer-facing application still appears to work normally.
Where AI fits into the story
CrowdStrike bases its AI assessment on code characteristics, including extensive comments, unfinished placeholders and statistical patterns. It also assesses that the operator likely used compromises to pursue bug bounty rewards. These are the company’s assessments.
A bug bounty programme pays for qualifying security findings within defined rules. Receiving a reward for one report does not establish permission for every method used elsewhere.
Earlier findings add context
PhantomRaven predates this week’s report. In March, Endor Labs published findings on additional packages. In a later update, it relayed the author’s denial of malicious intent and explanation that the collection supported vulnerability reports. Endor also said actual secrets or credentials did not appear to have been exfiltrated in its analysis.
Those observations concern the material each team examined. They should not be combined into a claim that every PhantomRaven incident had the same outcome.
The AI element here concerns how attack software may have been produced. Models that execute hacking actions themselves are a separate form of AI use.
The cover is an AI-generated editorial illustration, not a CrowdStrike product screenshot or evidence from an incident.