Fredrik Standahl in Shifter on startup AI security
Fredrik Standahl's Shifter commentary asks startup teams to make security checks part of releasing AI-generated code.
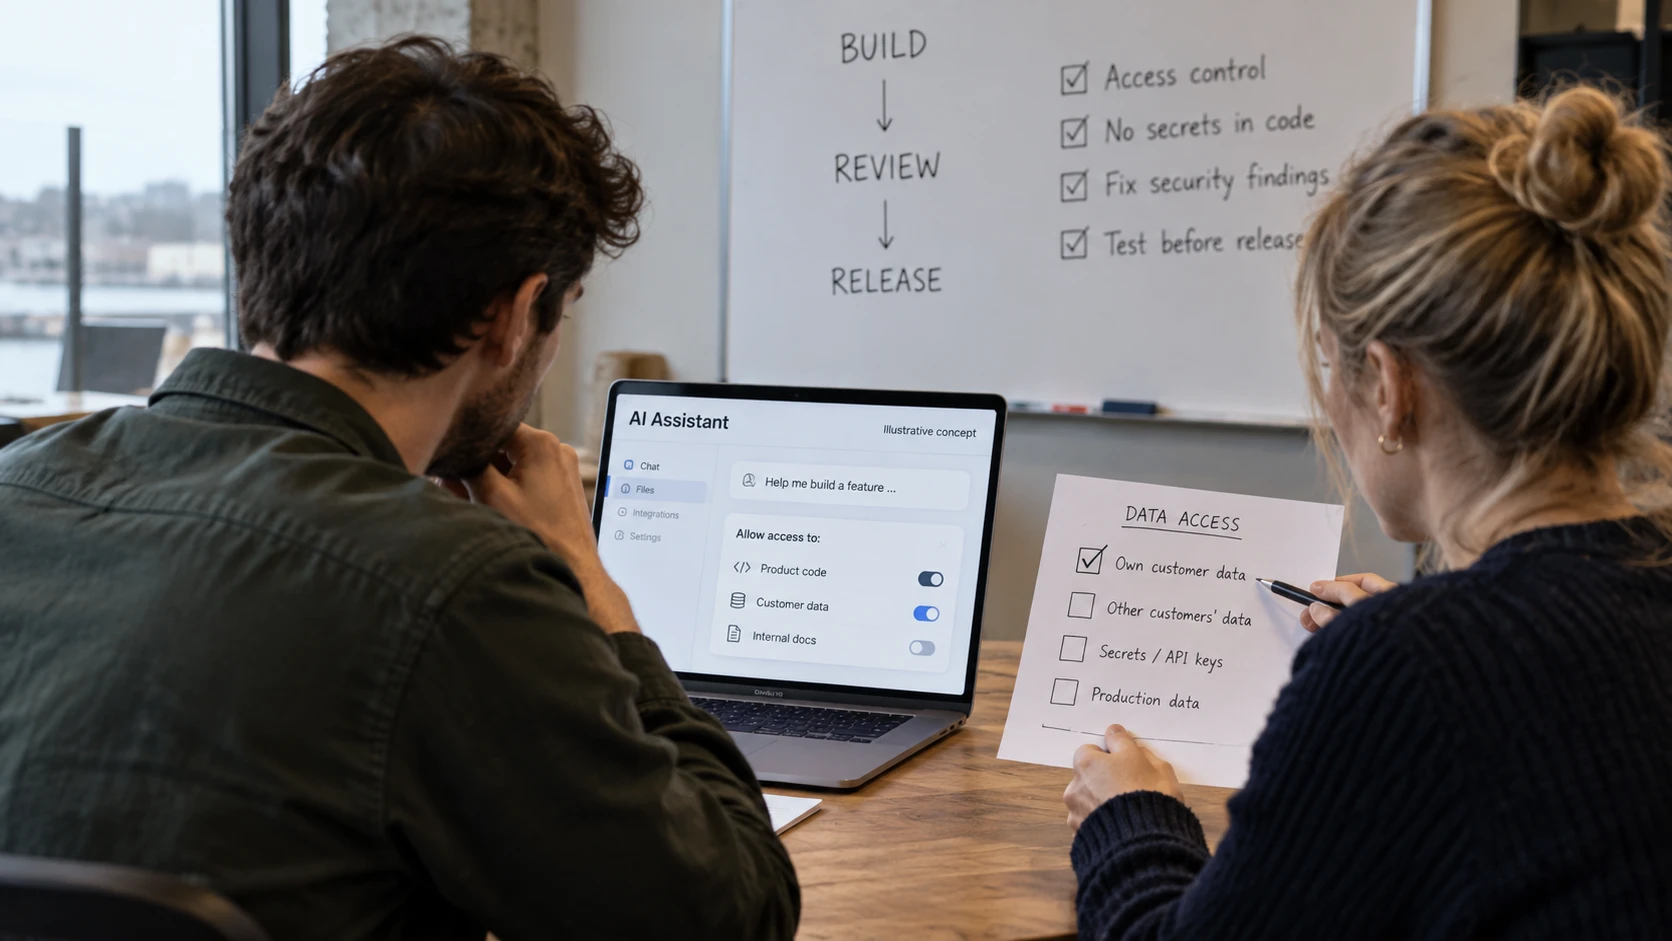
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
Shifter published a commentary by Fredrik Standahl on 14 April 2026 about security in startups using AI to develop software.
The piece argues that faster development still needs a release process that checks what the software can access and expose. Generated code needs review, just as code written by a developer does.
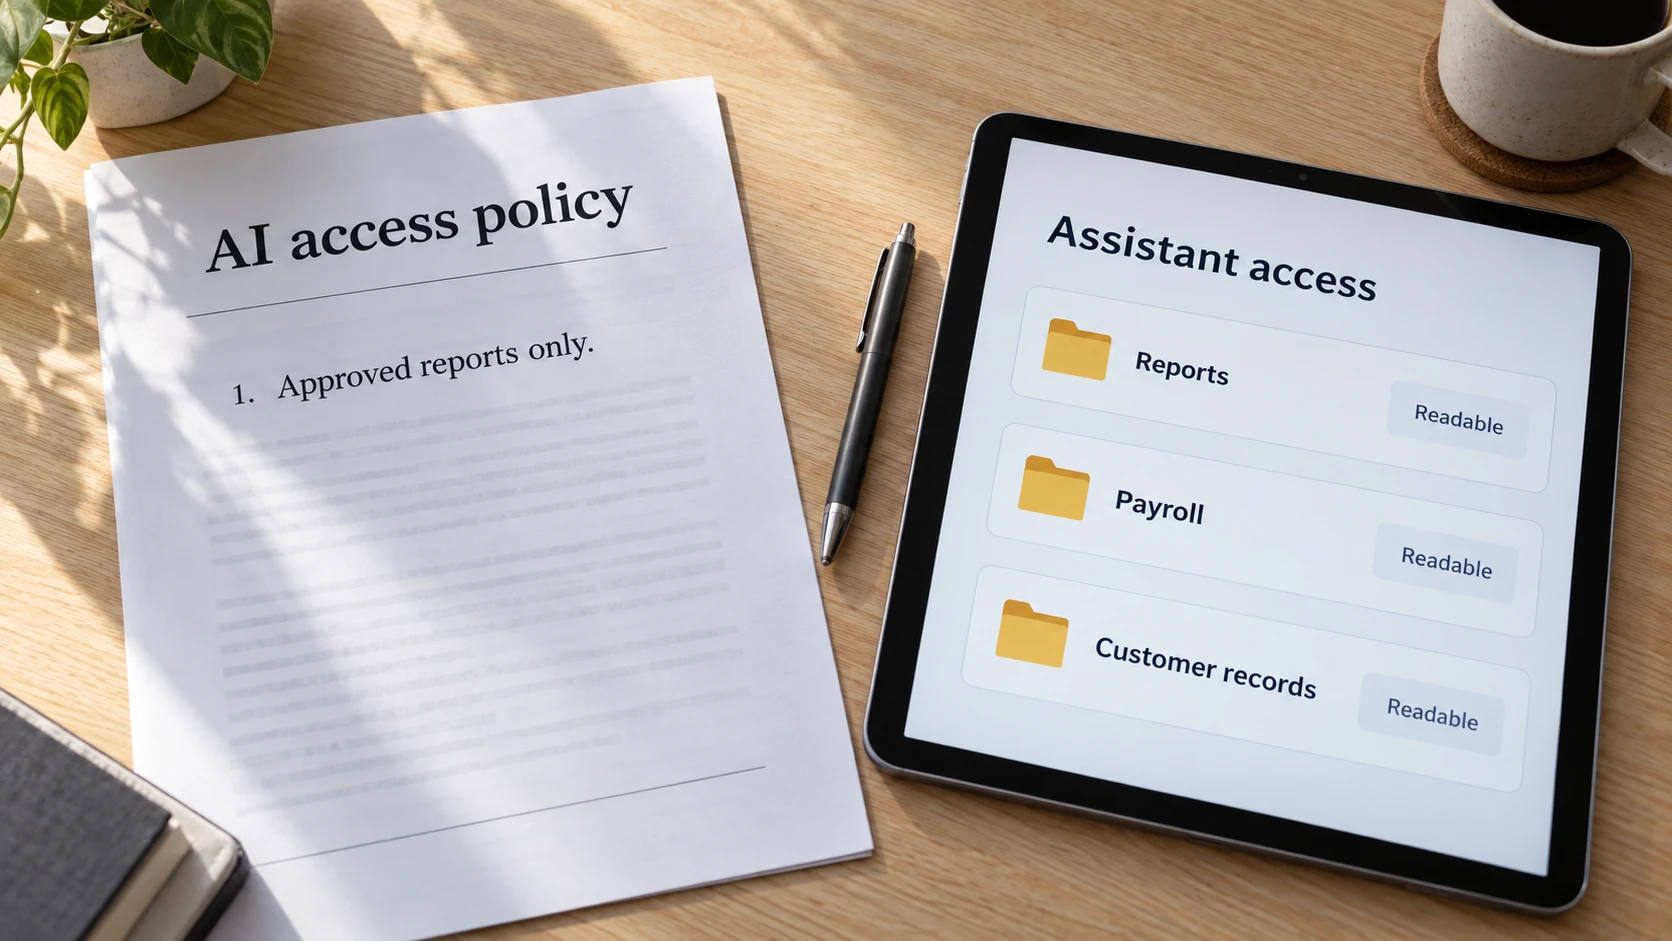
For a startup, the practical questions are concrete: can one customer access another’s records, are secrets kept out of source code, and do security findings get fixed before release? Those checks should be part of building the product.