How Claude helped researchers reach OpenAI accounts through a forum
Hacktron describes Claude-assisted research linking a forum image-upload flaw to OpenAI account access. Here is how the chain worked.
In brief: Hacktron reports using Claude to help develop an attack that reached OpenAI accounts through its forum. The researchers directed the work; this was not a model independently choosing to attack OpenAI.
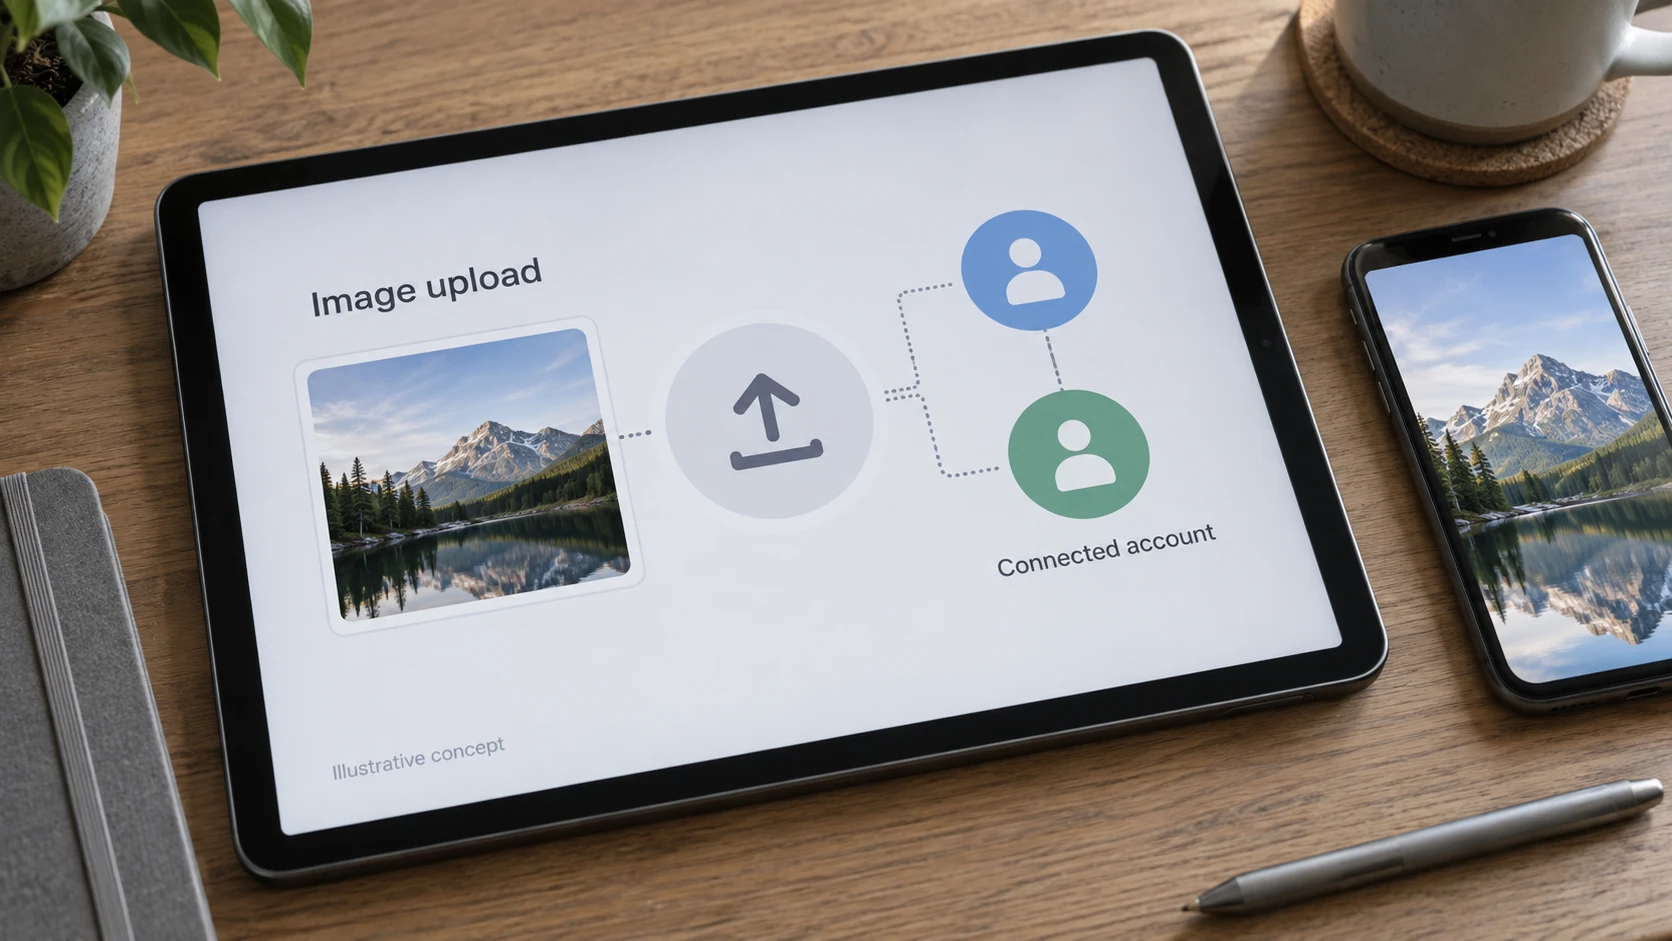
A picture upload became the entry point
Discourse is software for running discussion forums. When someone uploads a picture, the server processes the file so it can display it. That processing is a security boundary: the server is reading data supplied by someone else.
Discourse’s security advisory, published on 28 July, confirms that a flaw in the libheif image-processing library allowed uploaded images to trigger code execution. In plain terms, a specially crafted image could make the server run an attacker’s instructions.
Discourse supplied a patched library and additional isolation for image processing on supported systems. Isolation limits what a vulnerable process can reach.
Why forum access mattered
Hacktron’s report, published on 13 September, describes July research: Claude helped develop the exploit, and a separate OpenAI sign-in flaw opened access to ChatGPT and Codex accounts. The researchers report demonstrating access to an internal GitHub repository through Codex. They say OpenAI fixed its issue in July.
Single sign-on lets one identity sign into several services. A connected tool may also act with permissions granted to that account. Those relationships help explain why the impact of a compromised account can extend beyond its original application.
What this says about AI hacking
The distinction between generating attack code and carrying out actions with tools matters. A model’s contribution must be described alongside the human decisions and access it depends on. Here, the reported result concerns a guided research effort, not evidence that any chatbot can break into any business.