Falcon Guardian: putting limits on what AI agents can do
CrowdStrike is extending AI security into agent activity. Here is what Guardian adds and what we would check before a rollout.
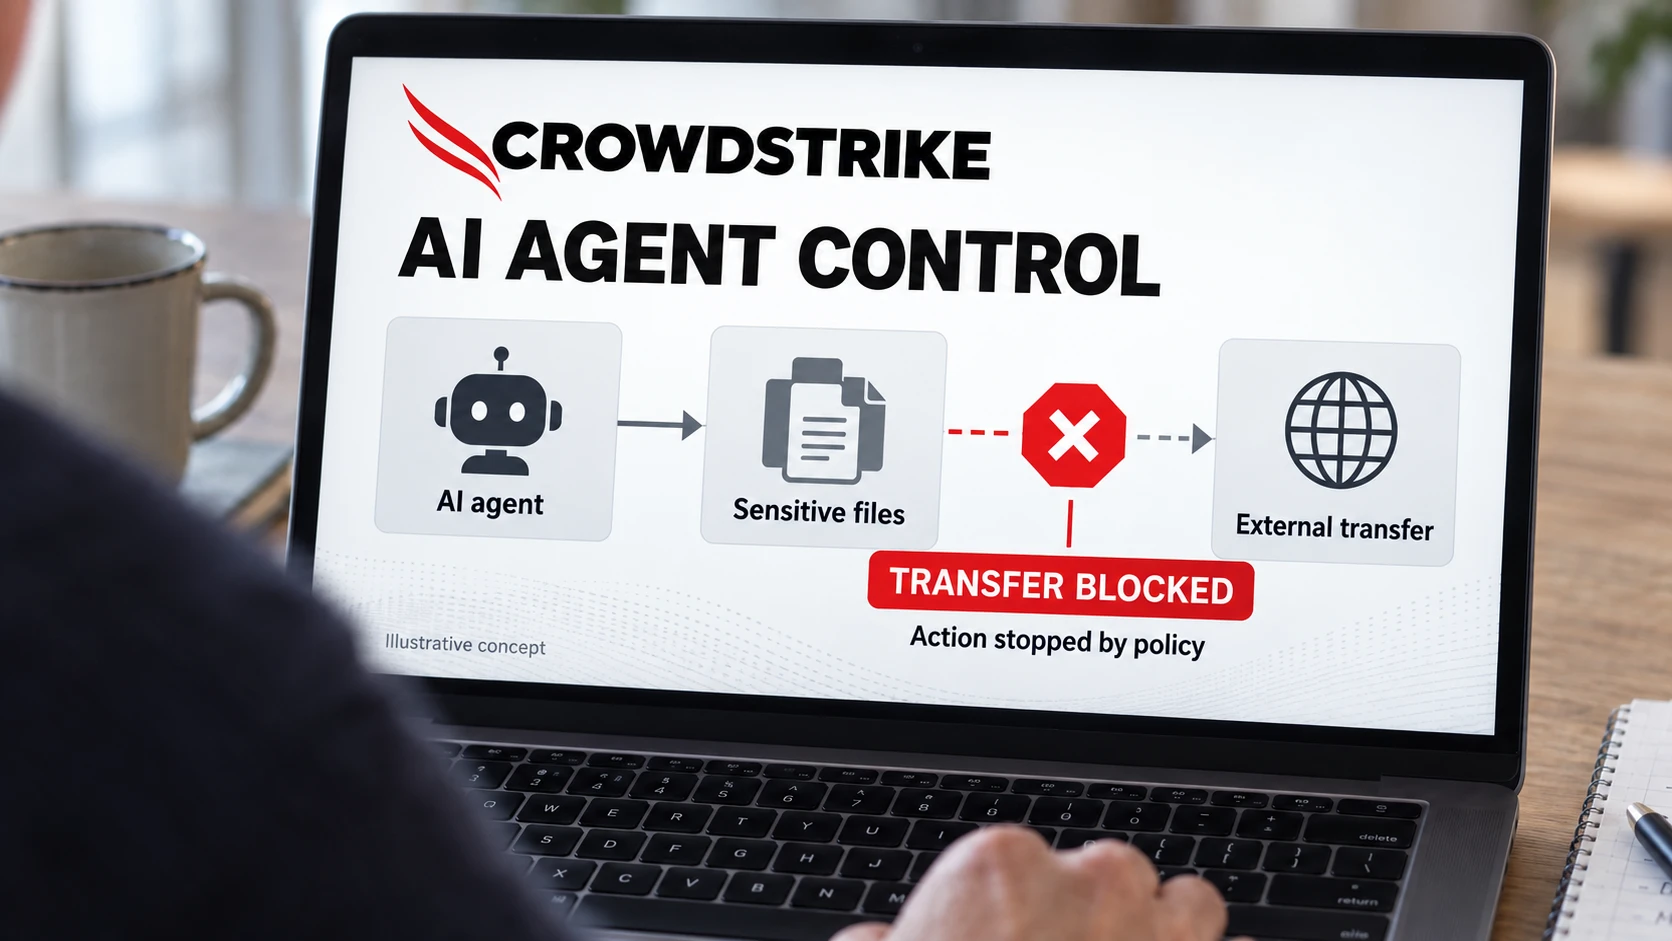
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
An AI agent with access to files, credentials and a command line needs boundaries you can enforce. Knowing that it is running helps. Being able to stop an unwanted action is the harder part.
CrowdStrike introduced Falcon Guardian on 1 September 2026 to address that problem. Its announced capabilities include agent discovery, visibility into agent actions, access controls and runtime detection and response.
For a business already using Falcon, the useful question is specific: which of our agents does it cover, and what can it stop?
Follow the action, not just the prompt
Consider an assistant asked to summarise a project folder. If it can also read customer records and send files to an external service, its access extends beyond the task. A harmless request does not make every subsequent action harmless.
That is why we would assess the whole workflow: the user, the agent, its credentials, the tools it calls and the data those tools can reach. A log of the conversation may explain the request without showing everything that happened afterwards.
CrowdStrike describes Guardian as the evolution of Falcon AIDR, retaining its existing AI protection capabilities while extending control over agent execution. It would be inaccurate to describe the earlier product as a logging tool with no response capabilities.
The distinction matters when planning an upgrade. Start with your current configuration and identify the additional control you need.
Separate the release from the roadmap
The September announcement includes services and features with different availability dates. CrowdStrike’s launch blog places the managed response service later in Q3 and the AI gateway in Q4, with the gateway in pre-beta at announcement. These are the vendor’s stated plans, not delivery guarantees.
Before procurement, get written confirmation of the supported agents, operating systems, licences and available features for your deployment. A capability listed on a product page does not establish that it covers every workflow in your business.
Test a workflow your people use
We would begin with a small group of machines and a familiar task. Agree what the agent may read, change and send. Then try both a permitted action and an action that should be blocked.
Check the result from both sides. Can the employee finish legitimate work? Can the security team see why an action was stopped, which identity was involved and what happened before the alert?
Shadow AI discovery is a useful starting point, but the inventory needs an access review alongside it. An approved agent can still have excessive permissions.
Finally, decide who handles a blocked action. Some cases will need a legitimate exception; others will require access to be withdrawn. That decision needs an owner with the authority to act, including outside office hours. The value of Guardian should be demonstrated in that working arrangement, not inferred from the product name.