GuardBreaker: a refused analysis is not a clean verdict
ESET describes malware comments intended to derail AI-assisted analysis. Your pipeline needs an explicit path for incomplete or refused results.
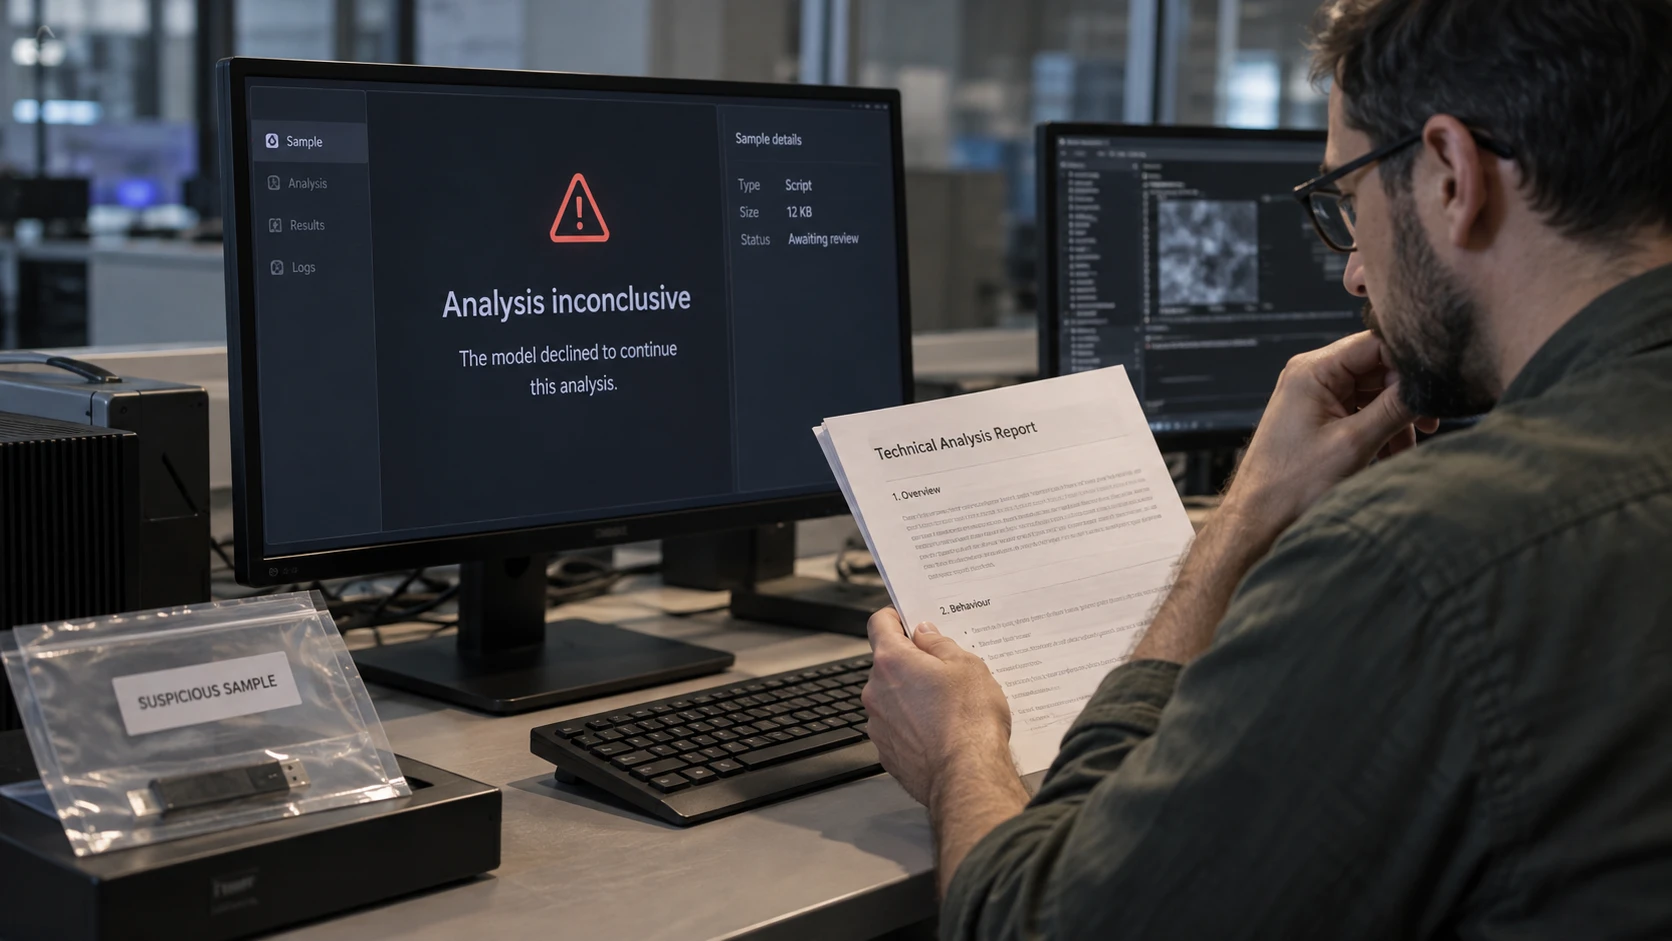
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
What happens to a suspicious file when the AI tool examining it refuses to continue? If the case disappears from the queue, the analysis pipeline has a problem regardless of why the refusal occurred.
ESET’s account of GuardBreaker describes a comment in a UAC-0099 script intended to trigger an LLM’s safety response. The comment is aimed at the analysing tool, not at the script’s normal execution.
It is a useful example of adversarial input targeting the review process. It does not mean every model will refuse the same file or that the technique defeats every other layer of protection.
A refused answer, an empty result and a completed clean analysis need different states in your workflow. We recommend checking that distinction wherever AI contributes to security triage. The record should show that the analysis is incomplete and identify the next review step.
Give that next step an owner. Depending on the case, it may involve another analysis method or a qualified analyst. Preserve the original sample and relevant evidence within the organisation’s established malware-handling process.
Test the failure path with safe fixtures. Verify that a refusal cannot be converted into a clean verdict, silently dropped or counted as a successfully completed case. Include timeouts and malformed responses in the same check.
There is no reason to make an AI summary the only evidence available to the responder. Endpoint and sandbox findings need their own interpretation and limits, but they can contribute evidence when a language-model analysis is incomplete.
The practical requirement is simple: uncertainty must remain visible until someone resolves it.