What ISO 27001 costs, and what drives the price
Compare ISO 27001 proposals on implementation, internal time, tools, audit fees and ongoing maintenance. Scope matters more than an unsupported headline price.
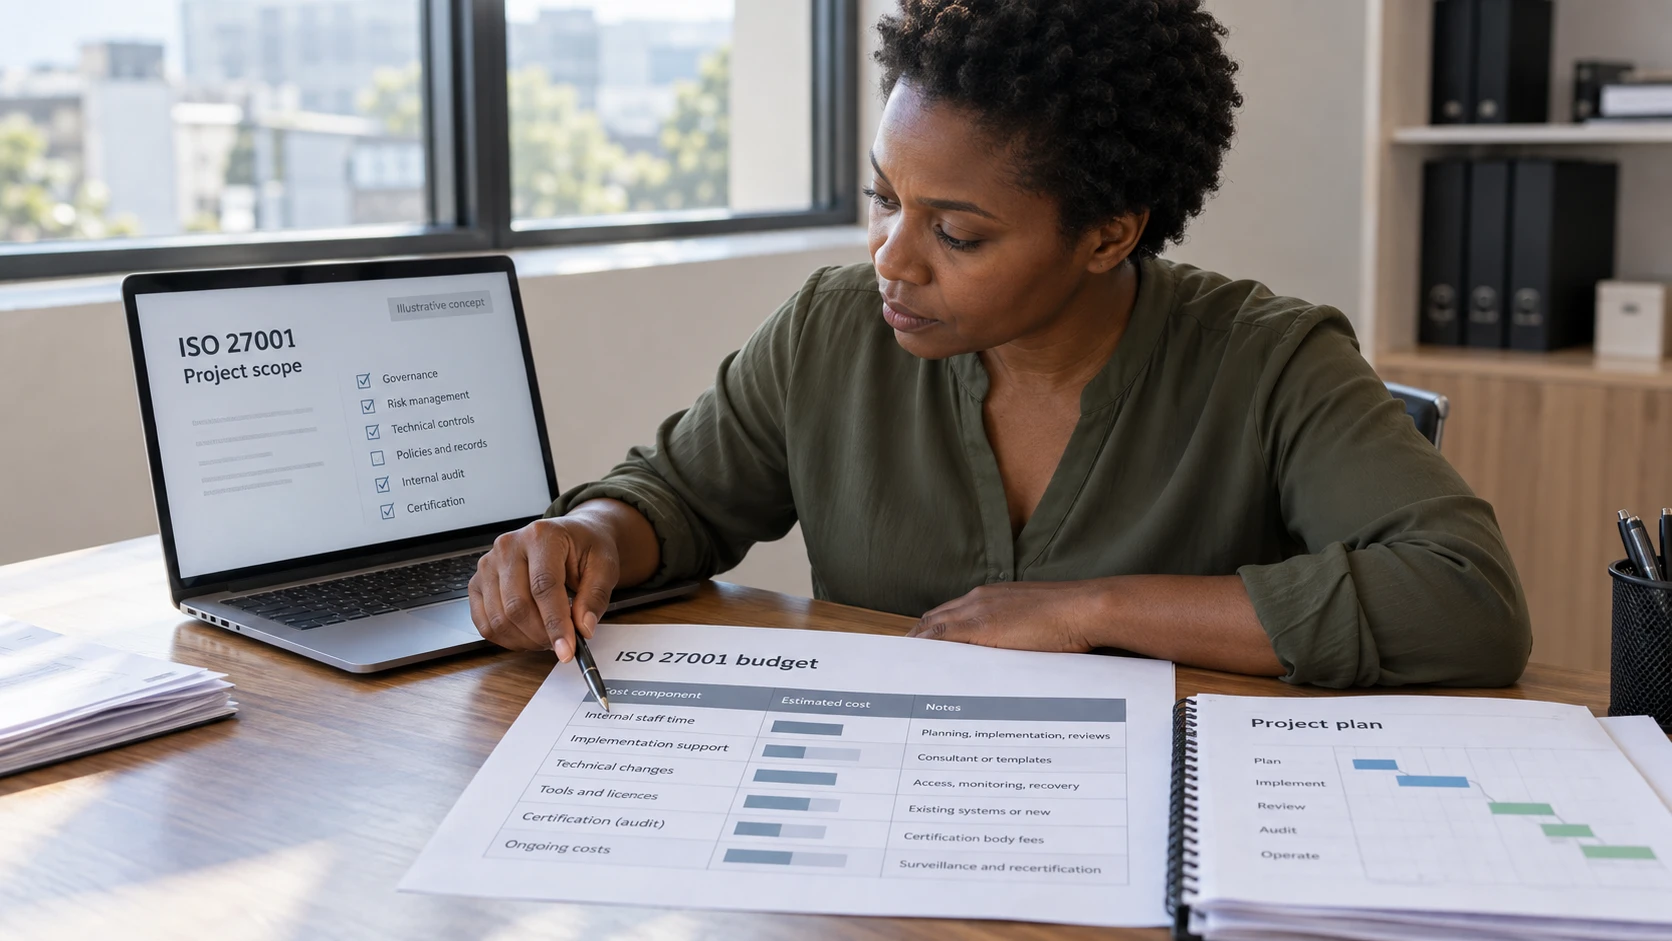
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
An ISO 27001 quote is only comparable with another quote when both cover the same work. A low implementation fee may exclude the audit, the tools and much of your team’s time.
Build the budget around scope and existing capability. The useful question is what the organisation must change to operate the management system, then what it will cost to keep it working.
Separate the cost components
Internal work. Managers, system owners and staff need time for decisions, implementation, reviews and the audit. An external consultant cannot supply all the knowledge about how the business operates.
Implementation support. Clarify whether the provider writes and implements with you, reviews work your team produces or supplies templates. These are different services.
Technical changes. The risk assessment may identify a need for better access controls, recovery capability or monitoring. Existing tools may cover some of it. ISO 27001 does not mandate a particular vendor.
Records and workflow. A GRC platform can help organise evidence, but buying one is not a requirement in itself. Evaluate whether existing systems can maintain controlled documents, risk records and audit trails adequately.
Certification. Ask the certification body for its own scope and fee breakdown. Audit duration depends on the organisation and complexity; the relevant accreditation framework is ISO/IEC 27006-1.
Budget beyond the initial certificate
Include recurring control work, licence renewals, surveillance and eventual recertification. Ask how an acquisition, new office or additional product would affect scope and price.
A subscription may combine several costs, while a project proposal lists them separately. Neither format tells you whether the total is complete.
Before signing, resolve four points: what is excluded, what effort is expected from your staff, who owns the documents and records, and what happens at contract exit. If there is a guarantee, identify the covered costs and conditions in writing.
Secured by FM CyberSecurity packages security operations and certification preparation as a subscription. Dedicated ISO 27001 support is another route. Compare either option against the same scope and ongoing responsibilities so the budget reflects the work your business actually needs.