How long does ISO 27001 take?
The ISO 27001 timeline depends on your starting point, the controls you need to implement and the certification body's audit schedule.
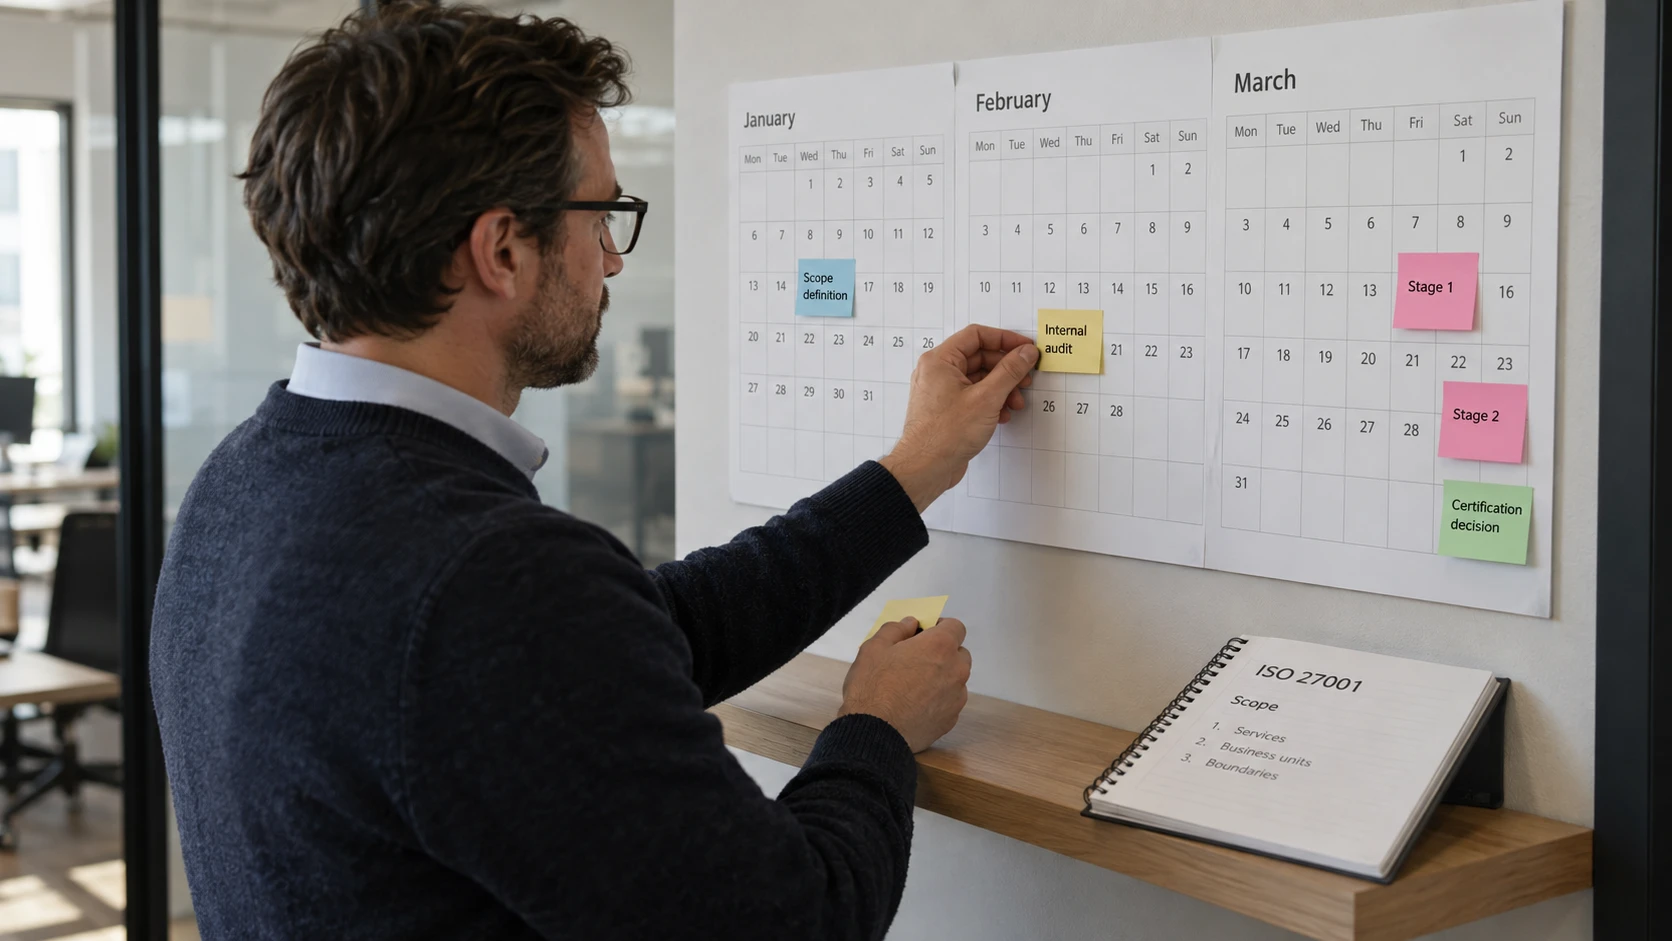
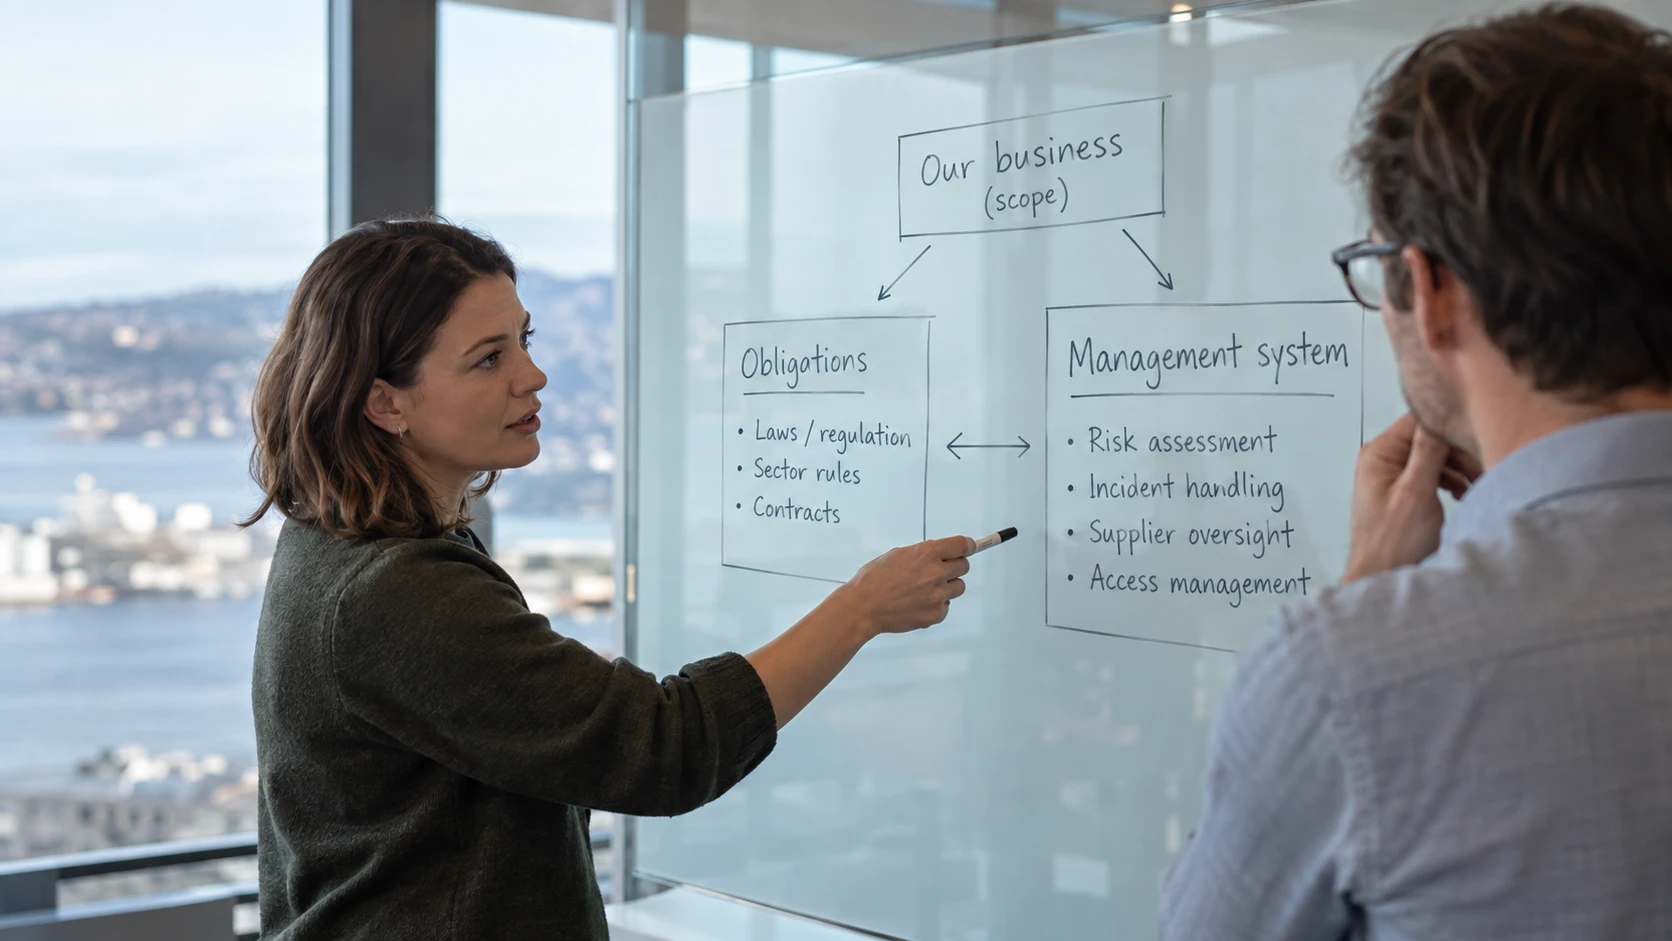
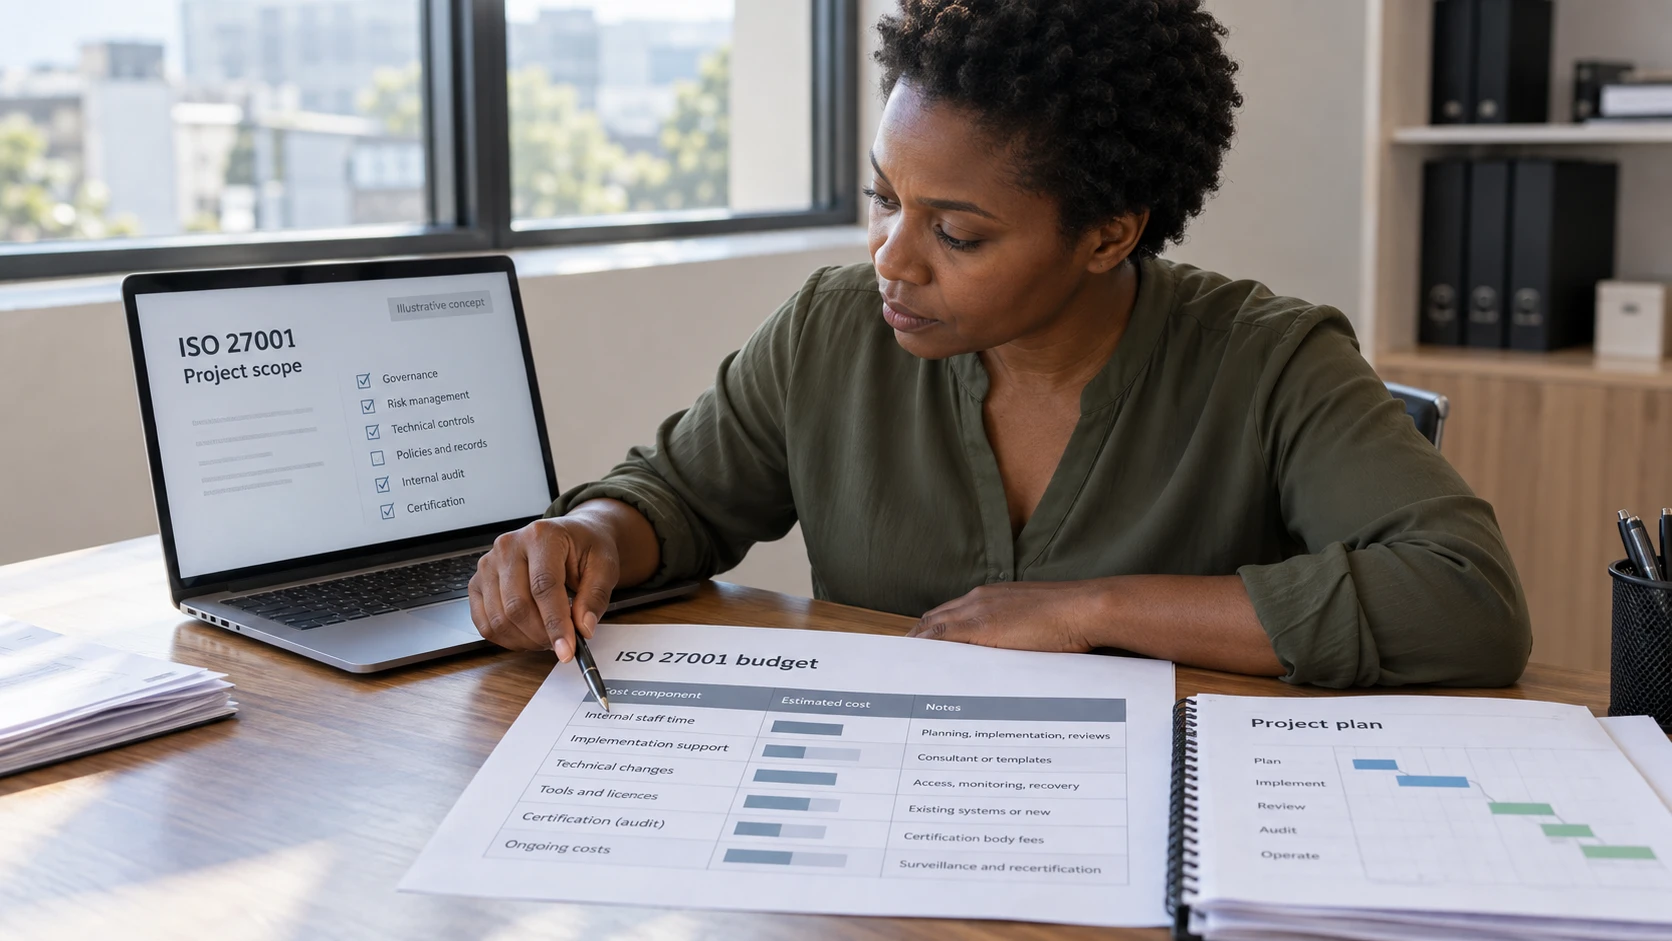
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
There is no reliable ISO 27001 timeline without a scope and a starting-point assessment. A business with established controls has different work ahead of it from one that must introduce access management, supplier reviews and recovery procedures.
Plan against the date you need the certificate, then separate preparation, audit and the certification decision. A consultant’s readiness date is not the date a certification body will issue a certificate.
Find the work that sets the pace
Start with the services and business units the certificate must cover. Identify the controls already operating, the evidence available and the gaps that require changes.
Some tasks can run together: drafting policies, collecting an asset inventory and selecting a certification body. Others depend on earlier work. You cannot meaningfully assess a control’s operation before it has been implemented.
Reserve time from the people who approve risks, manage systems and own supplier relationships. Quick decisions help, but they cannot substitute for deploying a missing control or demonstrating that a process works.
Put the audit on the calendar early
Ask an accredited certification body for its proposed schedule and evidence expectations. Certification normally includes a Stage 1 assessment of readiness and a Stage 2 assessment of implementation and effectiveness, followed by a certification decision. Leave room to address findings. SGS describes this certification cycle.
An internal audit and management review also need planning. The organisation must have enough evidence for those activities to be useful; an empty template with a meeting date is not preparation.
If the tender deadline is fixed, ask the buyer whether it requires an issued certificate or will accept other evidence. Do that before committing to a date you do not control.
Make a short readiness estimate testable
If an offer proposes readiness in a few weeks, ask what it assumes: existing controls, a narrow scope, available staff and access to records. Define what “ready” includes and how gaps will change the plan.
Secured by FM CyberSecurity combines security operations and certification preparation. Any project schedule needs to be agreed against the organisation’s actual scope and responsibilities.
Build an ongoing calendar too. Reviews, corrective actions and external surveillance continue after initial certification. The ISO 27001 checklist sets out the work that needs an owner throughout the cycle.