Compliance
Practical analysis of ISO 27001, NIS2, and DORA, the way we deliver them to Nordic organisations.
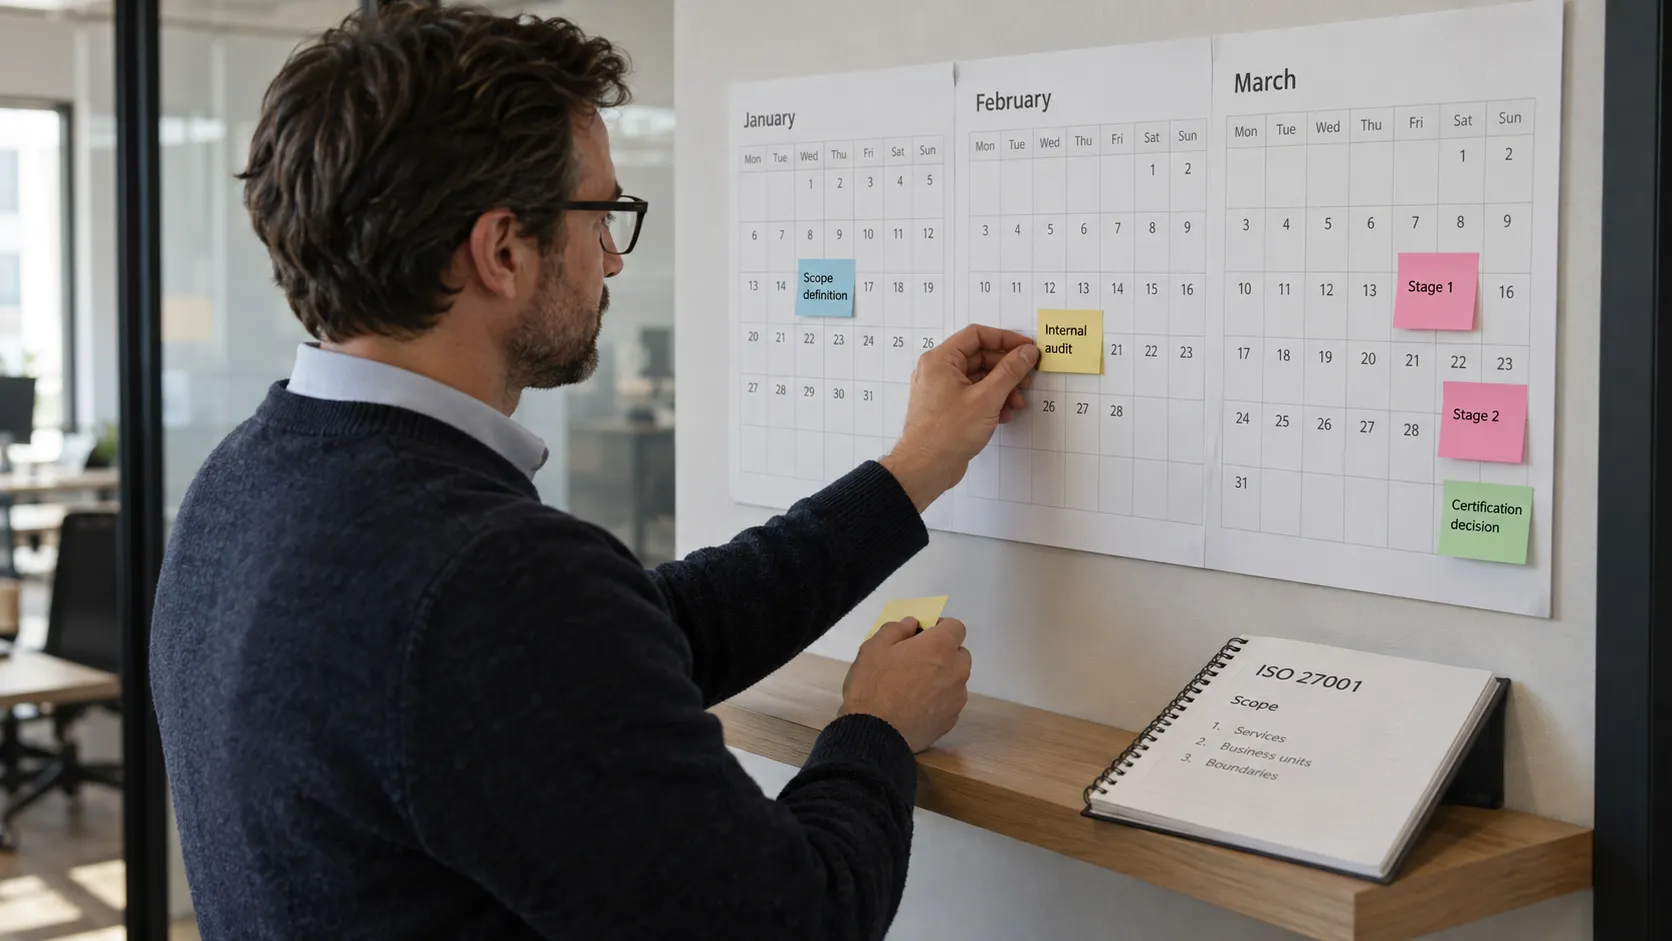
The ISO 27001 timeline depends on your starting point, the controls you need to implement and the certification body's audit schedule.
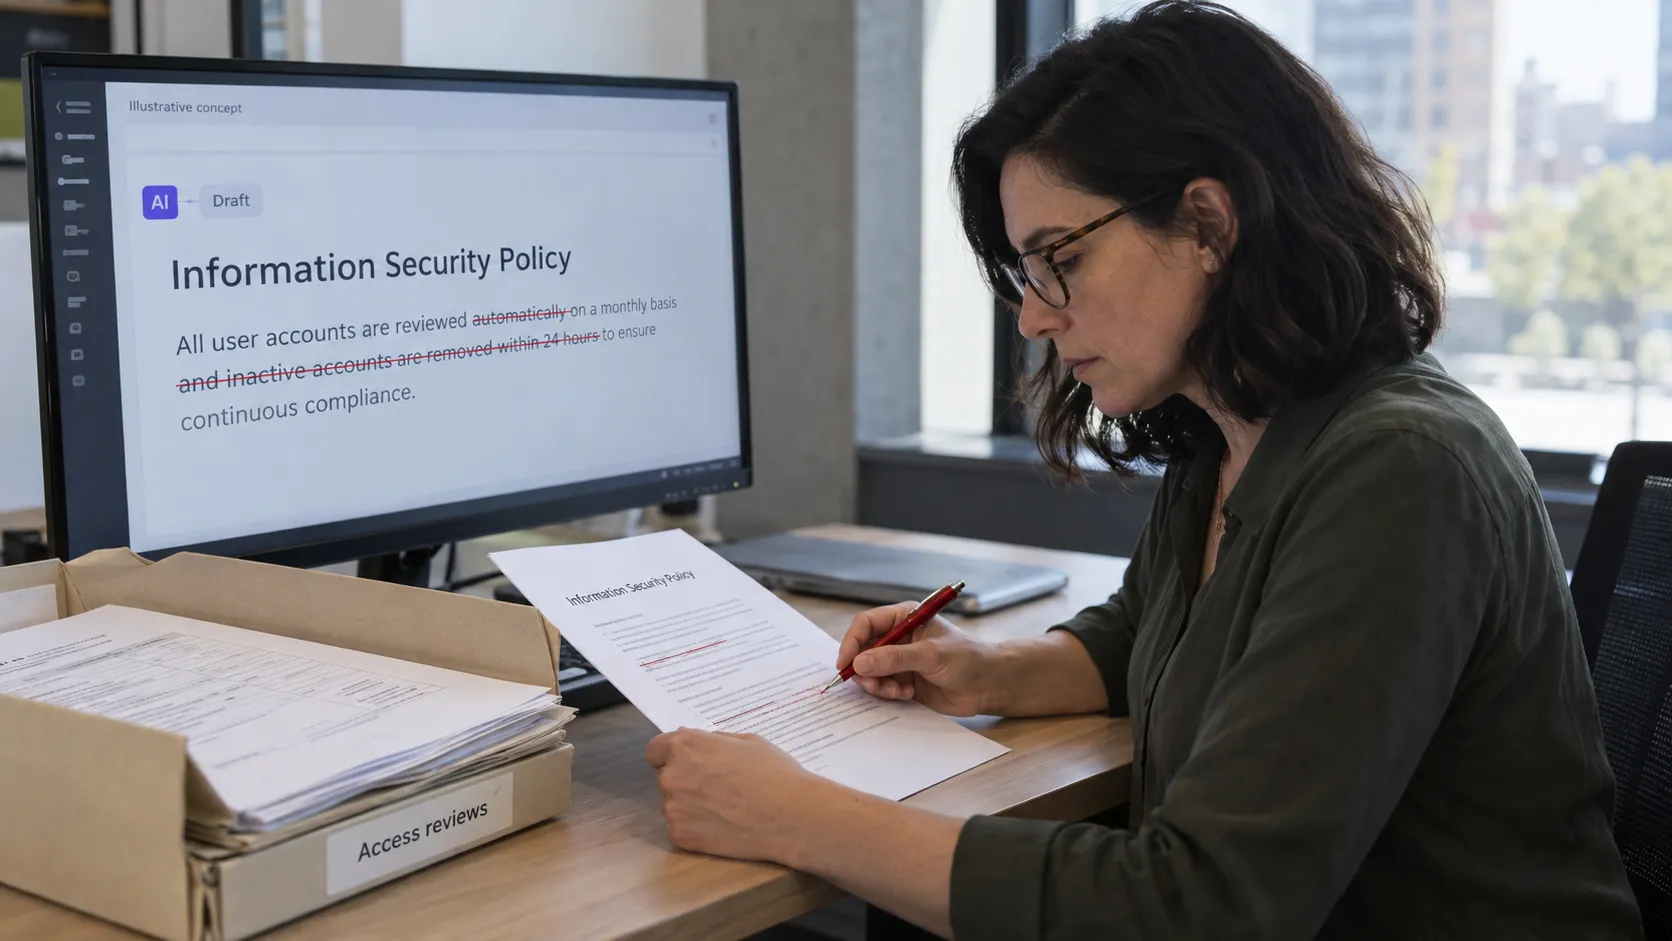
AI can help draft policies and organise evidence. People still need to make risk decisions, implement controls and verify that the records describe reality.
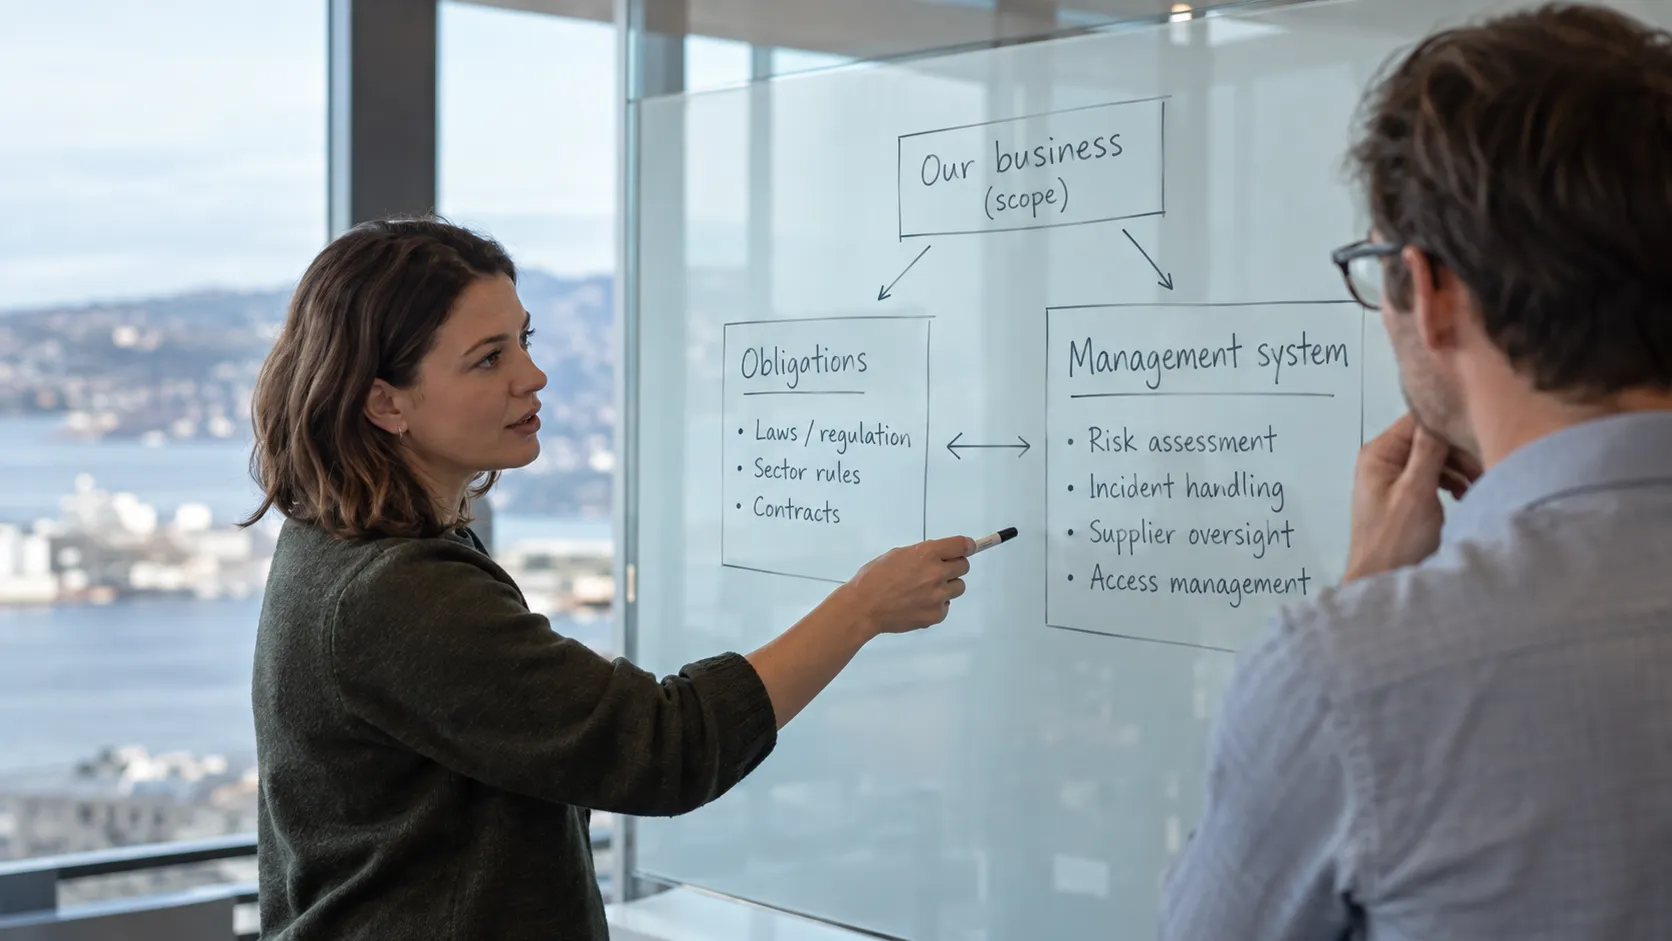
Build shared security processes, but track legal duties and certification separately. Applicable legal deadlines take priority over commercial preferences.
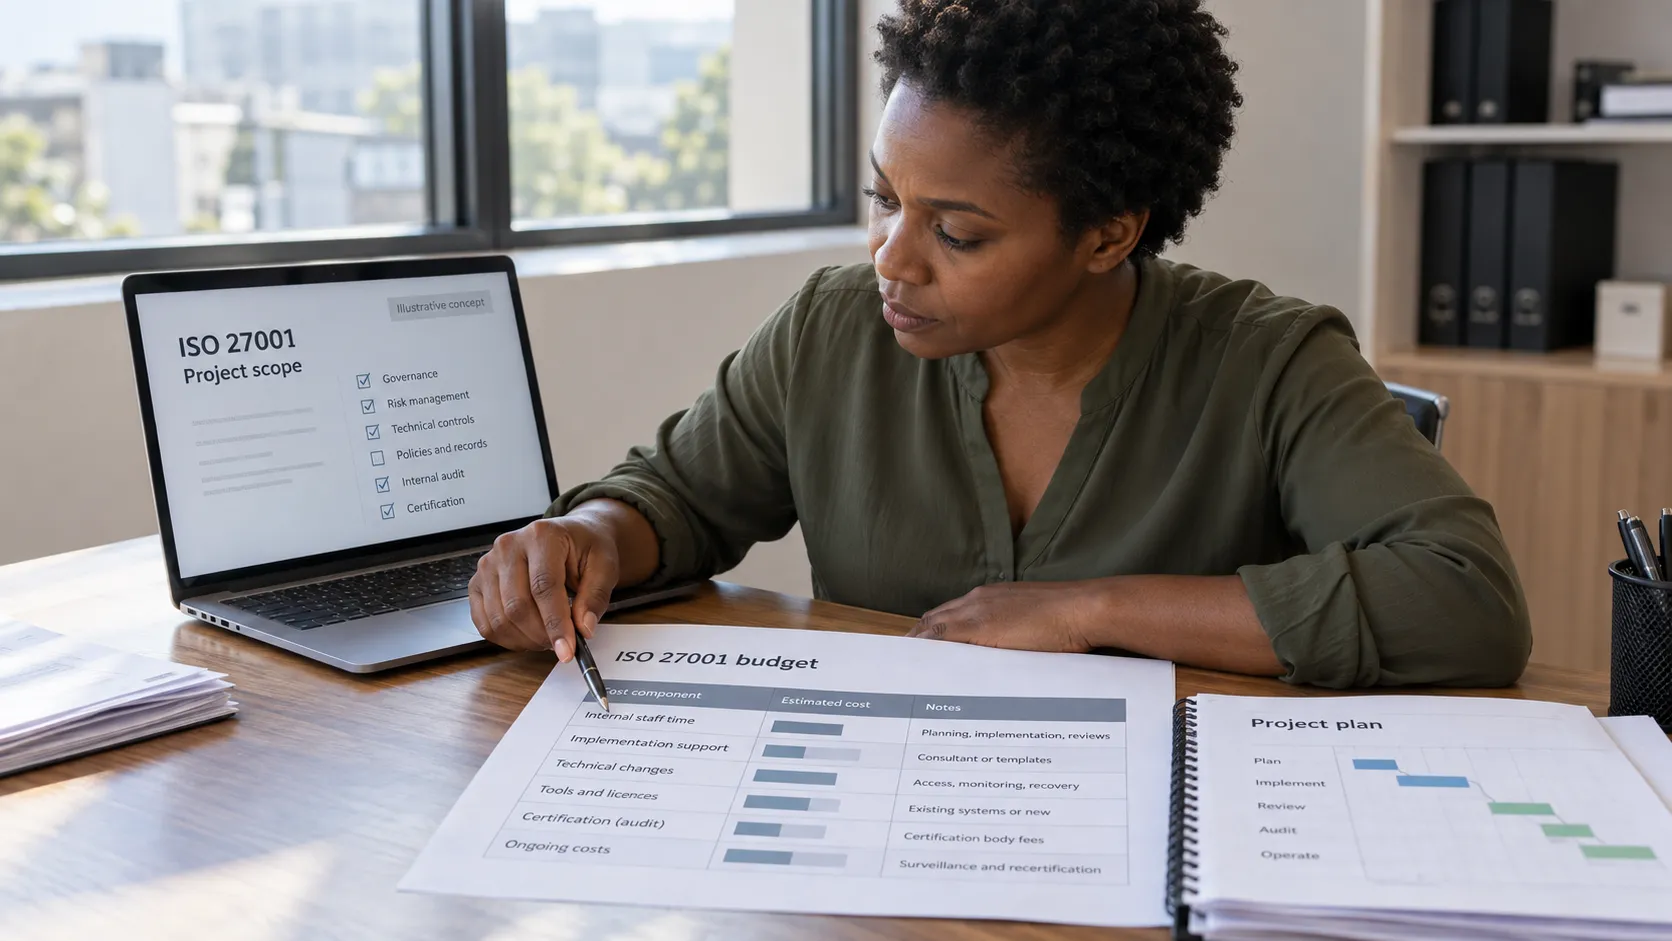
Compare ISO 27001 proposals on implementation, internal time, tools, audit fees and ongoing maintenance. Scope matters more than an unsupported headline price.
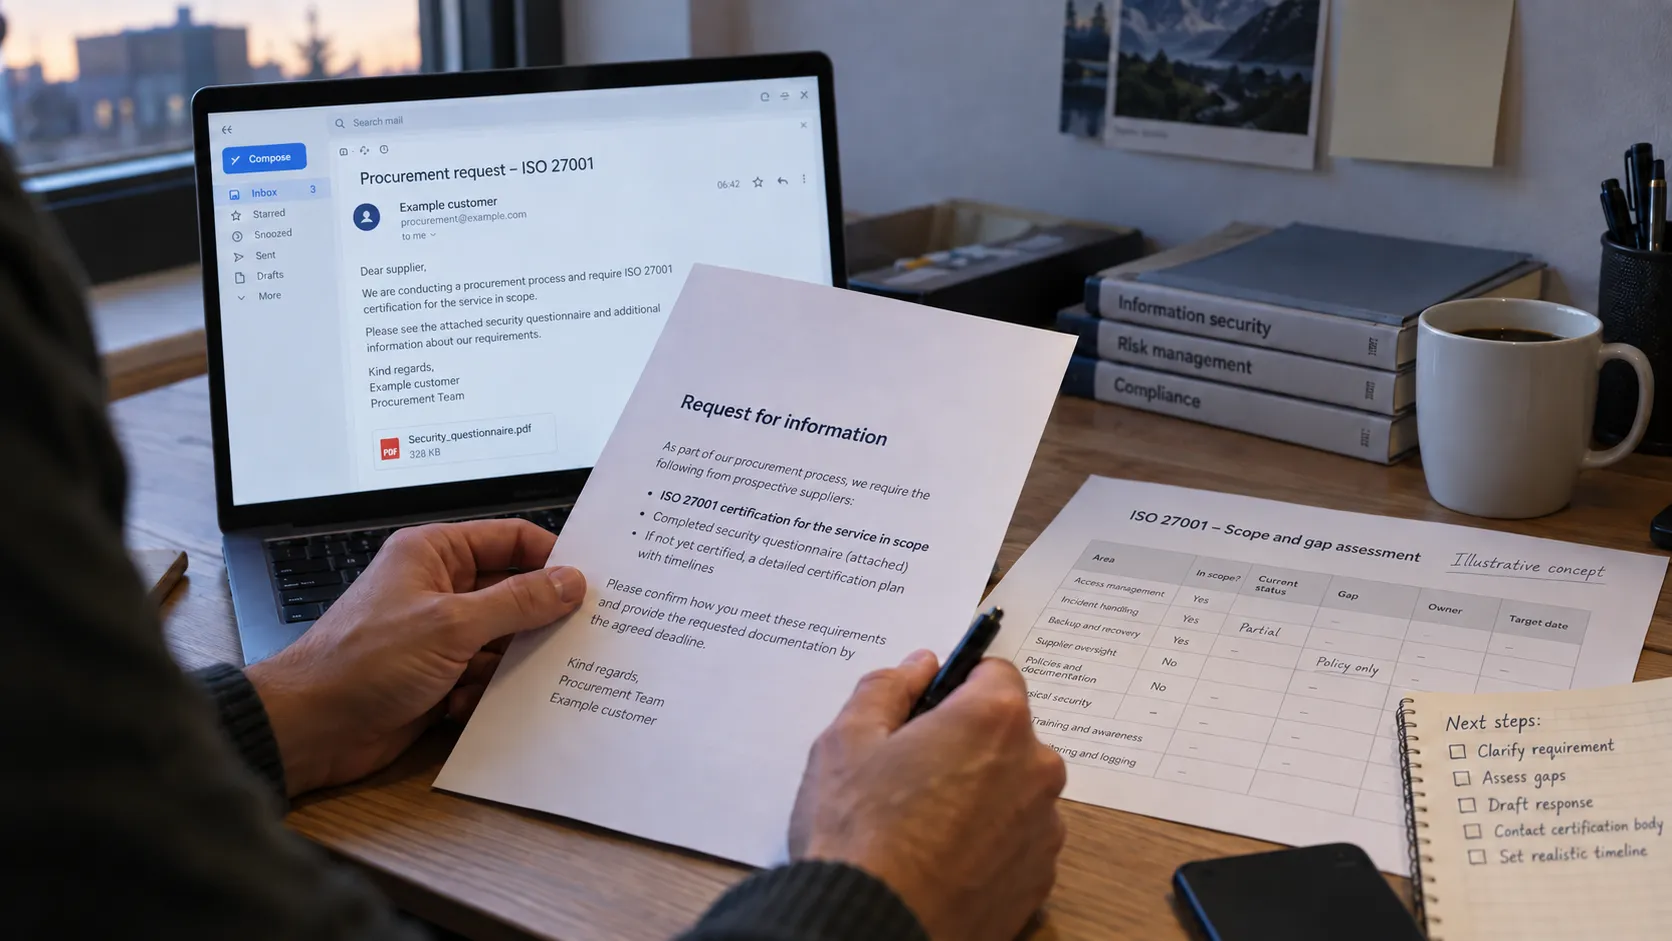
Clarify the certificate scope, deadline and acceptable evidence before promising a date. Then assess the gaps and agree a credible plan.
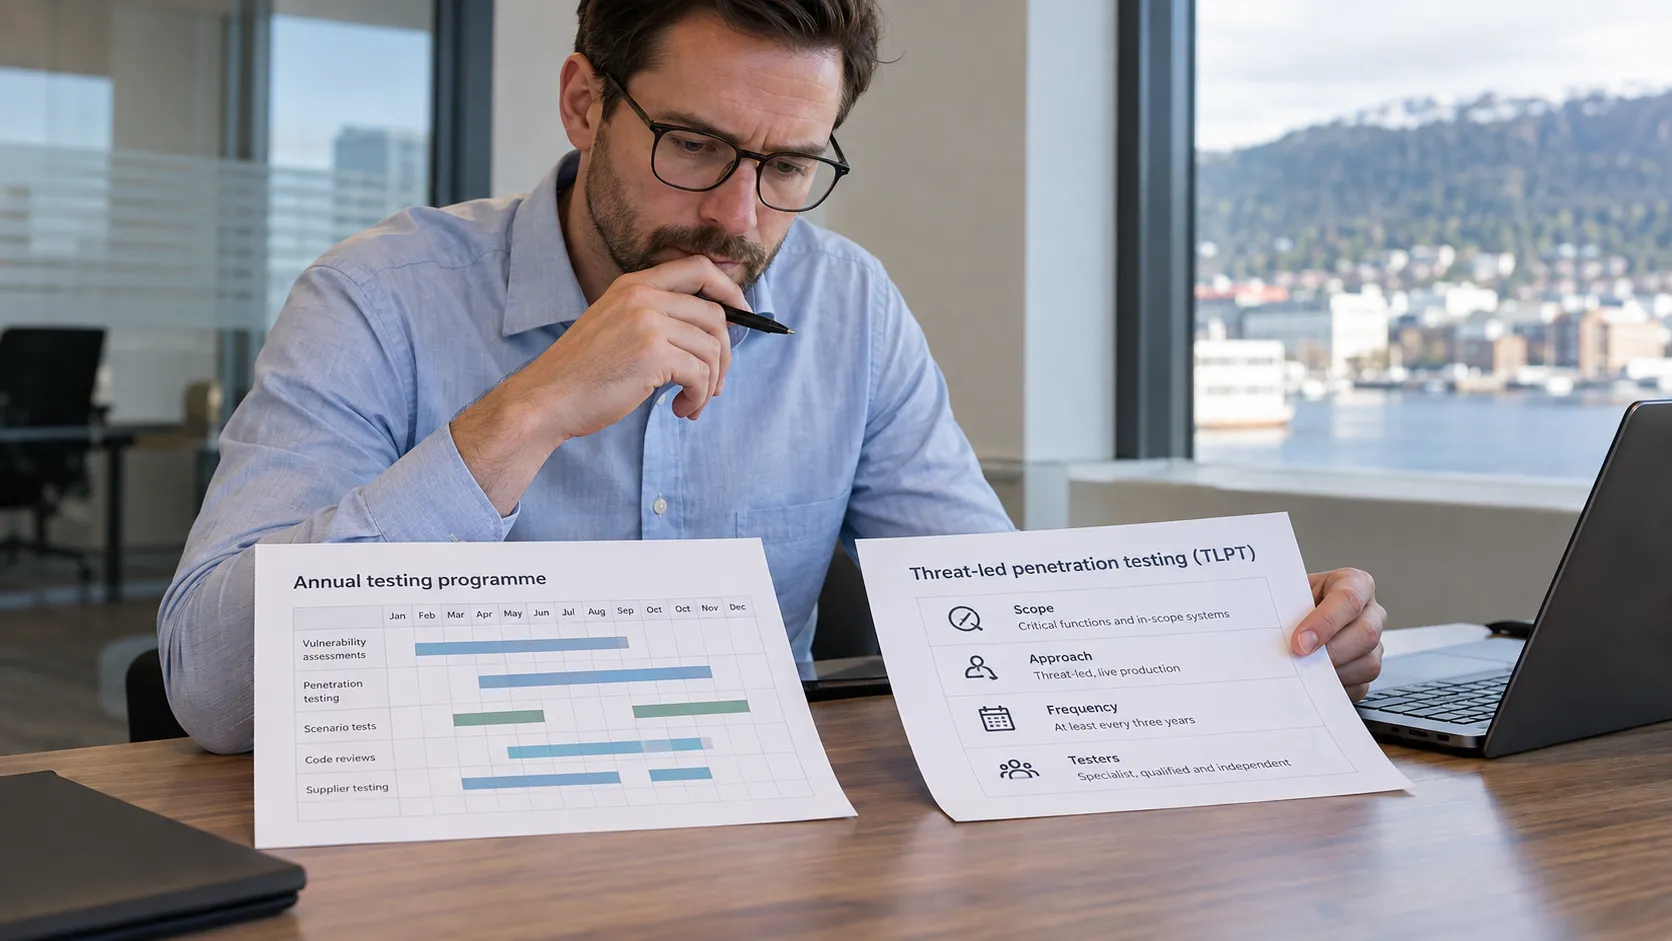
DORA distinguishes general resilience testing from designated TLPT. Choose methods against risk, document coverage and verify remediation.
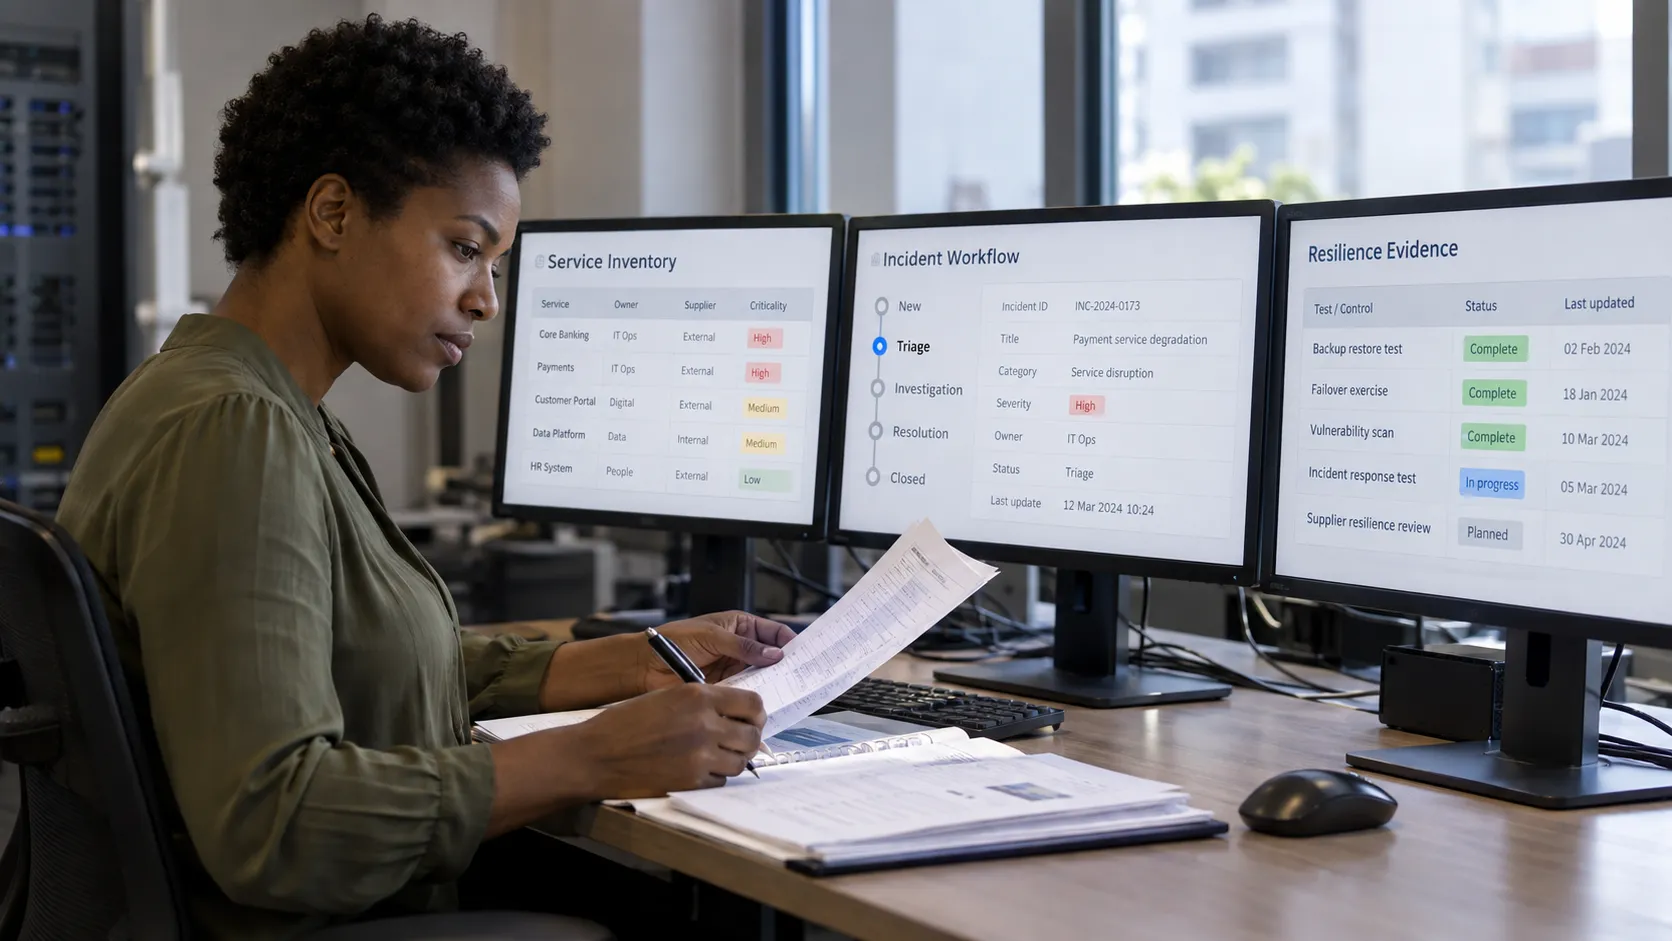
Software can organise registers, evidence and technical findings. Choose it around the decisions, data and responsibilities in your DORA programme.
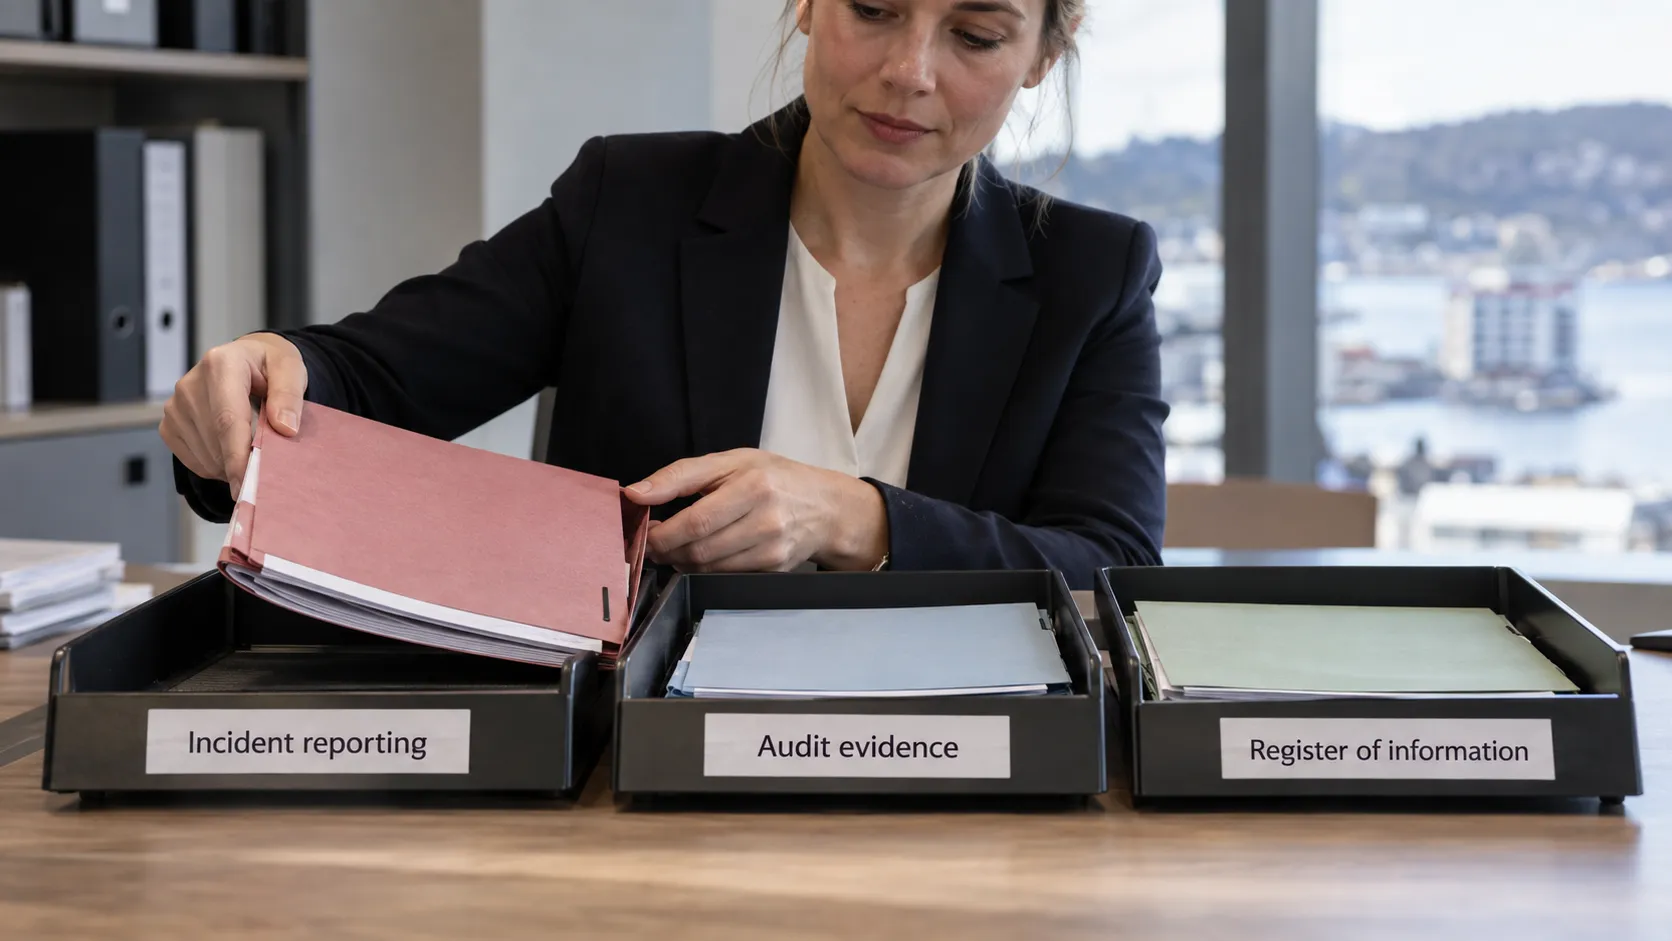
The ICT agreement register, planned-contract notices, incident reports and internal audit have different purposes. Assign owners and use the current submission rules.
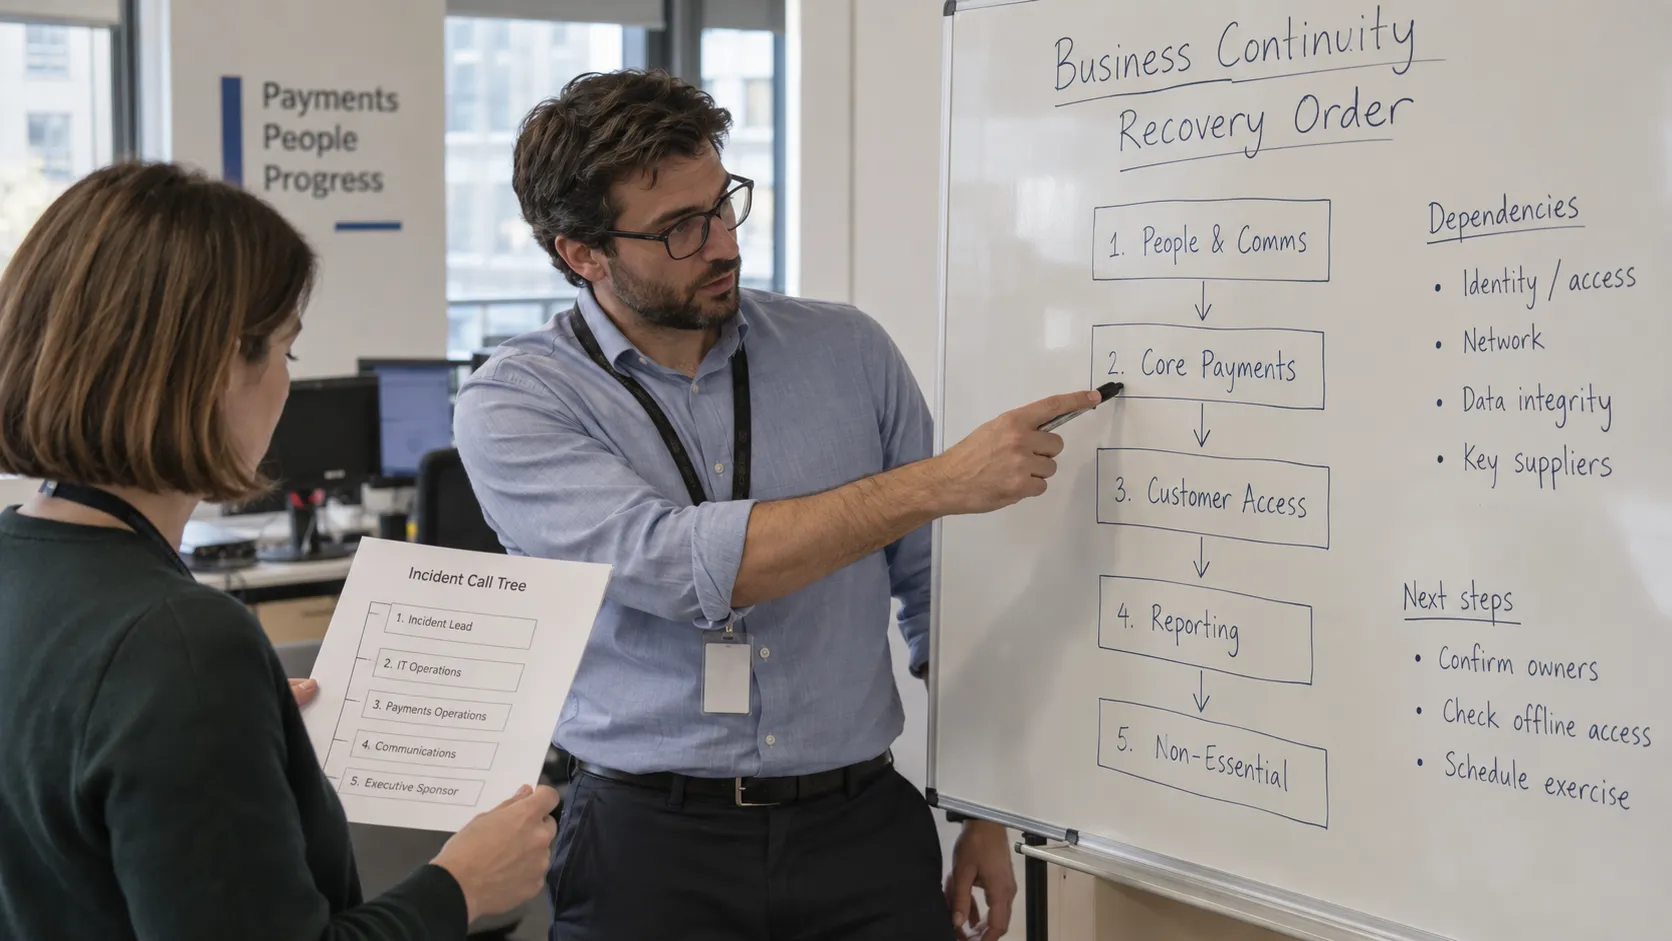
Continuity plans should follow the services the firm must sustain. Map dependencies, set recovery objectives and exercise the decisions as well as the technology.
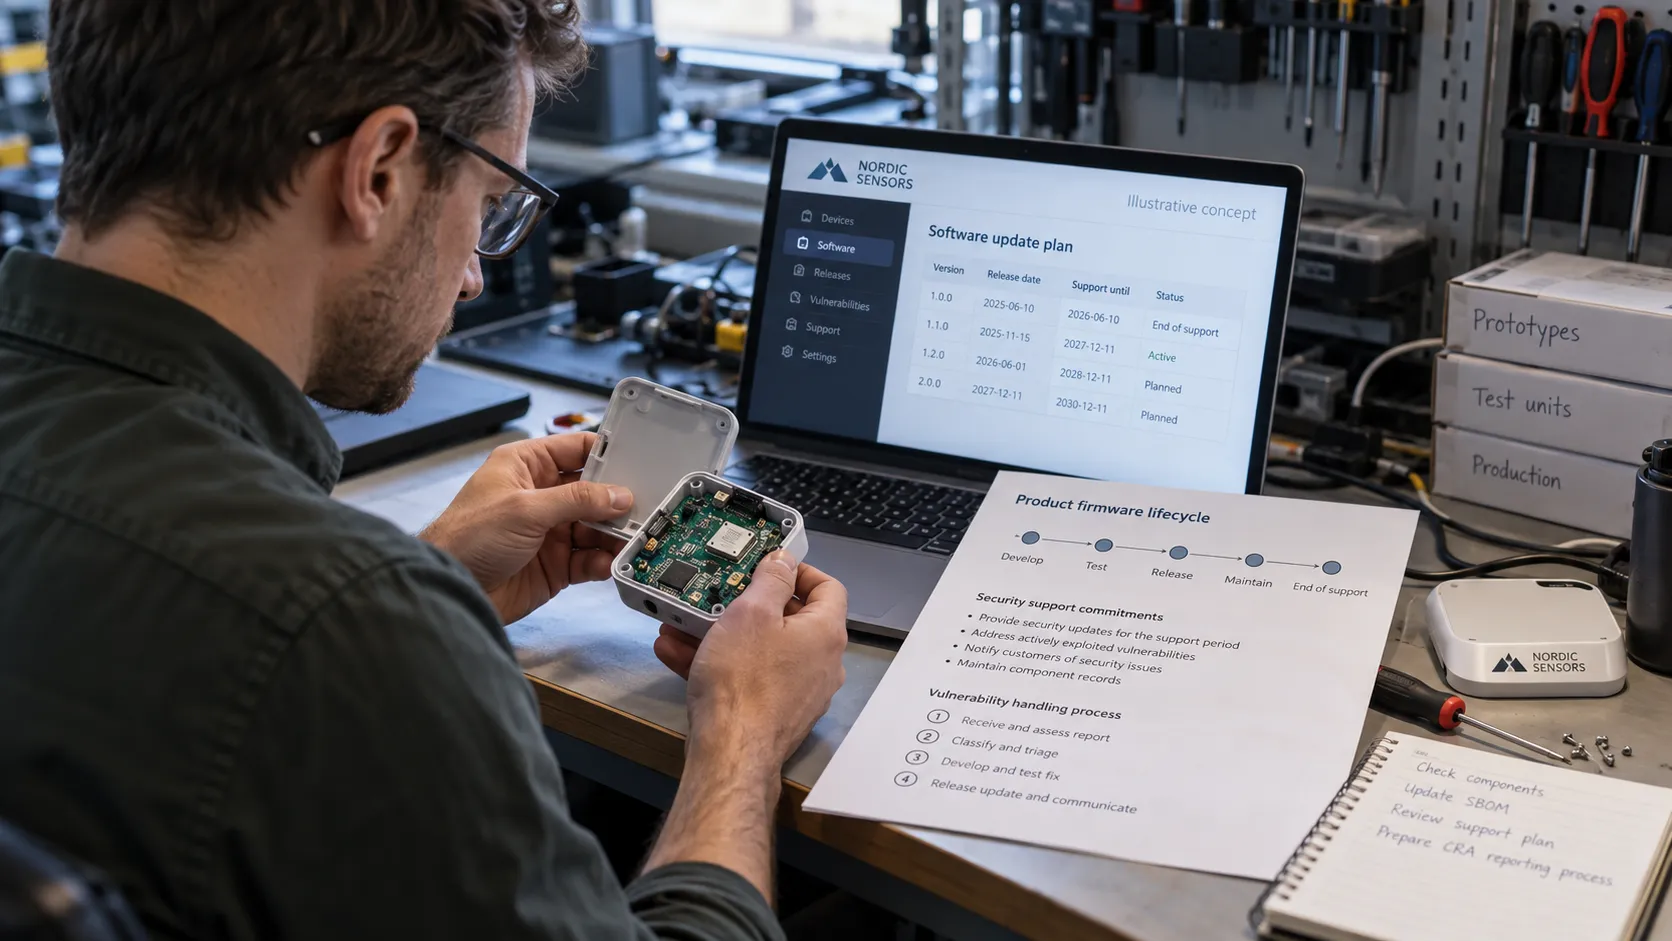
CRA manufacturer reporting began on 11 September 2026. The main product requirements follow in December 2027. Check product scope and your role now.
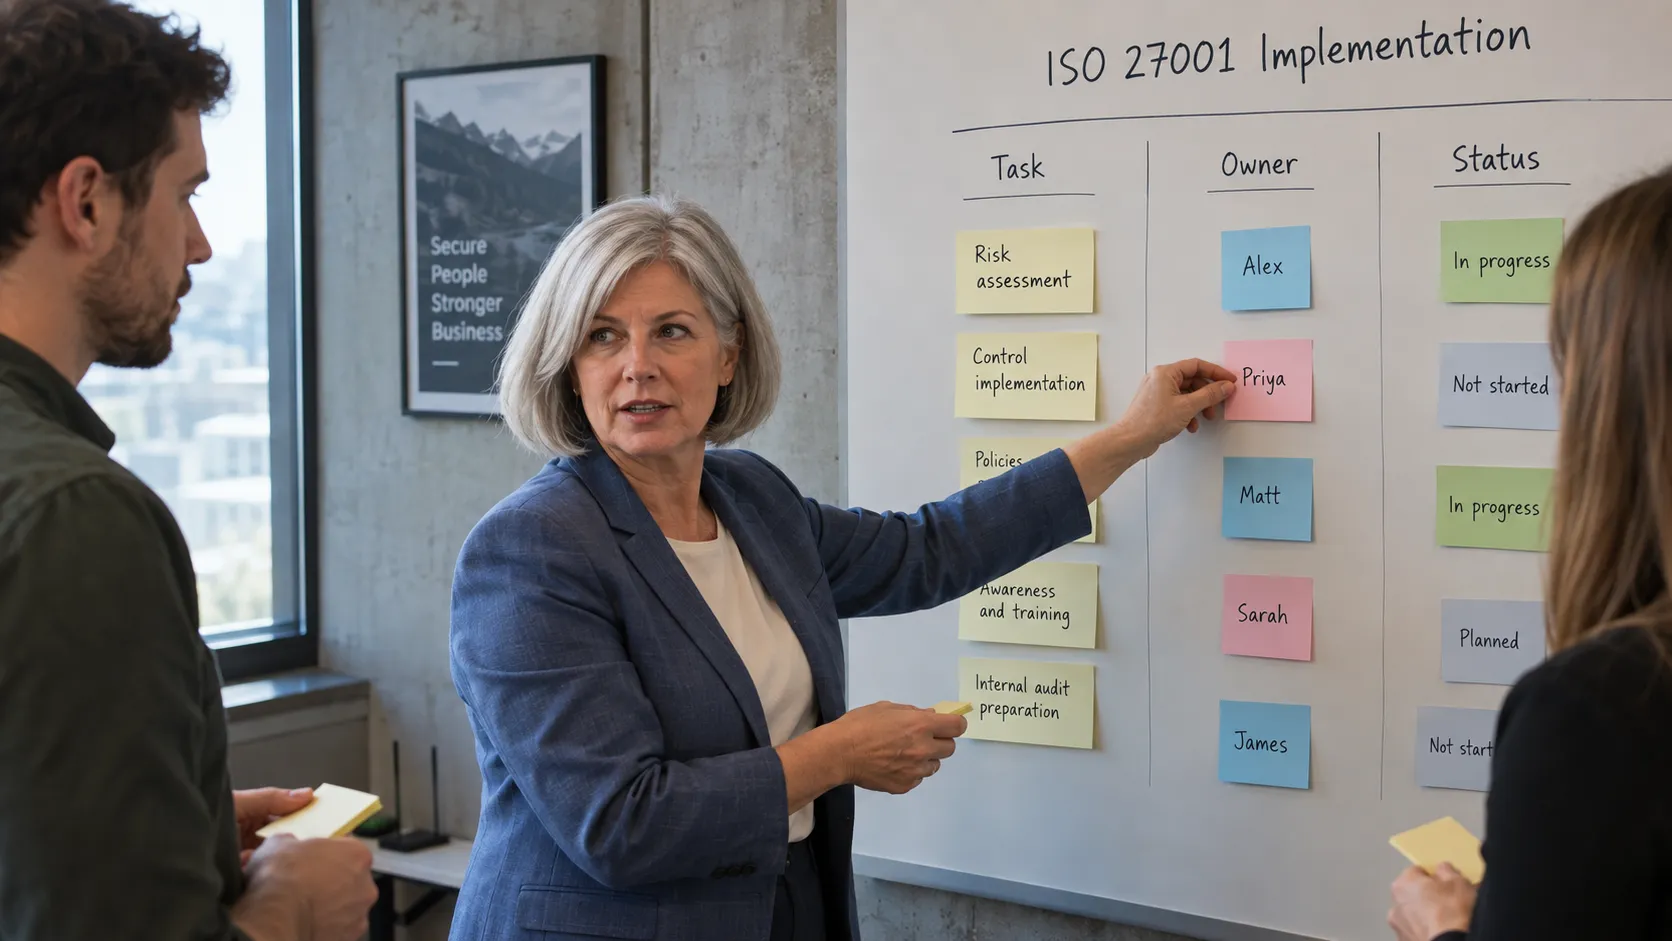
Implementation and audit are different assignments. Check the credential issuer, level and current status, then assess the consultant against the work you need.
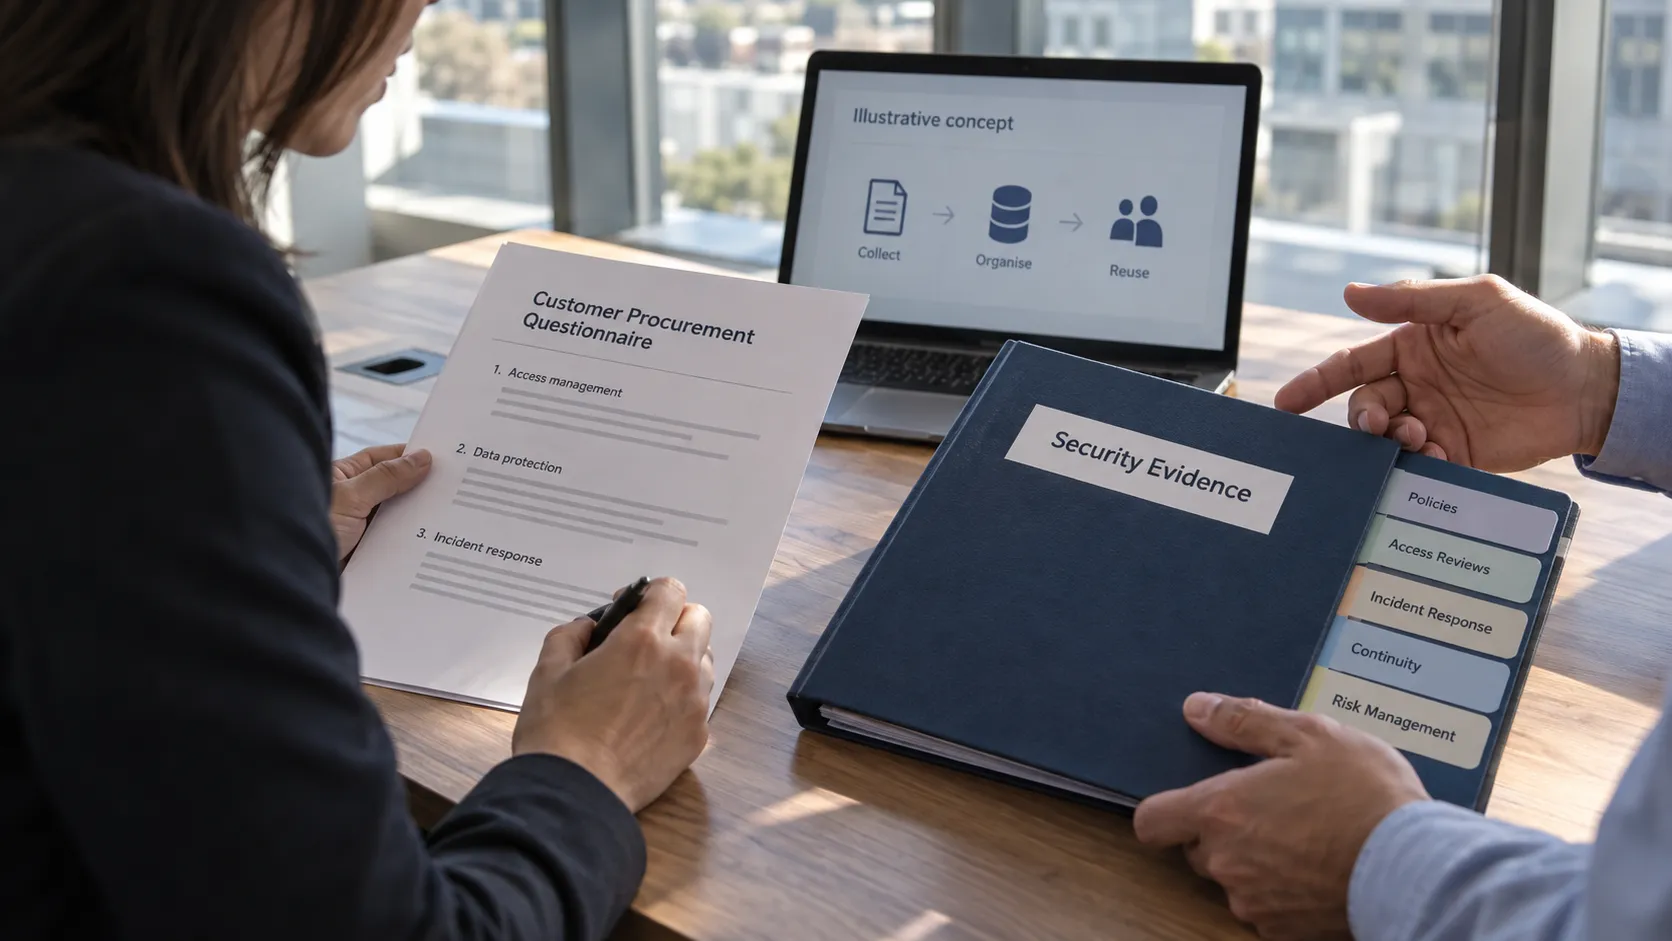
Clear security records help answer customer and investor questions. Build evidence around the controls you operate, with owners and an honest view of gaps.
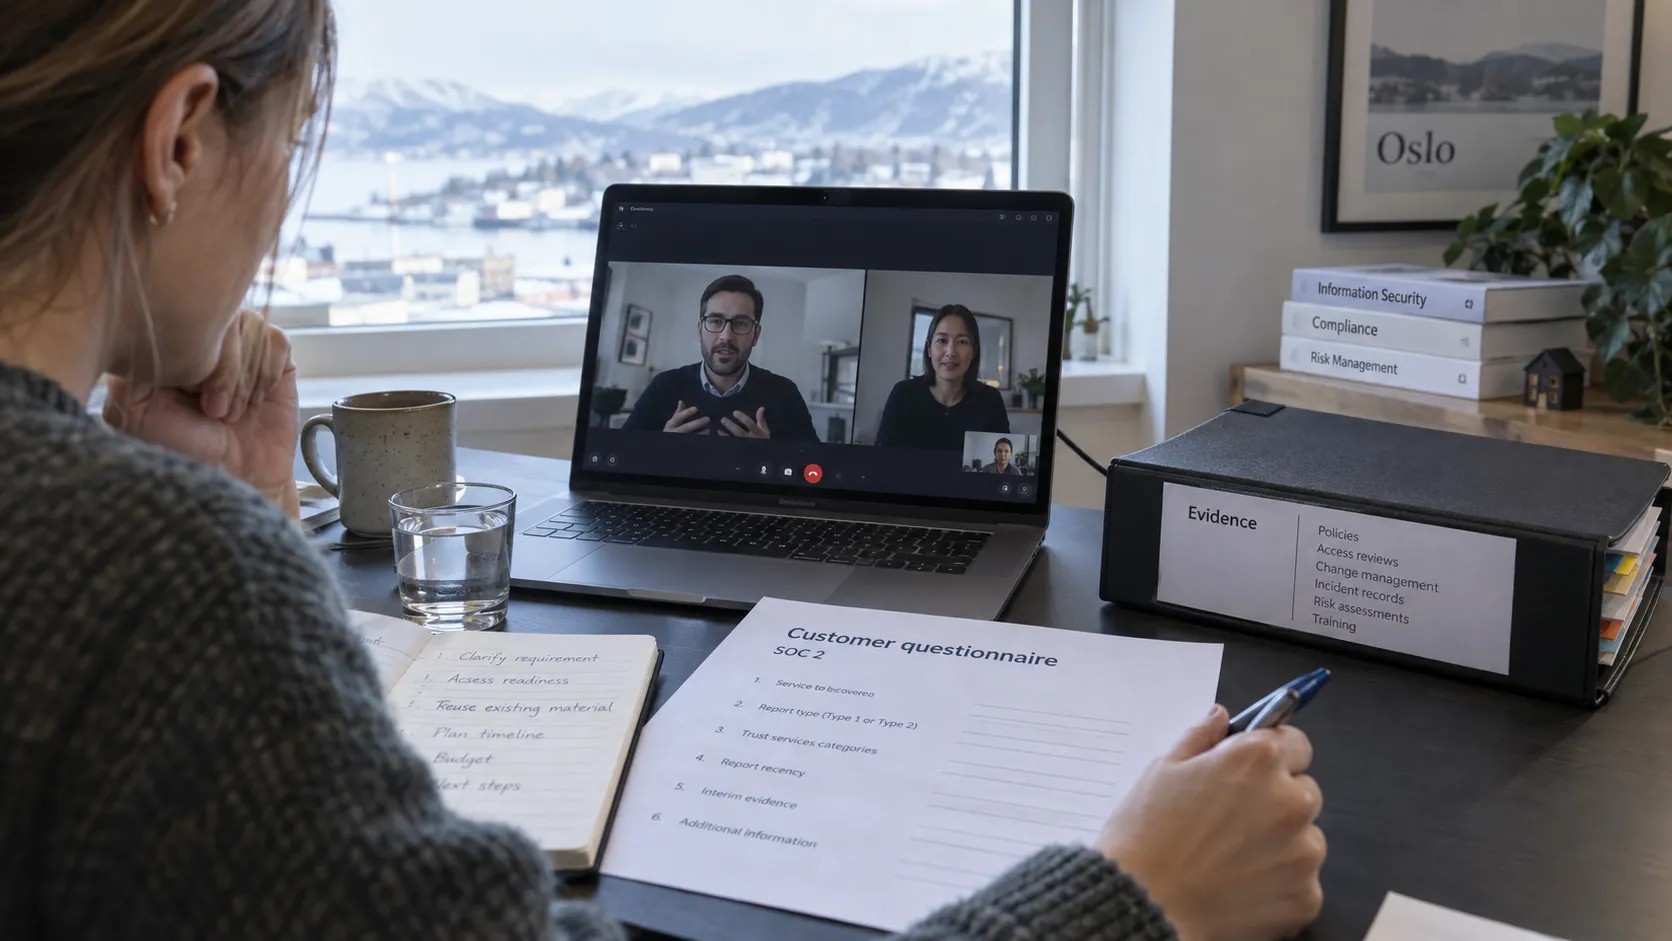
Let actual customer requirements define the SOC 2 scope, report type and timing. Reuse existing security evidence, but assess the gaps before budgeting.
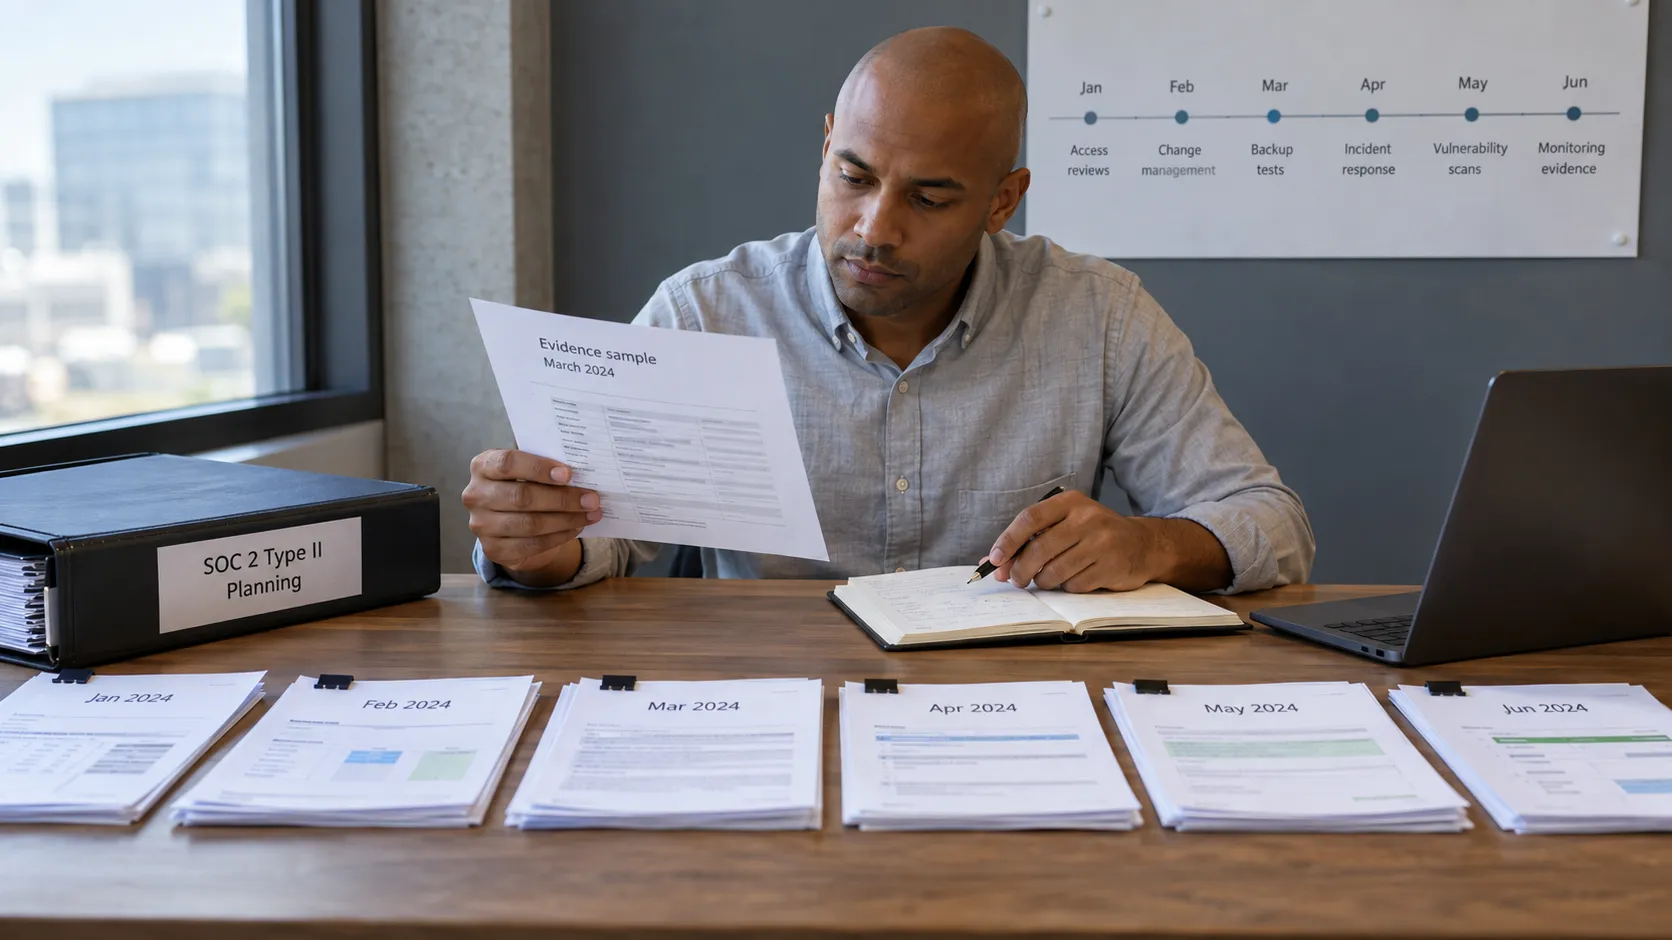
SOC 2 Type 2 reports on controls over a defined period. Read the system scope, opinion, testing results and customer responsibilities, not just the report title.
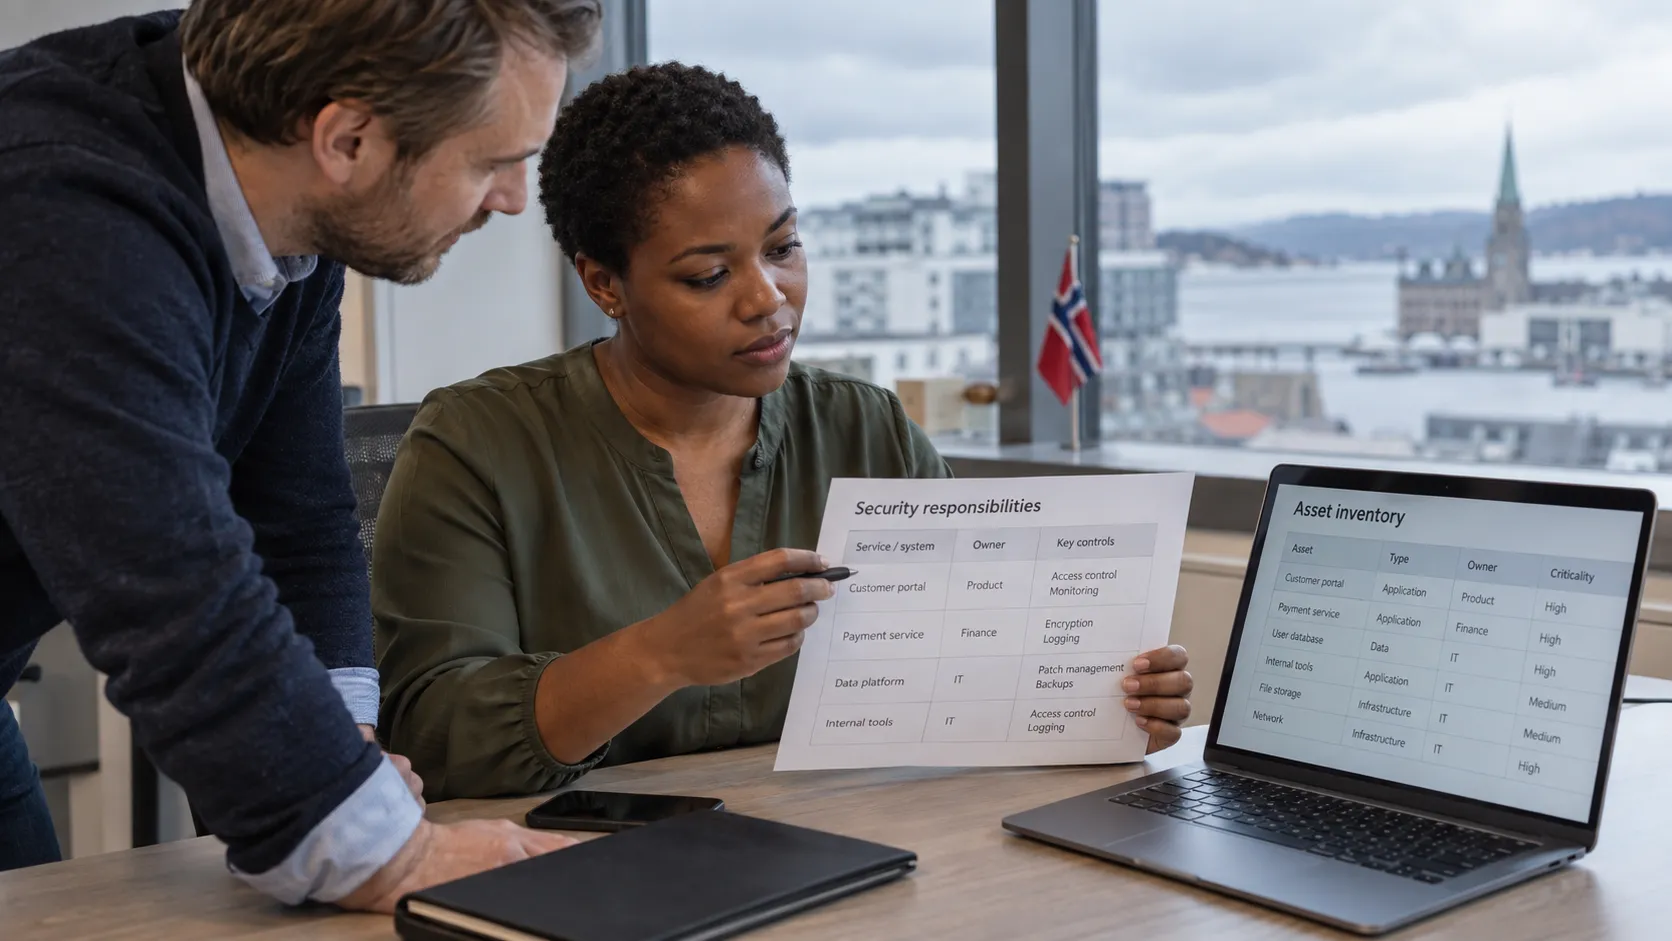
The Digital Security Act has applied since October 2025. Check the service definitions, exceptions and reporting rules for your category of provider.
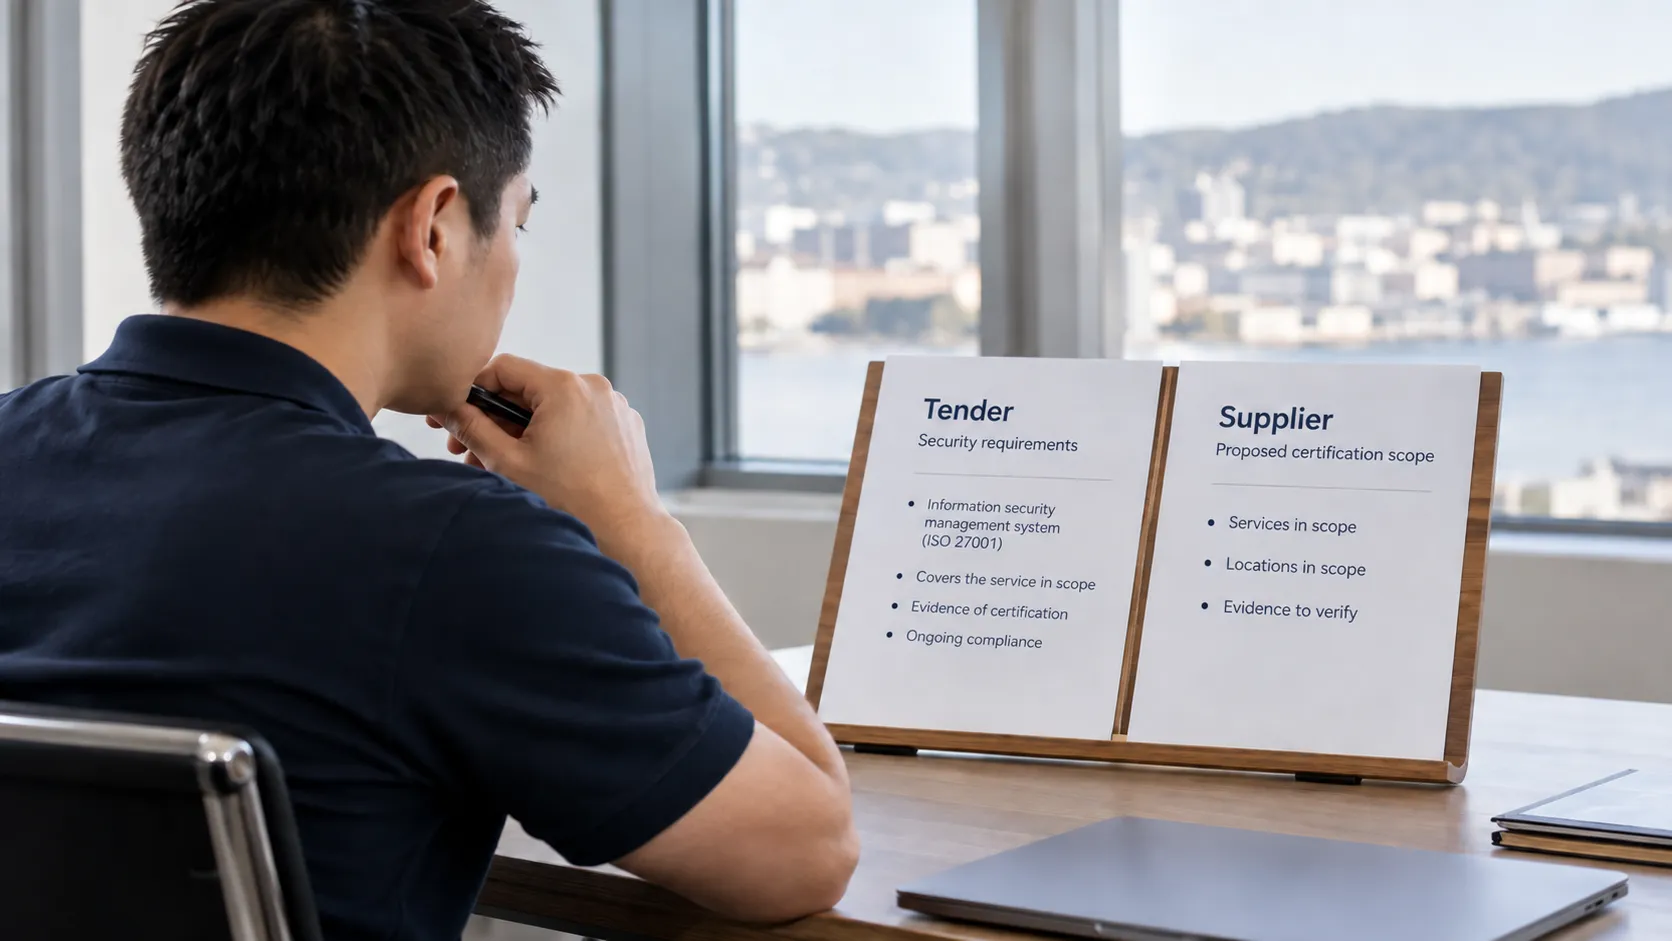
ISO 27001 certification gives buyers independent evidence about a defined information security management system. Its scope and the tender wording matter.
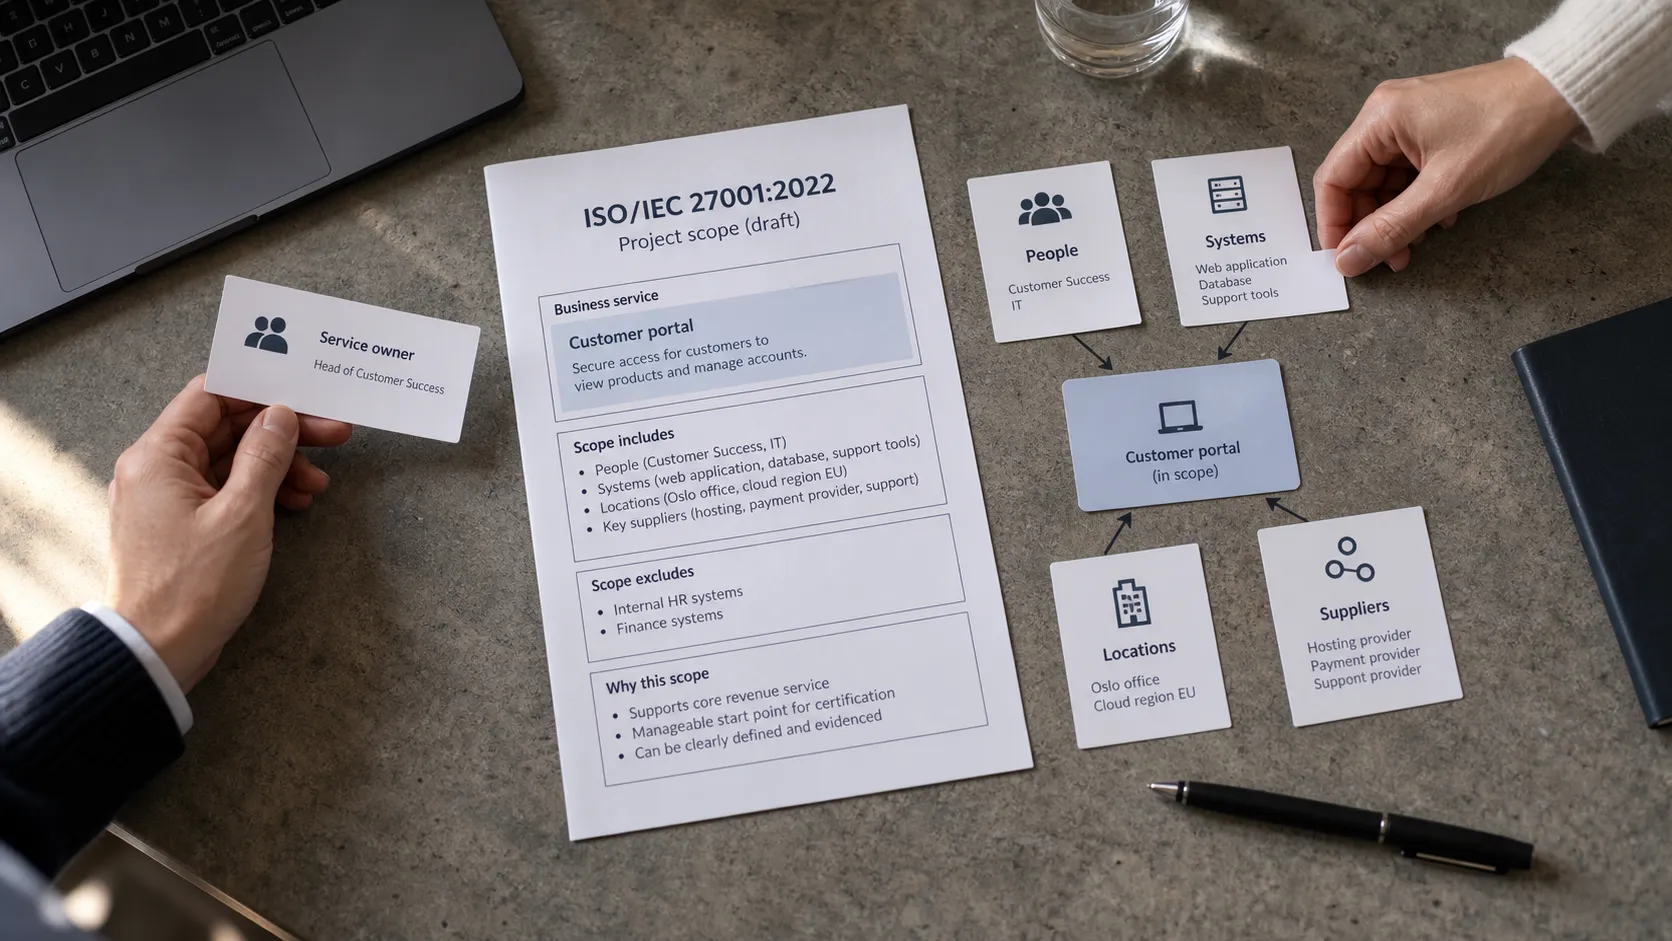
Define scope, assess risk, implement controls and gather evidence. A practical checklist for preparing a Norwegian SMB for ISO 27001 assessment.
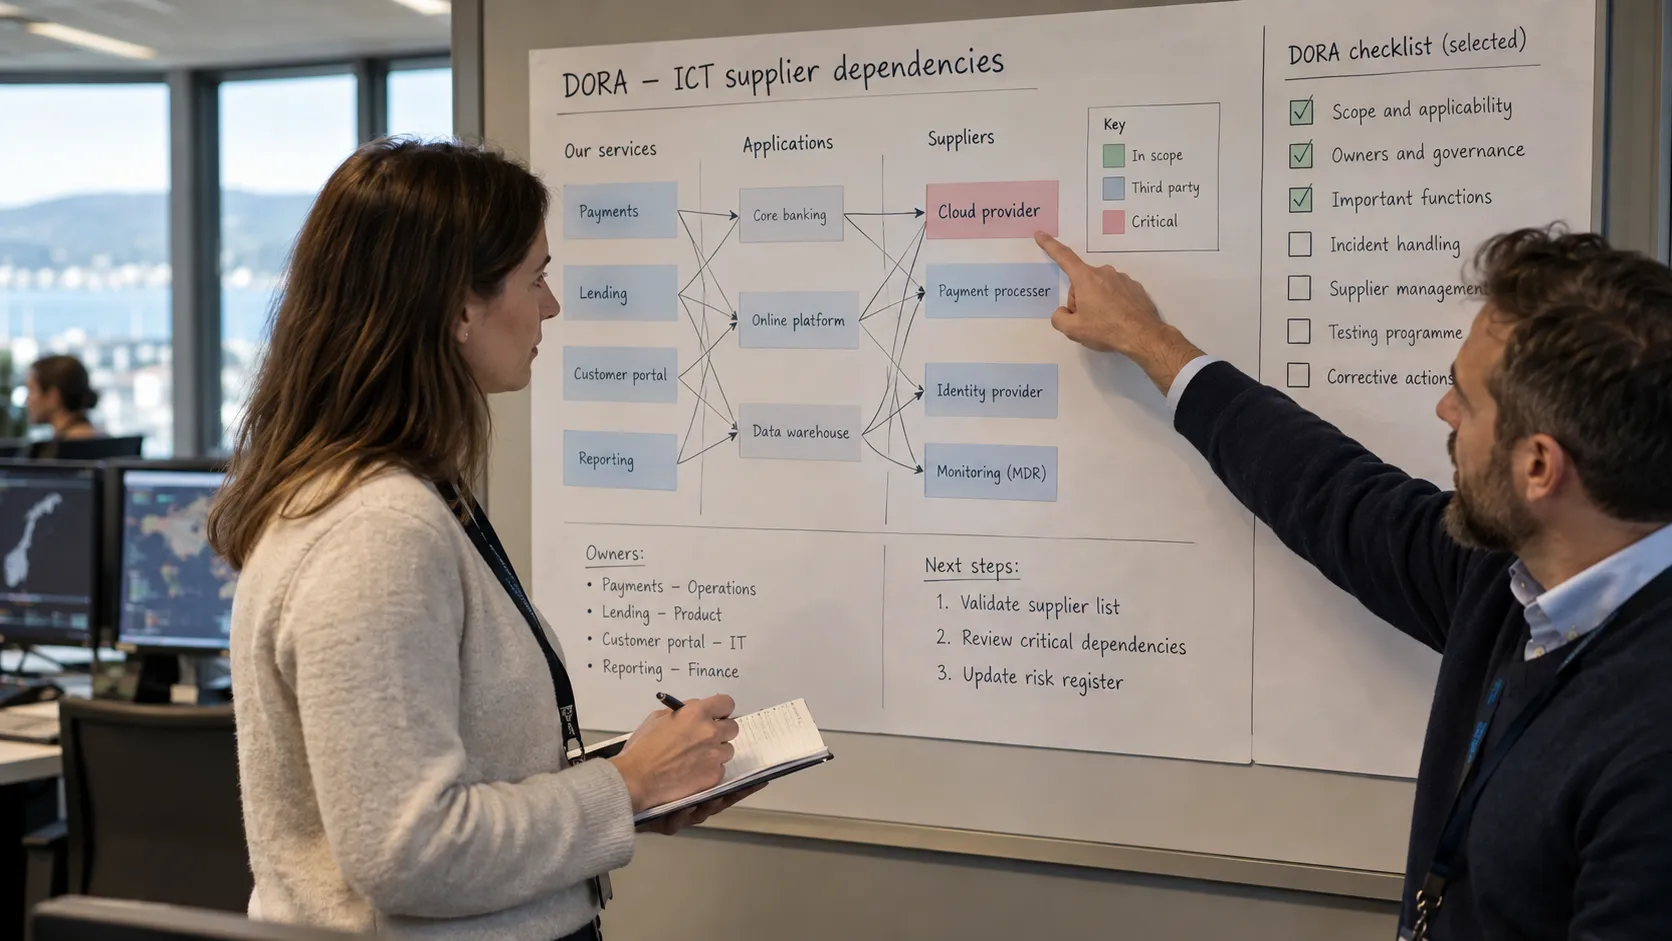
Confirm the applicable regime, map critical functions and connect the evidence. Updated for Norway's September 2026 extension of DORA-based rules.
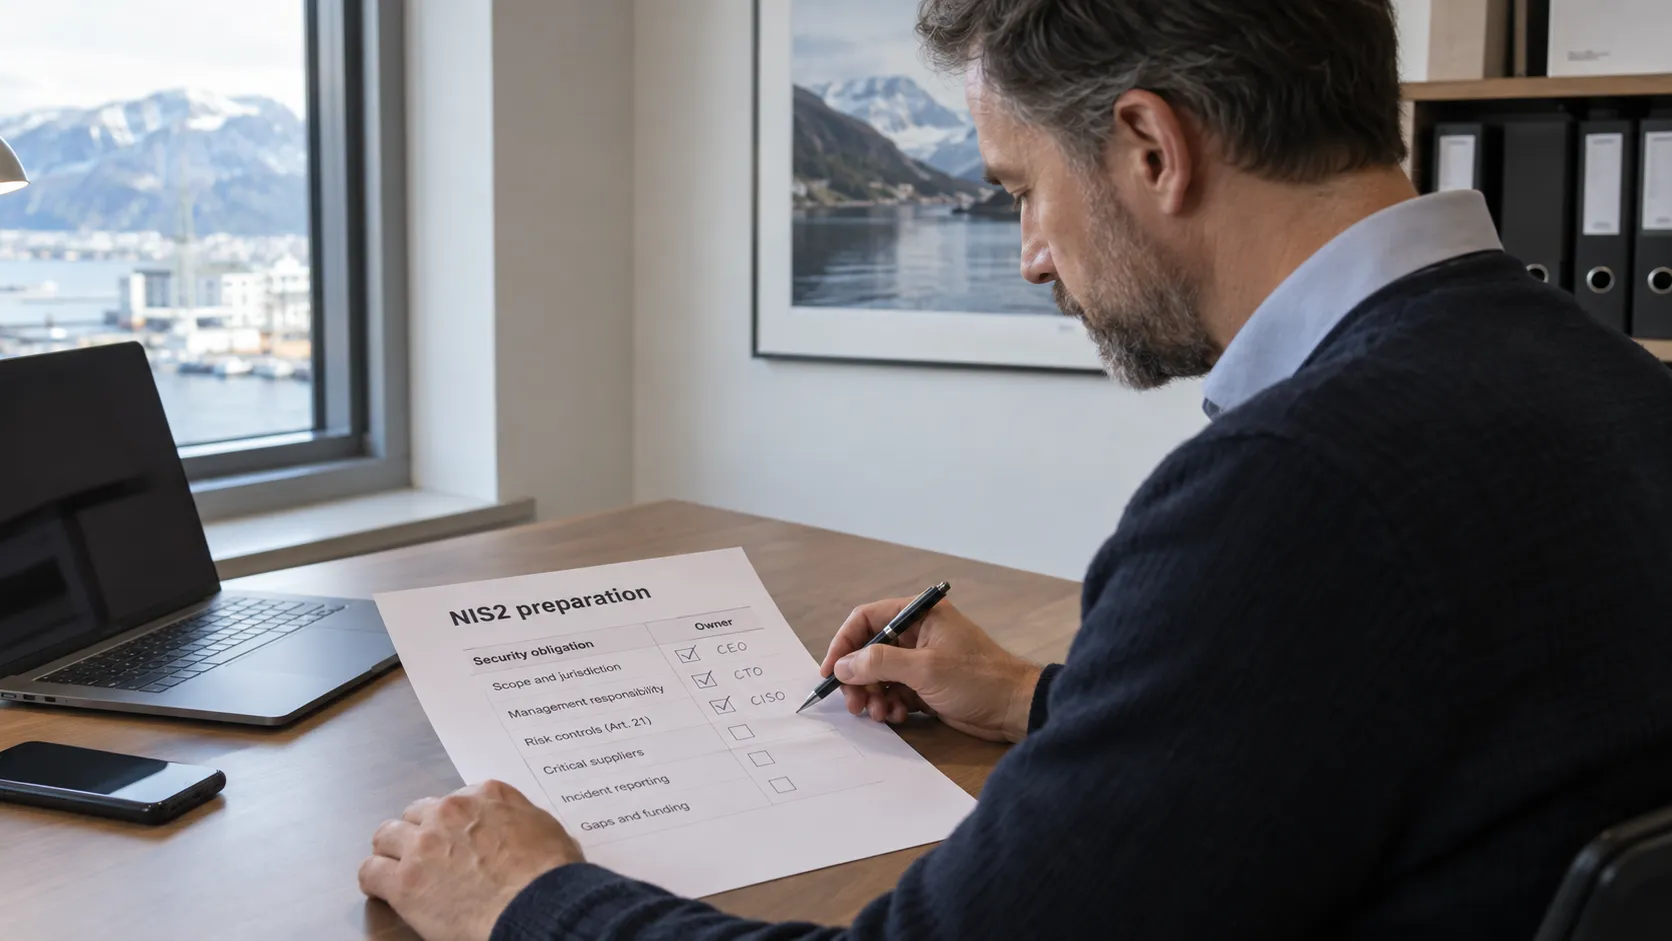
A NIS2 preparation checklist for management: scope, accountable owners, risk measures, supplier oversight and a reporting process matched to applicable law.
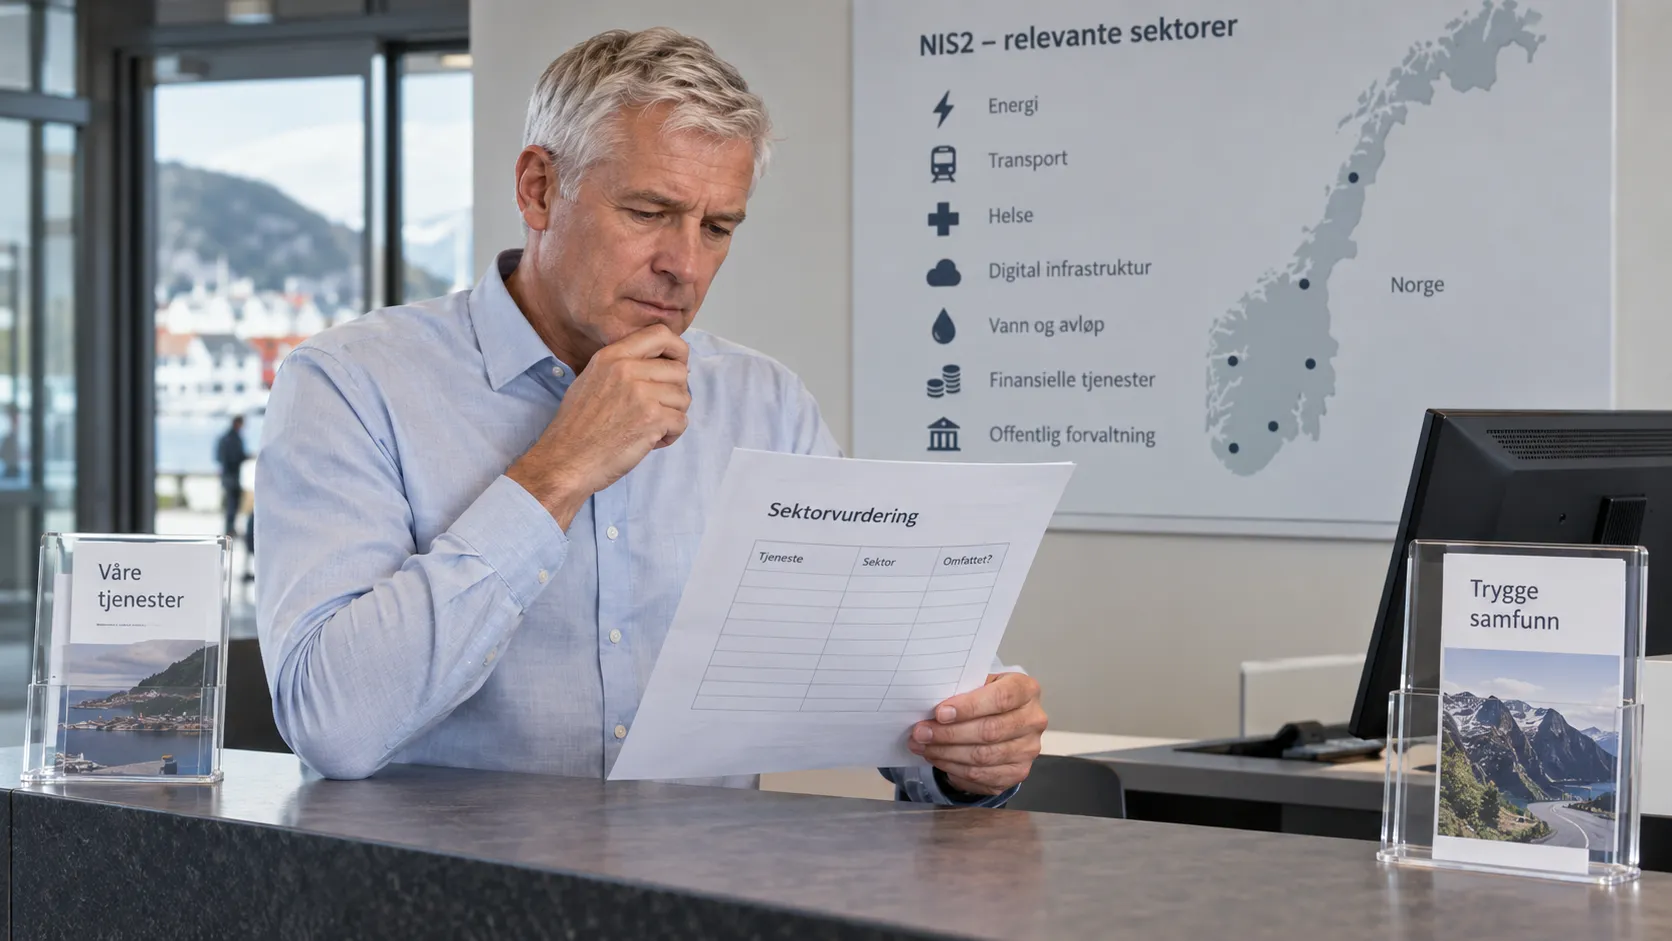
NIS2 scope depends on service, size, jurisdiction and exceptions. Distinguish direct legal duties from customer requirements and Norway's existing NIS1-based law.
Turn NIS2 preparation into a practical work plan: confirm applicable rules, assess controls, exercise reporting and track corrective actions.