What NIS2 means for Norwegian businesses
NIS2 scope depends on service, size, jurisdiction and exceptions. Distinguish direct legal duties from customer requirements and Norway's existing NIS1-based law.
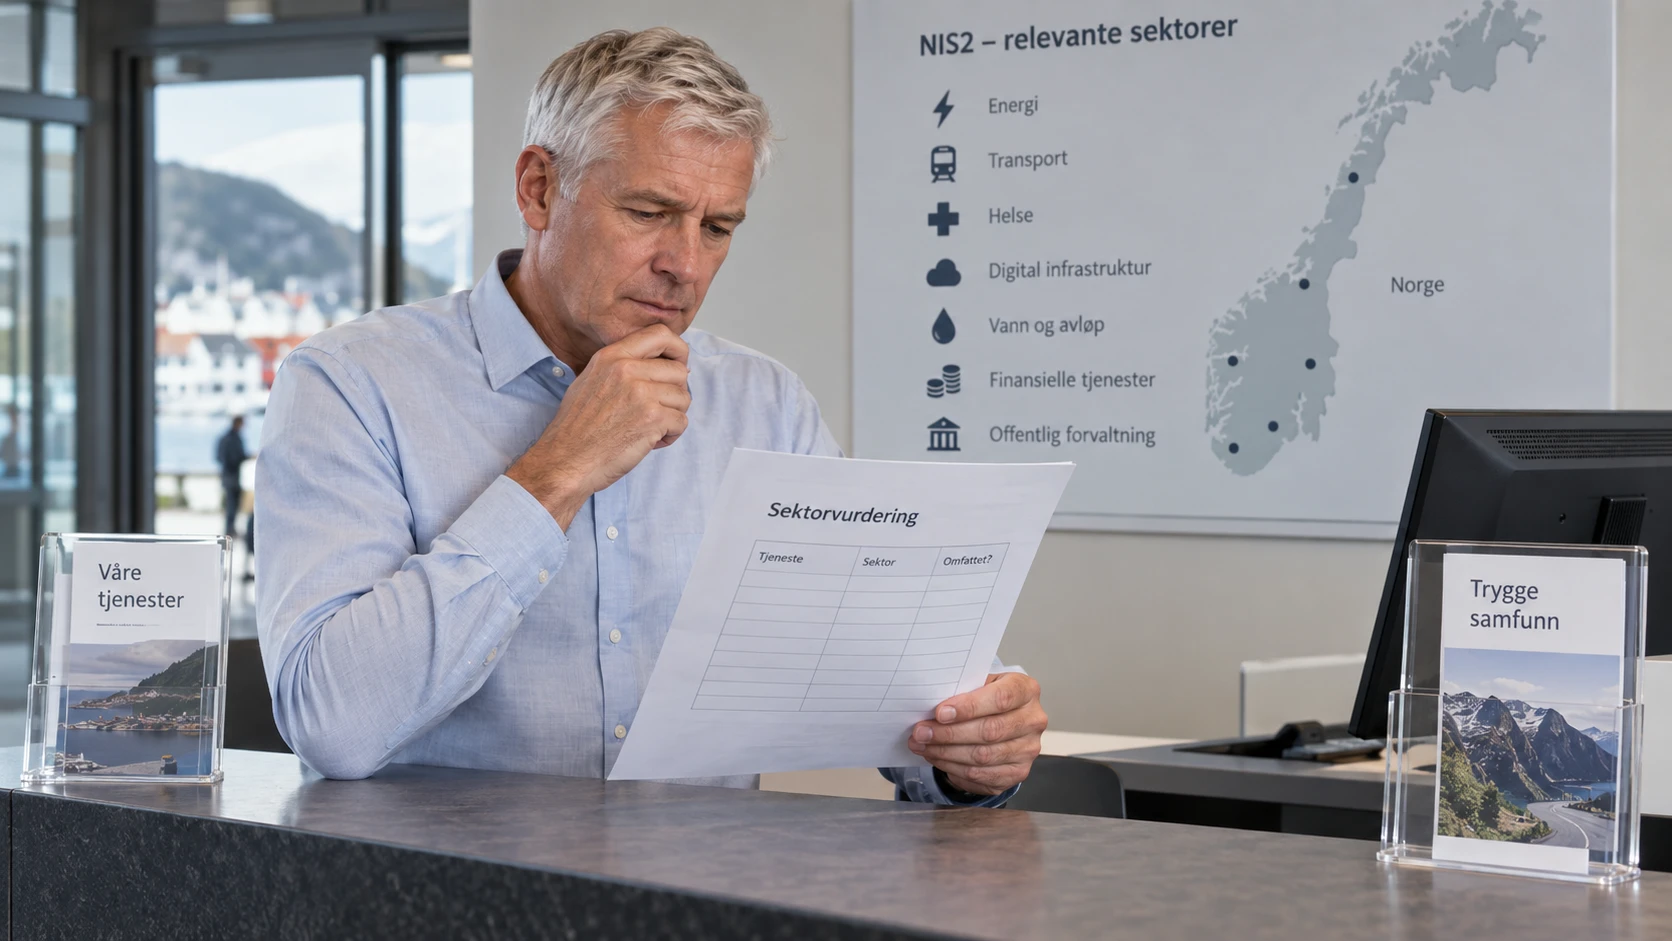
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
NIS2 is the EU directive on cybersecurity for specified sectors and services. It expands the earlier NIS framework and addresses risk management, incident reporting, management responsibility and supervision.
For a Norwegian business, the first question is which legal entity provides which service, and where. That assessment is more reliable than a simple headcount threshold.
Scope takes more than two numbers
The directive generally covers medium-sized and larger entities of the types listed in Annexes I and II, with exceptions that can include smaller organisations. Size assessment can involve financial measures and partner or linked enterprises. Article 2 sets the scope framework.
Do not treat “50 employees or €10 million turnover” as a complete legal test. Likewise, essential and important status is not determined simply by placing a sector in one column. Entity type, size and specific designation rules matter.
Check the relevant national implementation and any sector-specific regime. EU operations or certain digital services can require a jurisdiction assessment even when the parent company is Norwegian.
Norway’s current law is a separate starting point
Norway’s Digital Security Act entered into force on 1 October 2025 and implements NIS1. It is not the Norwegian version of NIS2.
The government’s 2026 budget documents describe work to prepare Norwegian implementation of NIS2 and CER. Use current Norwegian law and official implementation notices when setting legal deadlines.
Supplier requirements can arrive through contracts
A covered customer must consider supply-chain security. It may ask suppliers about access, incident handling, continuity and assurance evidence.
Those requirements can become contractual obligations. They do not automatically transfer all of the customer’s statutory NIS2 duties to the supplier or make it an essential entity.
Read the contract, identify the evidence requested and record what the business can actually demonstrate.
Make the conclusion reviewable
Write a scope memo covering entities, services, jurisdictions, size assessment, exceptions and the sources used. Give it an owner and a review trigger.
Then map the applicable requirements to existing controls and gaps. The NIS2 leadership checklist turns that conclusion into responsibilities and a work plan.