NIS2 checklist for Norwegian SMB leaders
A NIS2 preparation checklist for management: scope, accountable owners, risk measures, supplier oversight and a reporting process matched to applicable law.
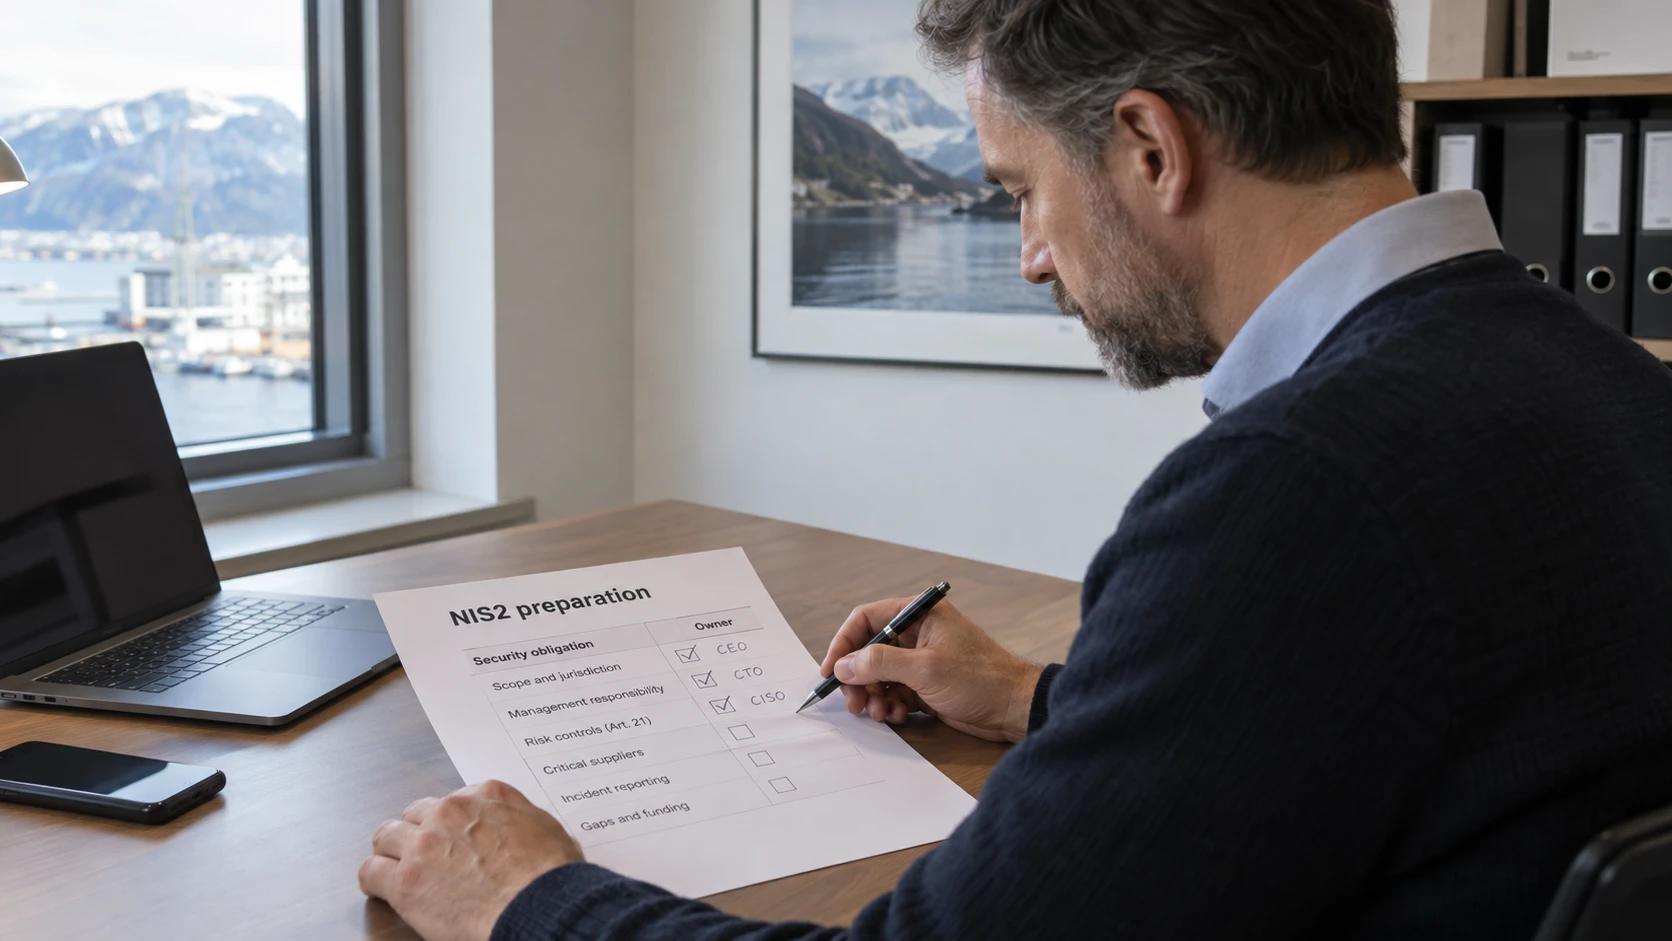
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
NIS2 preparation starts with a documented scope assessment. A sector label or employee count alone is not enough to decide whether a business is covered.
For a Norwegian company, distinguish current Norwegian law, any applicable EU-country obligations and customer contract requirements. Norway’s Digital Security Act implements NIS1; it should not be presented as the Norwegian NIS2 implementation.
1. Establish scope and jurisdiction
Identify the legal entities, services and countries involved. Assess the directive’s sector definitions, size rules, group relationships and exceptions against the relevant national law.
Record the basis for inclusion or exclusion, who assessed it and when it must be reviewed. A new service or acquisition can change the answer.
2. Assign management responsibility
Name an accountable executive and the owners of the operational work. Management needs to understand the material risks, approve the approach and ensure sufficient resources.
Plan appropriate training and regular reporting. A status report should identify decisions, overdue work and unresolved risks, rather than just the number of completed tasks.
3. Map controls to the requirements
Use Article 21’s risk-management measures and the applicable national or sector rules as the reference. Annexes I and II identify entity types; they are not the control library.
Review incident handling, continuity, supply-chain security, secure development, access controls and the effectiveness of measures. ENISA’s technical guidance supports implementation of the EU rules for specified digital-service sectors; check its scope before applying it as a legal checklist.
4. Check critical suppliers
Identify the suppliers whose failure or compromise would affect delivery. Clarify access, incident notification, assurance evidence and exit arrangements. Prioritise by dependency and impact.
5. Prepare reporting that can work out of hours
NIS2 uses staged reporting for significant incidents, including an early warning within 24 hours and a notification generally within 72 hours of awareness. Confirm the precise trigger, exceptions, recipient and later reporting duties in the applicable regime. The Commission’s FAQ explains the structure.
Assign a primary reporter and backup. Rehearse an incident with incomplete information and simultaneous contractual or privacy reporting duties.
6. Fund and review the gaps
Give each gap an owner, priority and deadline. Check progress through operating evidence and exercises. Keep the scope assessment current as Norwegian implementation and relevant EU rules develop.
The NIS2 explainer provides more detail on the scope questions.