How Nordic SMBs prepare for NIS2
Turn NIS2 preparation into a practical work plan: confirm applicable rules, assess controls, exercise reporting and track corrective actions.
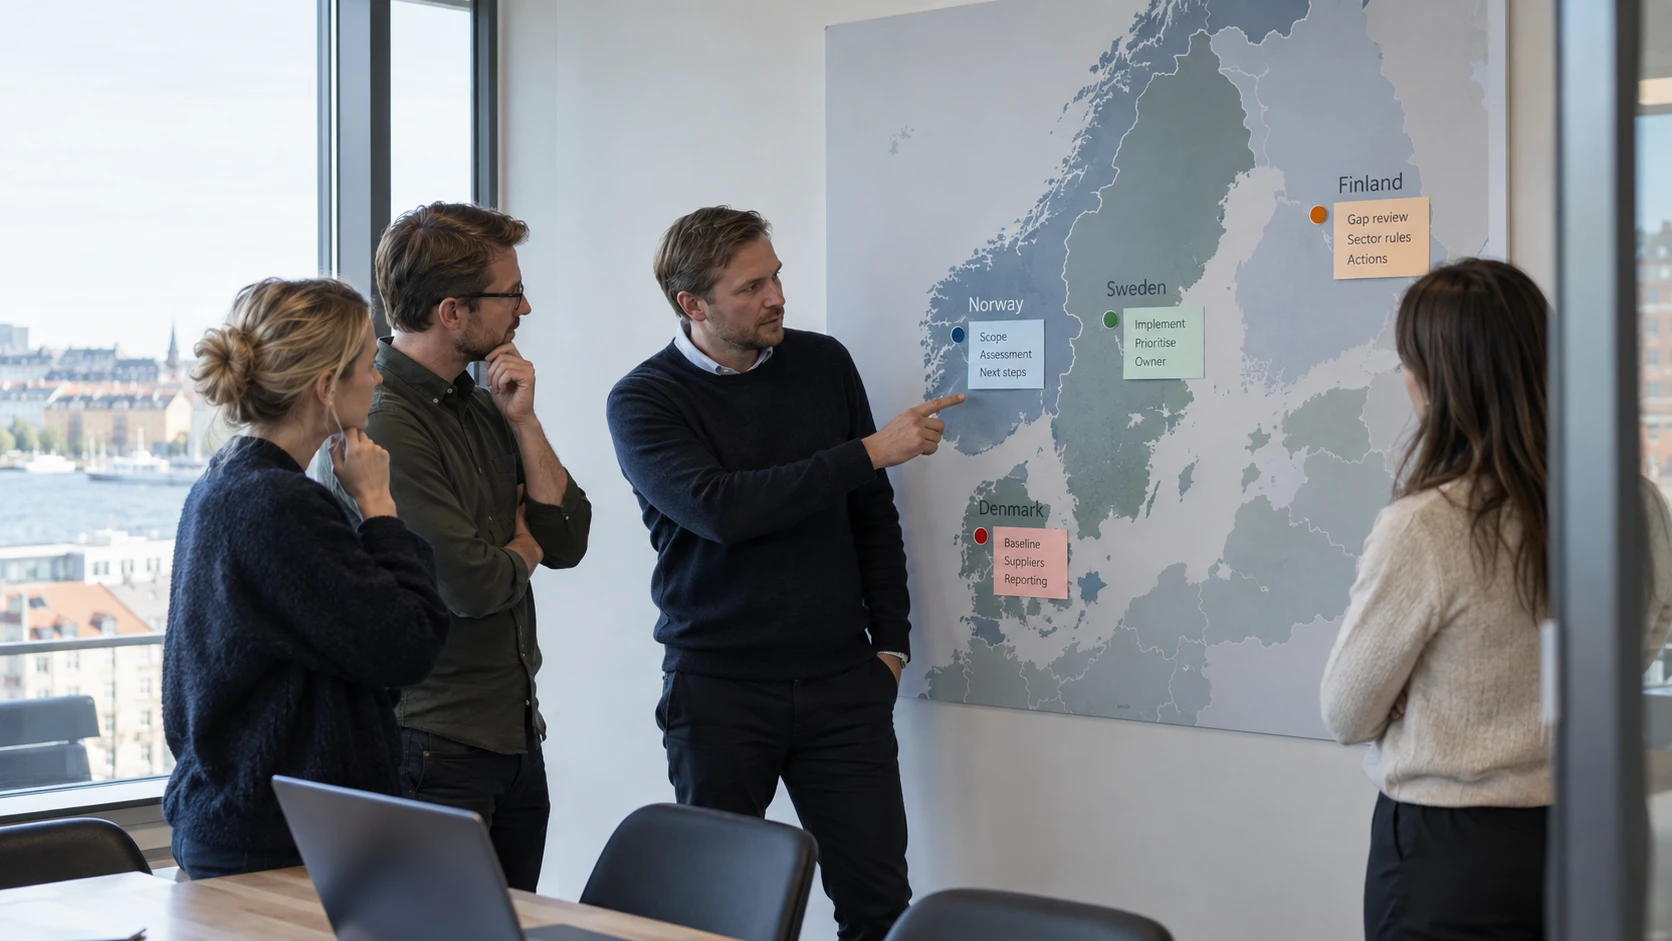
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
For a Nordic business, NIS2 preparation needs a country-by-country view where operations cross borders. The directive sets the framework; the applicable national law and sector rules determine the operational obligations.
Start with a scope assessment, then give the resulting work a manageable sequence.
Establish the baseline
Inventory the services, systems and suppliers needed to keep the business running. Identify the controls already in operation and the evidence that shows they work.
Map the gaps to Article 21 and any more detailed applicable requirements. NIS2’s Annexes I and II list sectors and entity types. They do not provide a security-control checklist.
An existing ISO 27001 system may supply useful processes and records. Assess the overlap explicitly; a percentage estimate without examining the scope tells you little.
Work on the gaps that change the risk
Prioritise controls whose absence creates a material exposure or prevents incident handling. Depending on the environment, that could mean privileged-access protection, reliable backups, supplier escalation or visibility into critical systems.
Give each action an owner and an acceptance criterion. “Improve backup” is difficult to close. “Demonstrate restoration of this service within the agreed recovery objective” can be checked.
ENISA’s implementation guidance offers useful examples for the digital sectors covered by Implementing Regulation 2024/2690. Apply its legal requirements only where relevant.
Exercise the reporting process
Choose a scenario with incomplete information: a supplier reports a compromise, or an administrator account is used unexpectedly. Determine who assesses significance, who can notify authorities and how deputies obtain access out of hours.
Record the decisions and the information available at each point. Use the deadlines and channels that apply to the entity, including any separate privacy or contractual requirements.
Review the evidence with management
At the end of each work period, review completed actions, open risk and the next decisions. Store evidence where the responsible people can retrieve it.
The purpose is an operating process that can survive a real incident and explain its decisions afterwards. The leadership checklist identifies the responsibilities management should retain.