ISO 27001 or NIS2 first?
Build shared security processes, but track legal duties and certification separately. Applicable legal deadlines take priority over commercial preferences.
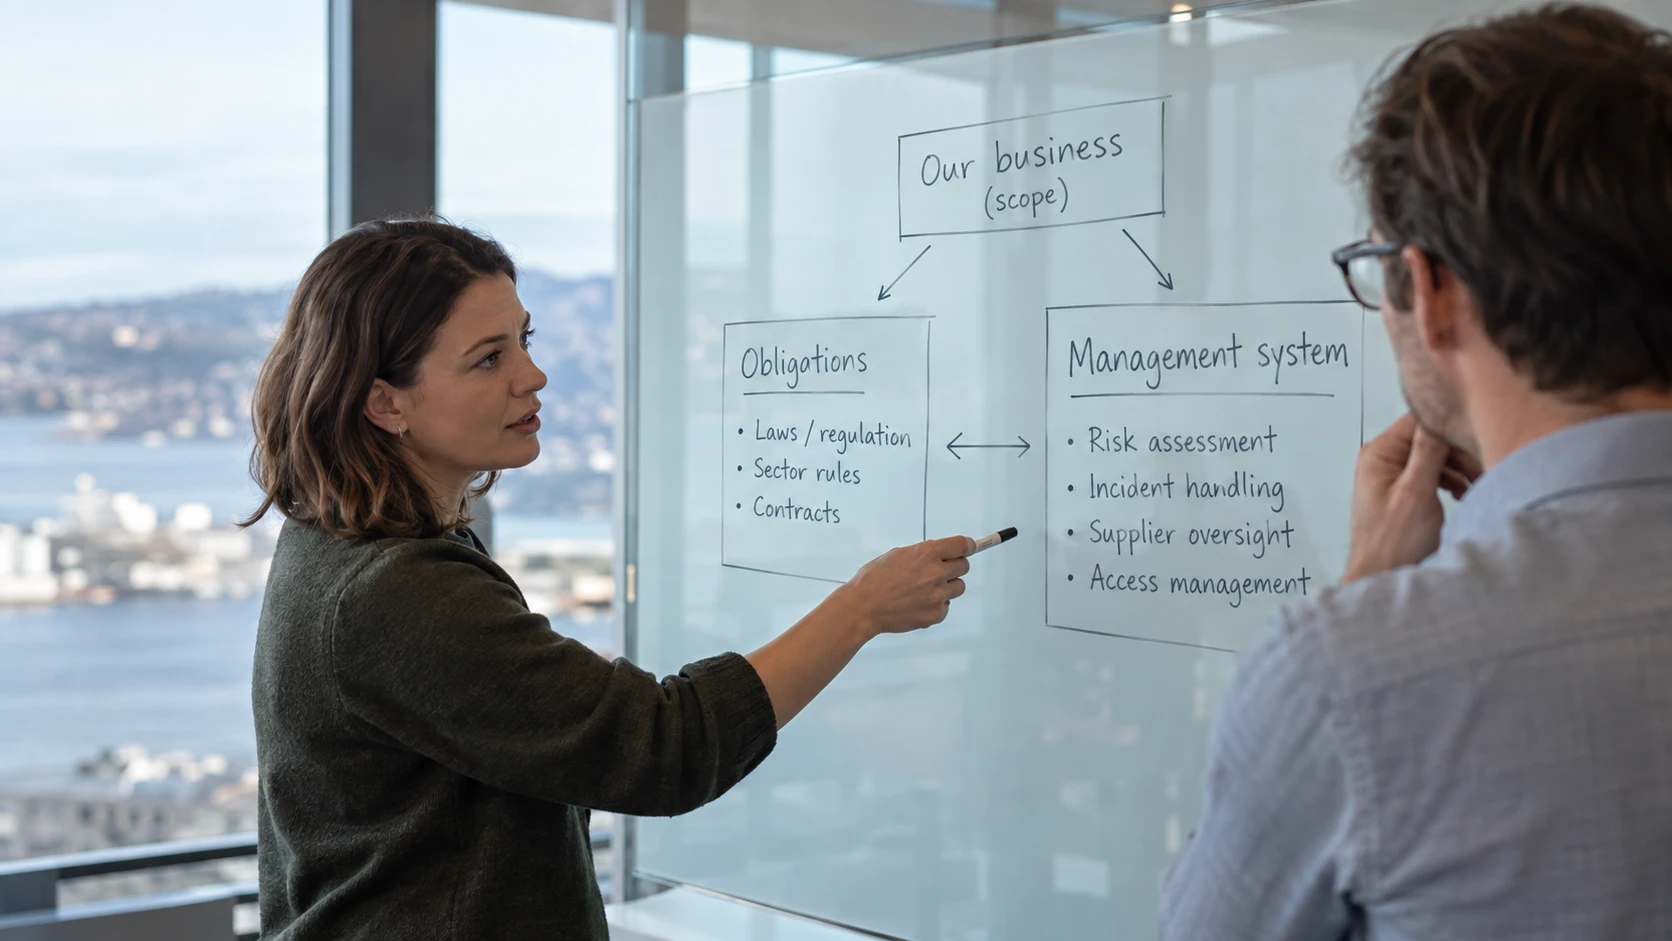
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
Start with the obligations that apply to the business today. A legal duty cannot be deferred because a customer would prefer an ISO 27001 certificate first.
After that, look for shared work. Risk assessment, incident handling, supplier oversight and access management can support both an ISO 27001 management system and NIS2 preparation. There is little value in maintaining separate versions of the same records.
Separate the outcomes
ISO 27001 certification is an independent assessment of a defined management system. NIS2 creates legal obligations through the applicable national implementation. An ISO certificate does not establish NIS2 compliance.
NIS2’s requirements include risk management, reporting and management responsibilities. Scope, registration, supervision and sector-specific rules also need attention. The difference cannot be reduced to adding a reporting template and a board meeting.
Identify the applicable jurisdictions
Norway’s current Digital Security Act implements NIS1. Norwegian NIS2 implementation is a separate process. Assess current Norwegian duties while tracking the forthcoming framework.
A Norwegian business may also need to assess an EU establishment or covered cross-border digital service under the relevant country’s rules. Customer contracts can introduce security requirements without making the supplier directly subject to every NIS2 duty.
Put the work in one plan
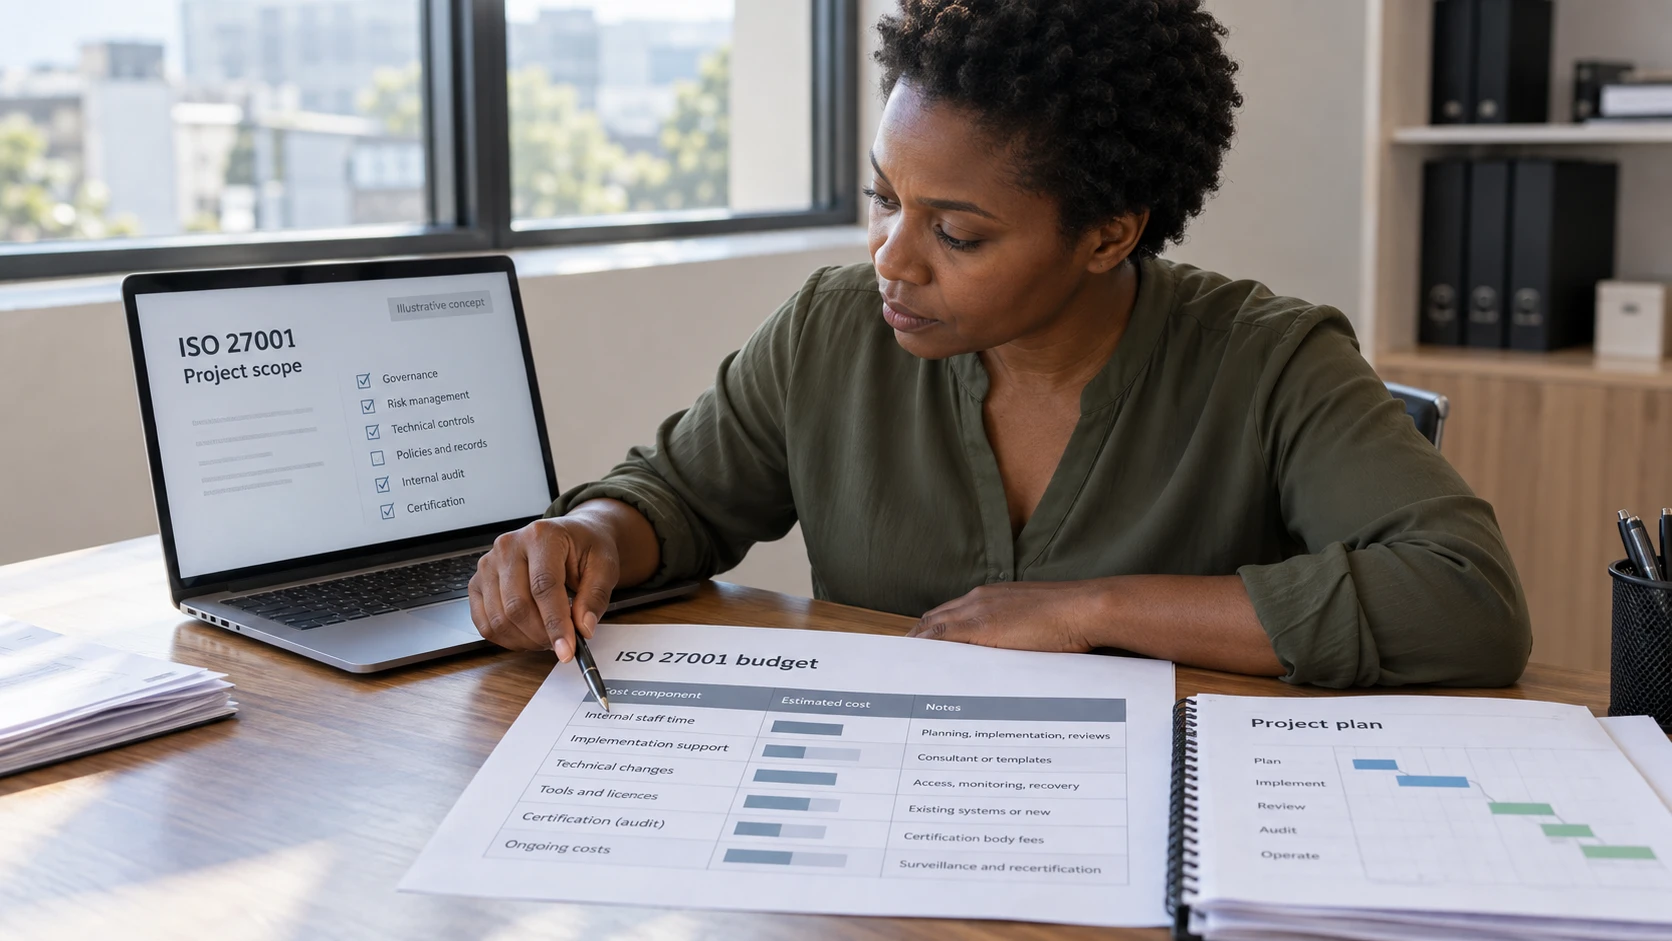
List each binding obligation, its deadline and its owner. Then map the existing controls and records to those requirements and the chosen ISO scope.
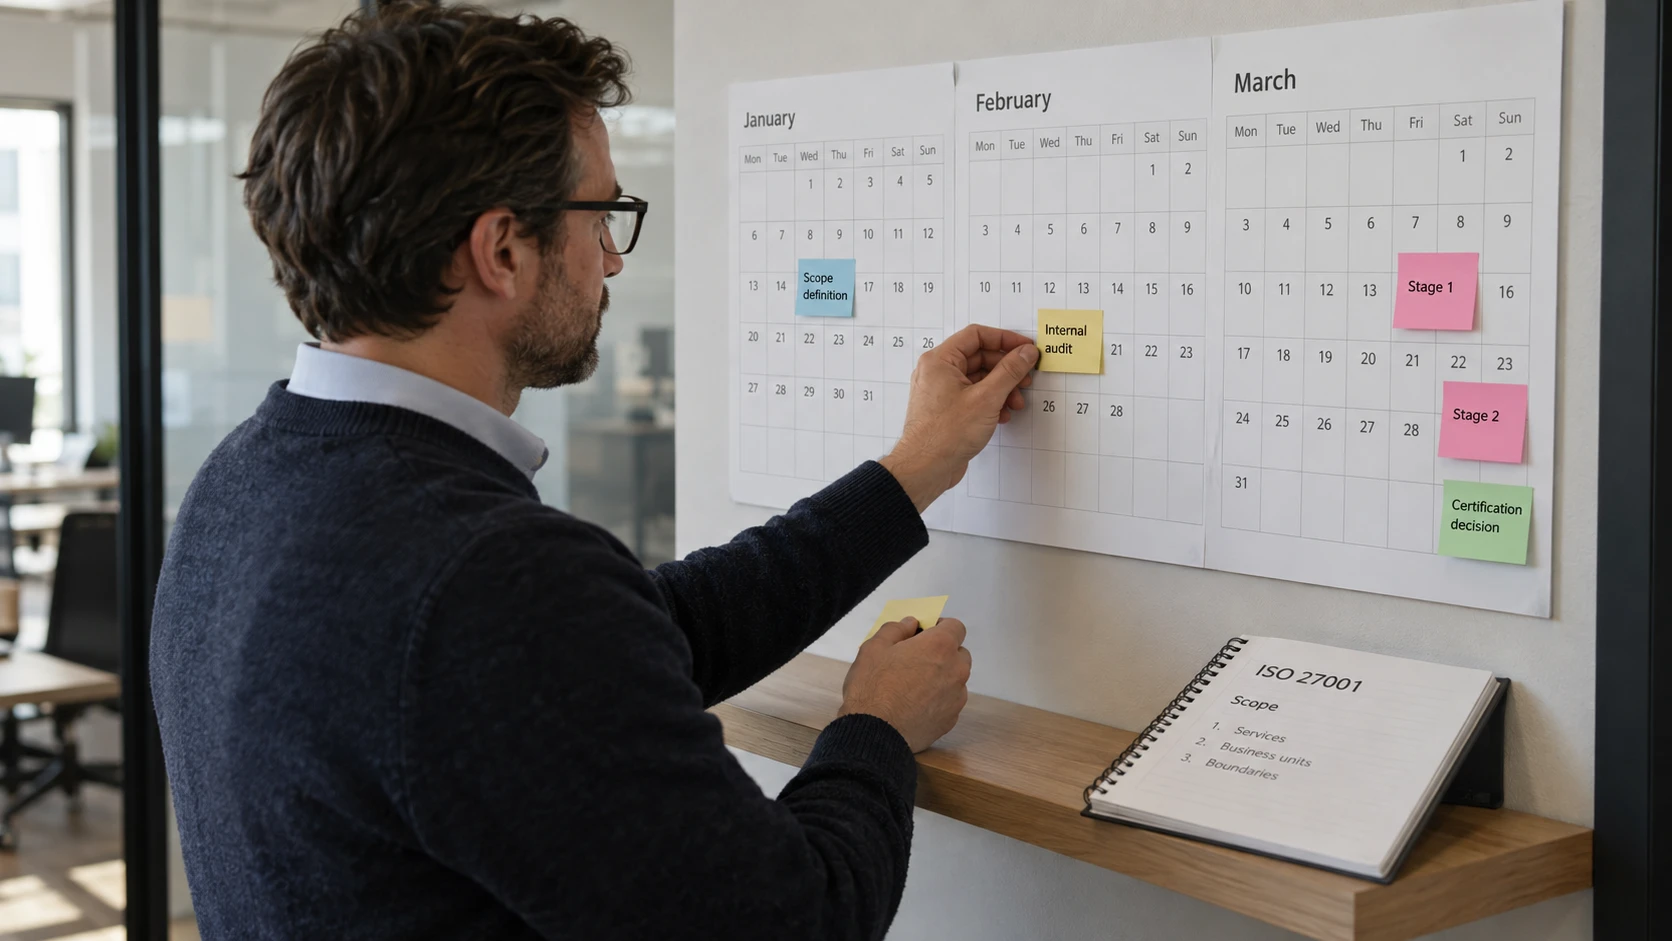
Fix urgent security gaps and current legal shortfalls first. Schedule certification preparation around confirmed customer requirements and the certification body’s calendar. Avoid promising that one assessment will automatically satisfy another.
For example, an incident process can serve several regimes while containing separate triggers, recipients and deadlines for each. An access review can provide one authoritative record referenced by several assessments.
The ISO 27001 checklist and NIS2 preparation guide cover the respective work. The goal is shared operation with a clear account of what each obligation still requires.