What ISO 27001 is, and why buyers ask for it
ISO 27001 certification gives buyers independent evidence about a defined information security management system. Its scope and the tender wording matter.
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
ISO 27001 is a standard for managing information security. It asks an organisation to understand its risks, choose appropriate controls and keep checking whether its approach works.
A certificate gives a buyer independent evidence about that management system within a defined scope. It does not certify every product as vulnerability-free or replace the buyer’s own supplier assessment.
What the management system contains
An information security management system, or ISMS, connects responsibilities, risk decisions, policies and records. It should make clear who approves access, how incidents are handled, how suppliers are assessed and how shortcomings are corrected.
ISO/IEC 27001 provides the requirements. The organisation determines necessary controls and explains its selection in the Statement of Applicability. Annex A is a reference for that work, not a reason to implement every control without considering the business.
Why procurement asks for a certificate
A buyer sharing sensitive information needs a basis for assessing the supplier. Certification can provide a recognised starting point and reduce some repeated explanation.
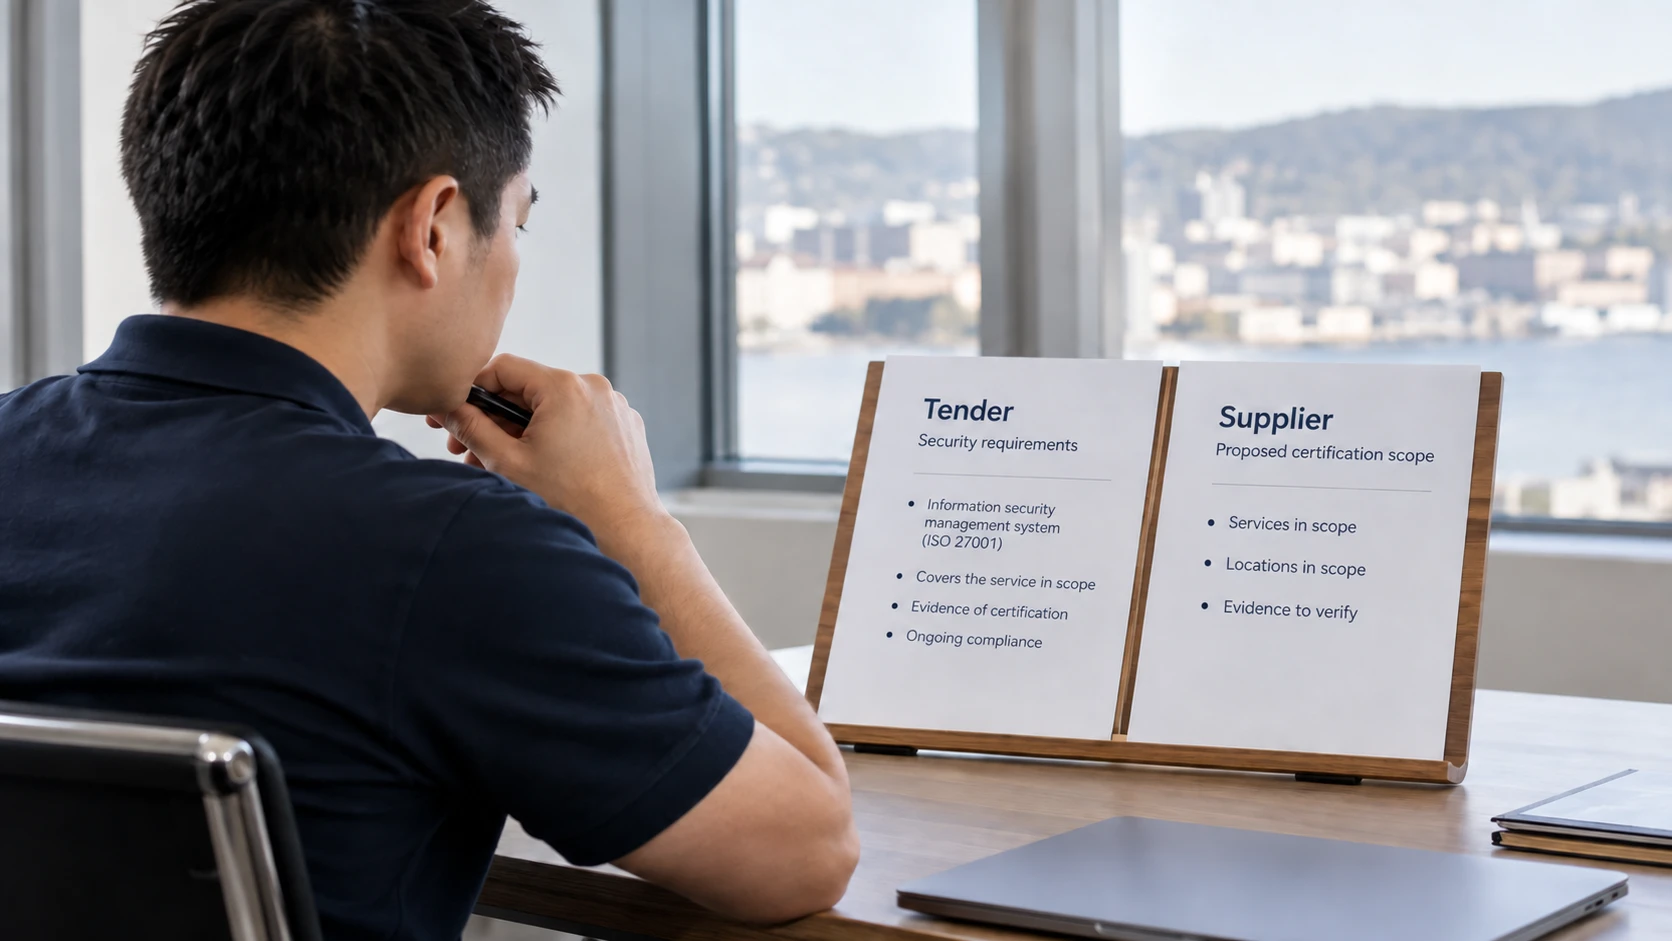
The certificate’s scope matters. A certificate covering one business unit may not cover the service being purchased. Buyers can also ask for additional evidence about the product, data handling, subcontractors or unresolved risks.
Certification is not a universal condition for Norwegian tenders. Read the qualification requirements and permitted evidence for the specific competition. DFØ explains the rules for qualification requirements. Where the wording is unclear, use the formal clarification process before the deadline.
Make the decision against actual demand
List the customers that require certification, the services they buy and their deadlines. Then assess the gap between your current controls and the proposed scope.
This gives management a better investment case than assuming certification will win contracts. It may remove an obstacle, but product fit, price and the rest of the procurement still matter.
If the decision is to proceed, use the ISO 27001 checklist to assign the work. If a request has already arrived, start by clarifying what the customer will accept.