Your customer requires ISO 27001. What do you do now?
Clarify the certificate scope, deadline and acceptable evidence before promising a date. Then assess the gaps and agree a credible plan.
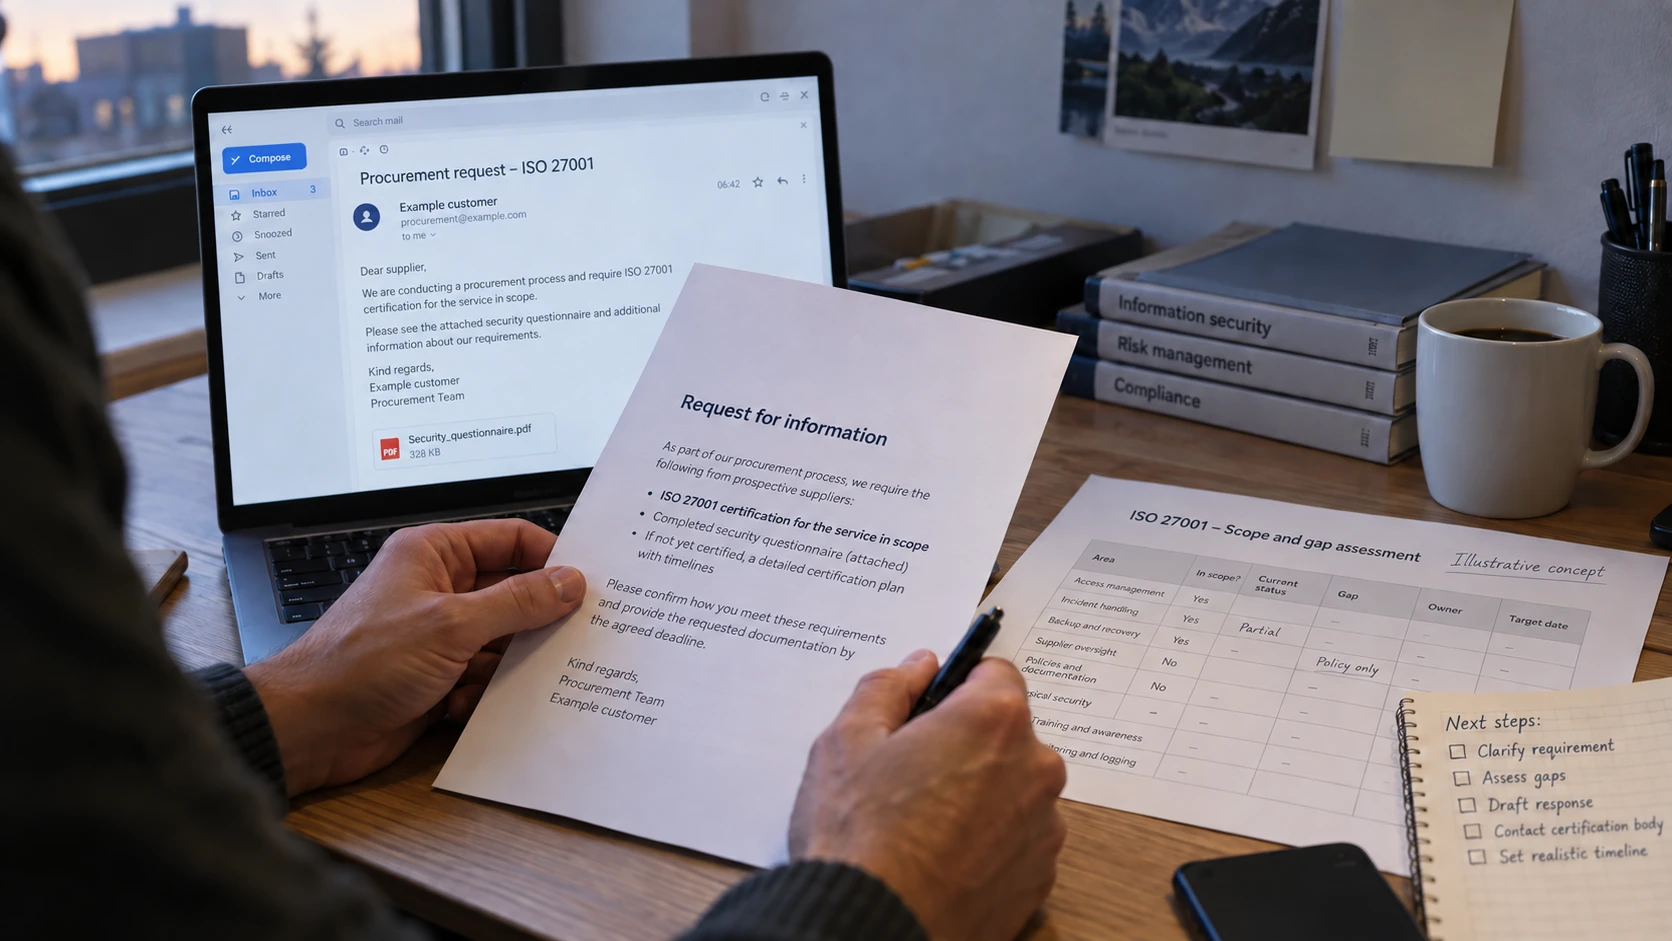
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
When a customer asks for ISO 27001, start with the exact wording. A required certificate, a security questionnaire and a request for a certification plan create different obligations.
Do not answer “yes” because work is planned, or promise a certificate date before checking what preparation and the external assessment will require.
Clarify the requirement
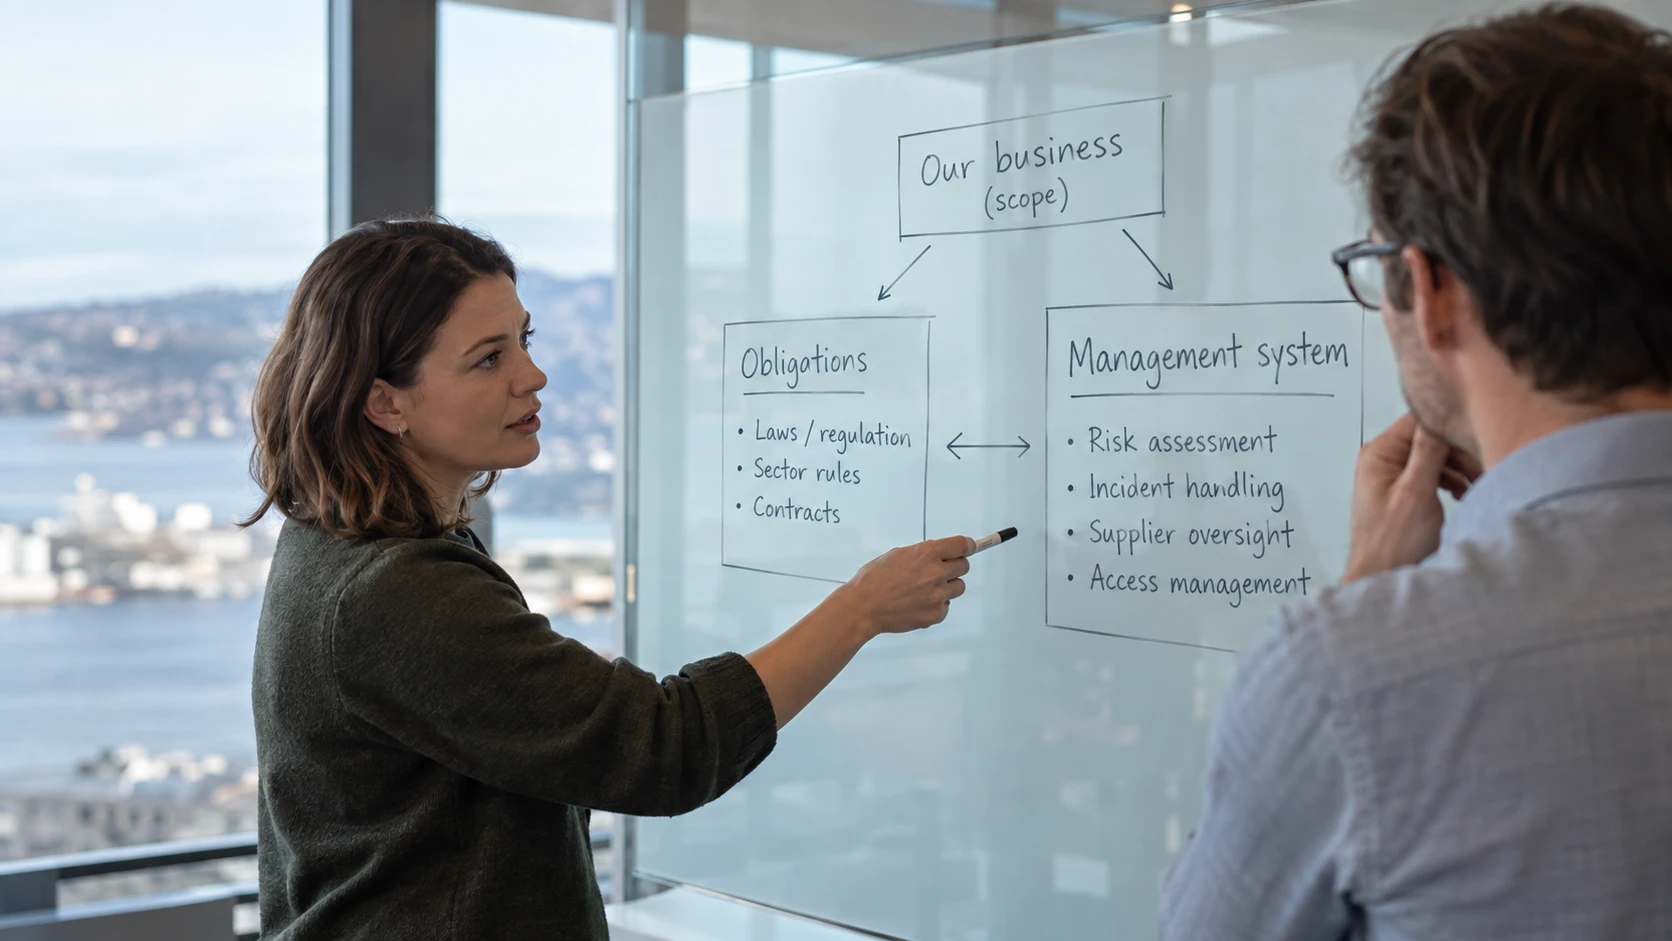
Ask which legal entity and service must be covered, which version of the standard is required and when the evidence must be supplied. Establish whether the deadline applies at bid submission, contract signature or service commencement.
If alternative evidence is possible, ask what the buyer will accept. A plan is not equivalent to a certificate unless the buyer explicitly agrees to it. For public procurement, use the stated clarification channel and follow the competition’s rules. DFØ’s qualification guidance explains the framework.
Establish what is true today
Check the proposed scope against existing controls and records. Access management, recovery, incident handling and supplier oversight may already exist, but they need assessment rather than assumption.
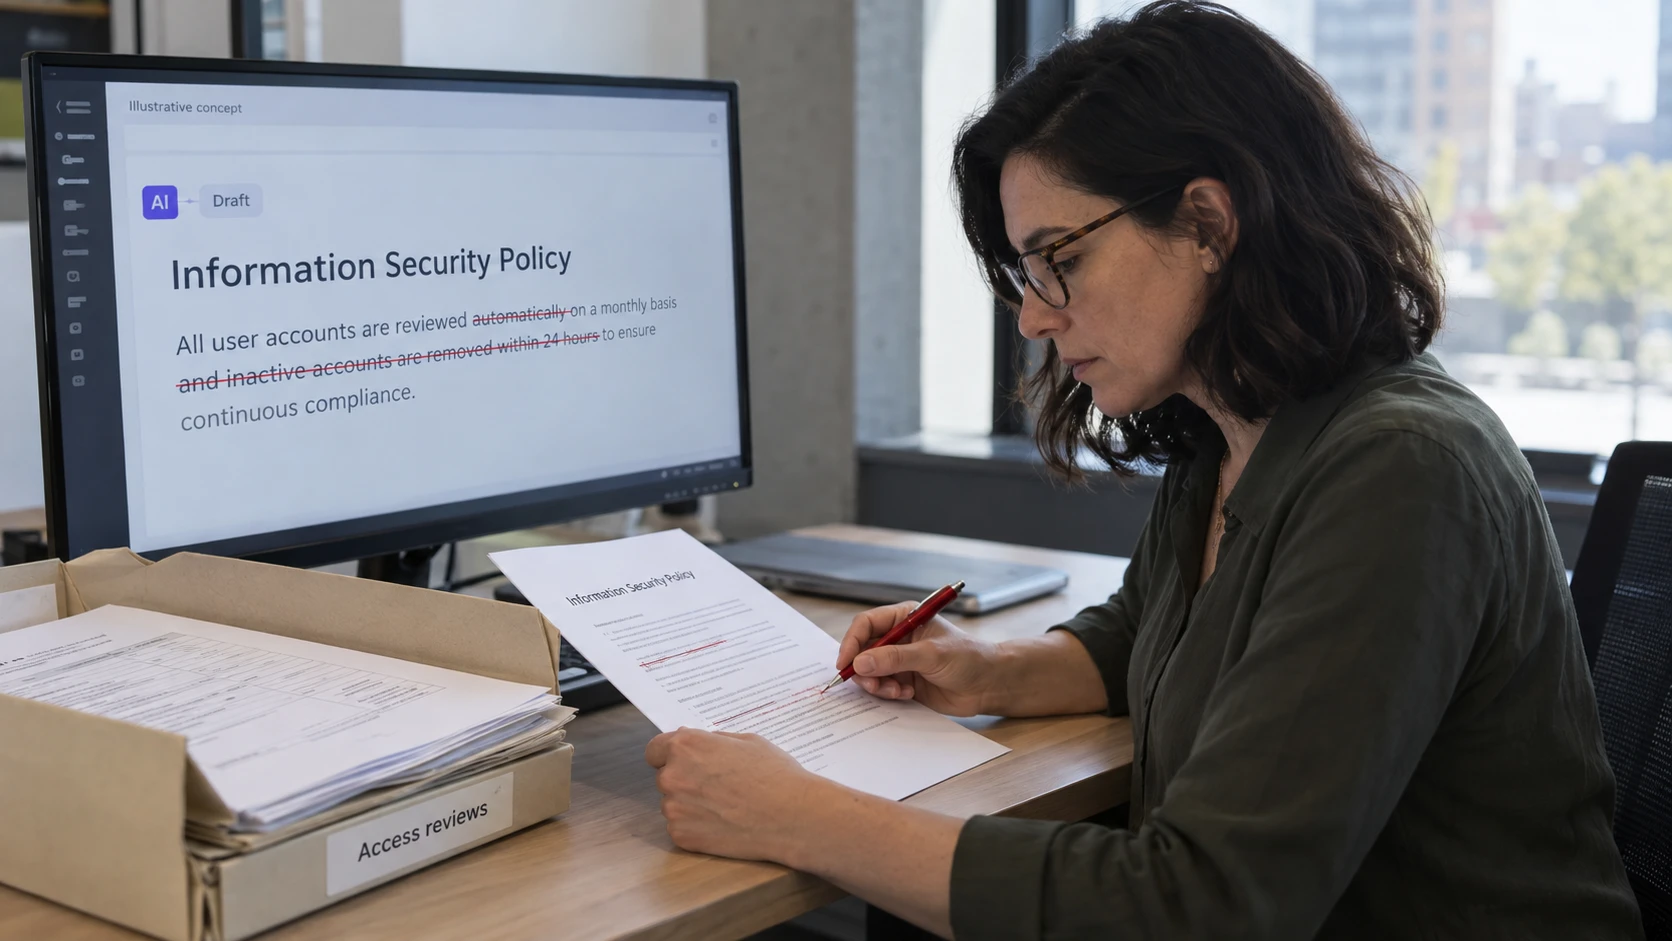
Distinguish a documentation gap from an implementation gap. Writing a backup policy does not demonstrate that the business can restore its service. The latter requires a working process and evidence.
Use the ISO 27001 checklist to give the gaps owners and dates.
Send a precise interim response
A useful reply can be short:
We are not currently ISO 27001 certified. We are assessing the scope covering this service and will provide a dated implementation plan by the agreed deadline. Please confirm whether you require an issued certificate at contract signature or will consider the proposed interim evidence.
Only say that an audit is booked when the certification body has confirmed it. Share detailed security records through an appropriate channel, rather than attaching sensitive findings to a broad sales email.
Set a plan the business can support
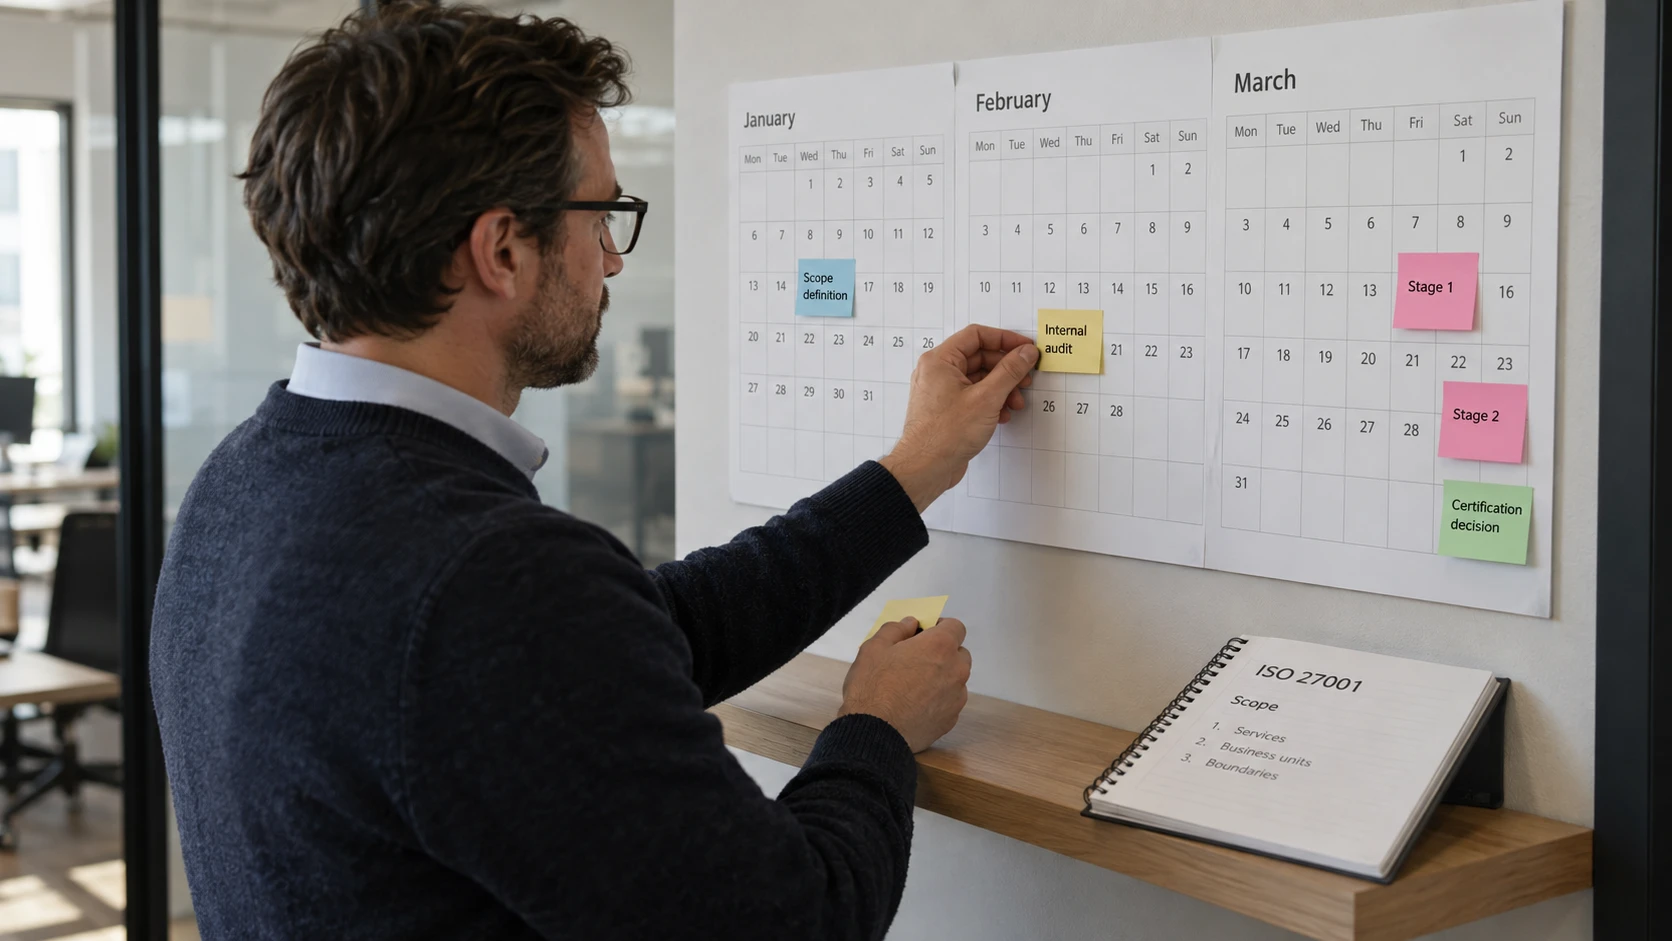
Estimate preparation from the gaps, available people and evidence requirements. Contact a certification body early and leave room for findings and the certification decision.
FM’s ISO 27001 service can support that preparation. The customer conversation should remain anchored in what is complete, what remains and which dates are confirmed. That gives the buyer something concrete to assess without overstating your status.