Why Tenable is part of FM's exposure management service
Tenable provides assessment and exposure analysis. The service around it must connect findings to asset owners, business priorities and verified remediation.
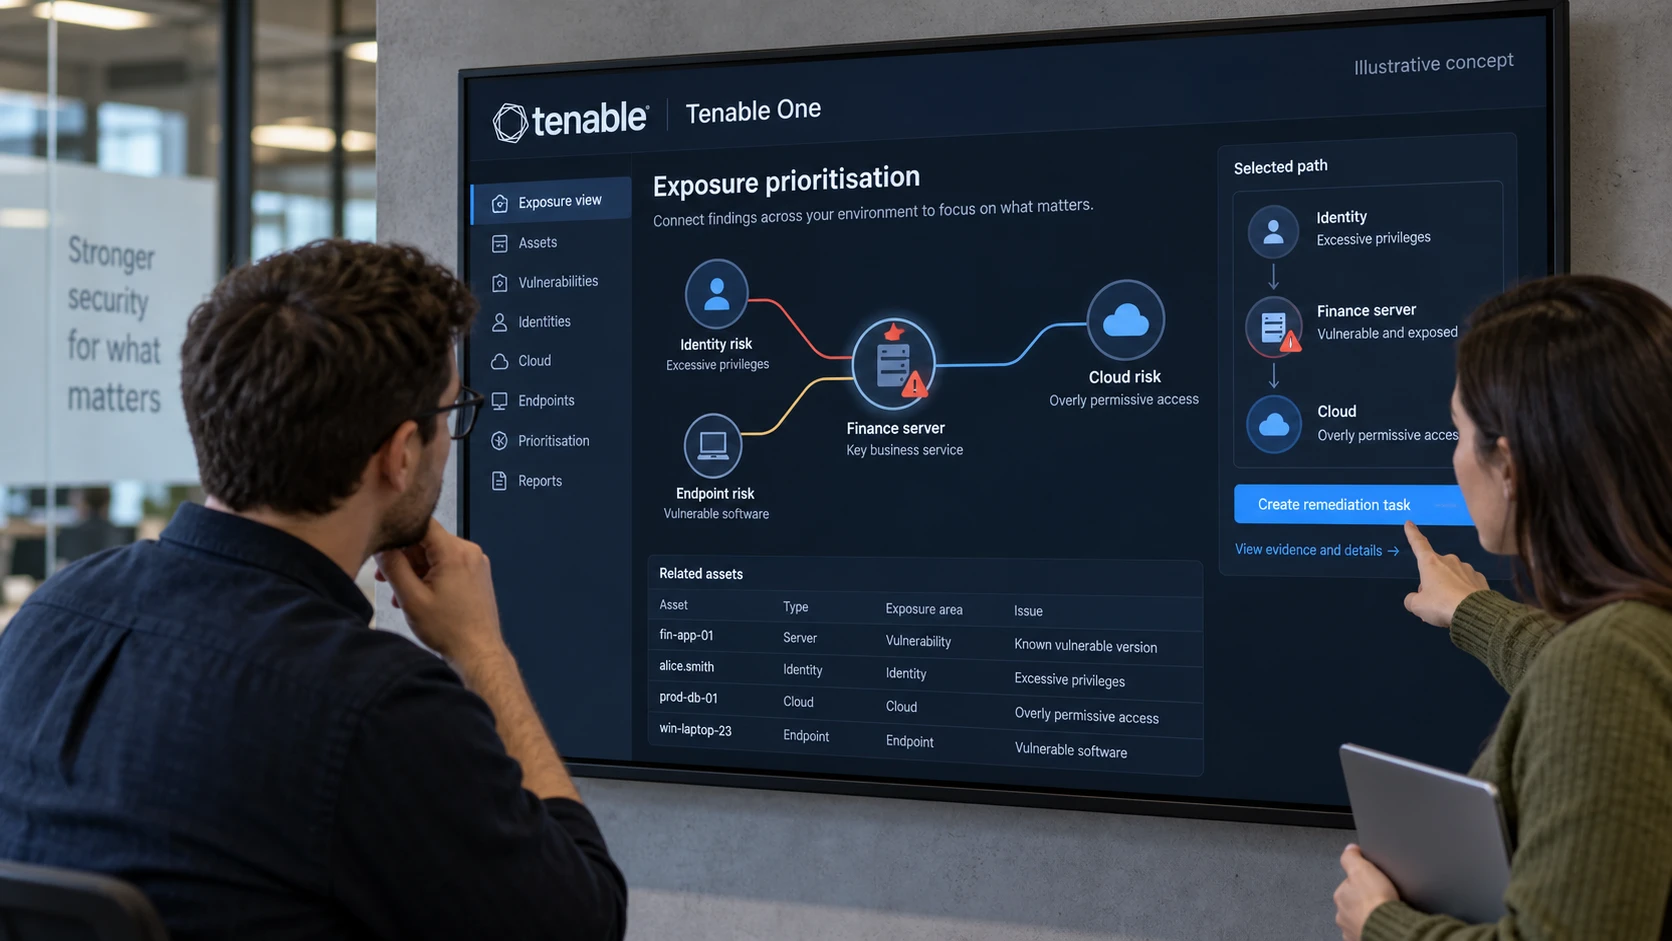
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
FM CyberSecurity’s exposure management service uses Tenable as a platform for assessment and prioritisation. The reason to use a platform is to make findings easier to connect and act on, while keeping the evidence behind a decision available.
The platform’s role
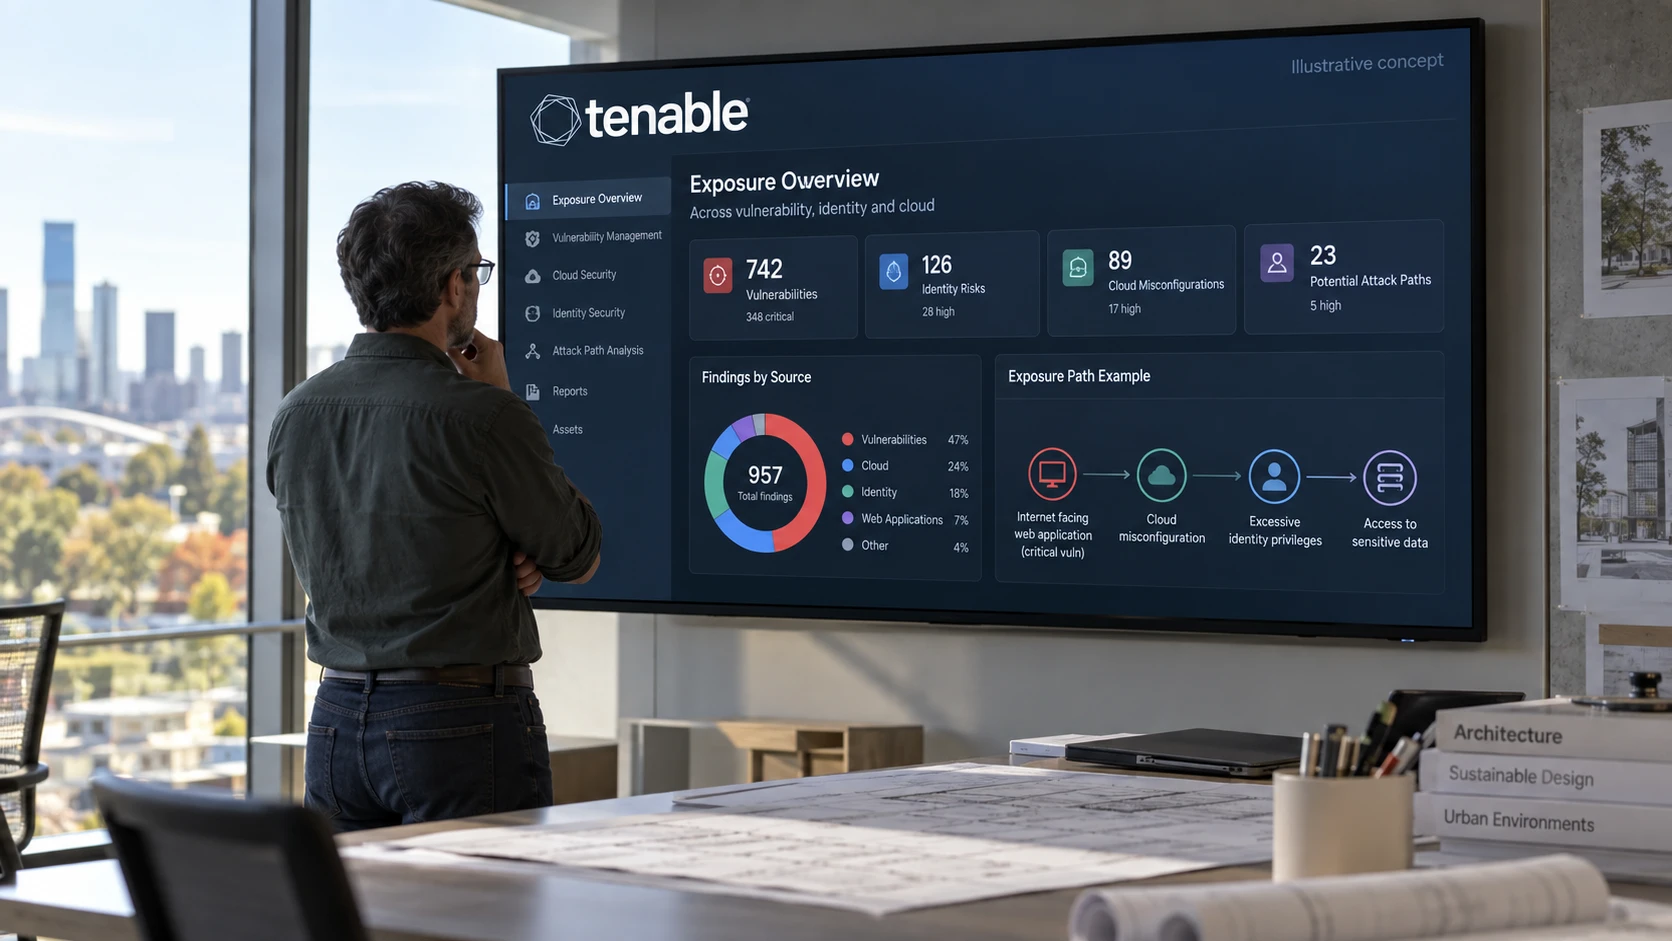
Tenable One brings several exposure areas into a common platform. The available view depends on the package, components and data connected to it.
That can support a question such as whether a vulnerable system lies on a route to an important service. It can also help bring findings from different teams into a shared prioritisation discussion. Neither outcome is automatic: asset matching, collection health and business context need attention.
The product comparison explains where a narrower scanner or vulnerability-management service may be sufficient.
The work around the tool
A useful engagement defines authorised scope, collection methods and ownership. Findings then need validation and a decision: remediate, apply an interim control, investigate further or accept the risk through the appropriate authority.
Tagging assets to business services helps communicate consequences. It should not hide other findings or imply that systems without a customer-contract label do not matter. Recovery infrastructure and internal dependencies can be critical too.
Reports should explain changes in risk and the decisions required. The people applying fixes need the technical detail; management needs material consequences and accountability.
Set expectations before deployment
Agree which activities FM handles and which remain with your team or another supplier. Assessment does not automatically include patch deployment, identity changes or round-the-clock response.
Confirm the module scope and operating effort as well as the licence. Tenable Identity Exposure is distinct from privileged access management and is not automatically part of FM’s Secured offering.
The ongoing programme guide describes a practical way to organise follow-up. The measure of progress is a better-understood and reduced exposure, with evidence that the agreed changes took effect.