Publishing a website without a public admin login
A static website can keep publishing separate from visitor traffic. Git, a build pipeline and a controlled publishing service each have a distinct role.
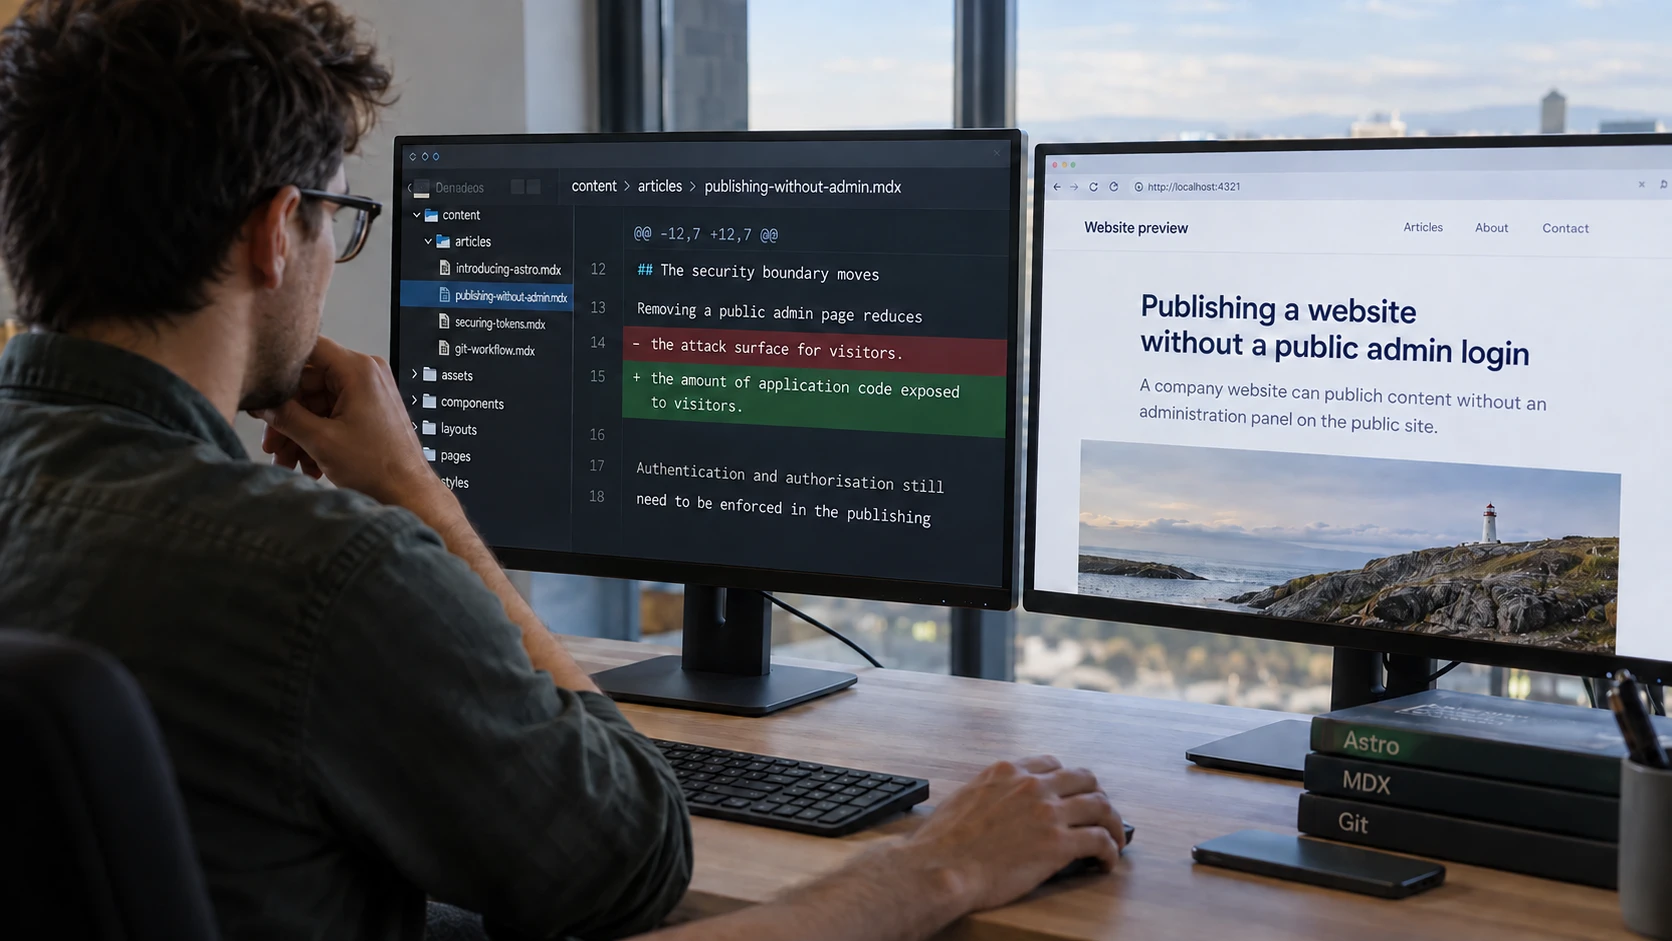
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
A company website needs a way to publish content. That does not require an administration panel on the public site.
FM CyberSecurity’s website stores articles as MDX files in Git and builds them into static pages with Astro. This separates the content visitors read from the system that authorises changes. It also makes articles reviewable alongside the code that renders them.
What the publishing path needs
A publishing service can accept an approved article, validate its metadata and commit the text and images to the repository. An MCP interface can expose those operations to an AI assistant. The build pipeline then checks the content and prepares a deployment.
The assistant is an editor with access to a publishing tool. It should receive only the permissions that role needs. A request to change an article should not grant access to application secrets or unrelated repositories.
For an existing article, check the version before writing. Otherwise two editors can overwrite each other’s work. Keep the text and its required images in the same commit so that a deployment does not reference a missing asset.
The security boundary moves
Removing a public admin page reduces the amount of application code exposed to visitors. The publishing service, identity provider, repository credentials and build system still need protection.
Authentication establishes who the publisher is. Authorisation decides which changes that identity may make. Both need enforcement in the service, regardless of what the assistant says the user intended.
Revocation also needs an explicit design. Disabling an Entra account does not automatically invalidate every token or session issued by another application. Microsoft documents potential delays and application-specific session handling. Define token lifetimes, renewal checks and an emergency way to remove access.
Git helps with review and recovery
A commit records a change, but its author field alone is not proof of who approved publication. Combine repository history with authenticated publishing records and appropriate branch protections.
A bad article and a failed build require different responses. Correct the content in Git; use deployment controls when a release needs to be reverted. Cloudflare Pages supports rollback to a previous production deployment. Reconcile the repository afterwards so the next build does not restore the problem.
This approach fits a site whose main job is serving published content. A customer portal with accounts and transactions has additional requirements. Choose the architecture around what the site does, then secure the path that can change it.