Endpoint Security
MDR, EDR, and endpoint security in practice, from our CrowdStrike Falcon operation.
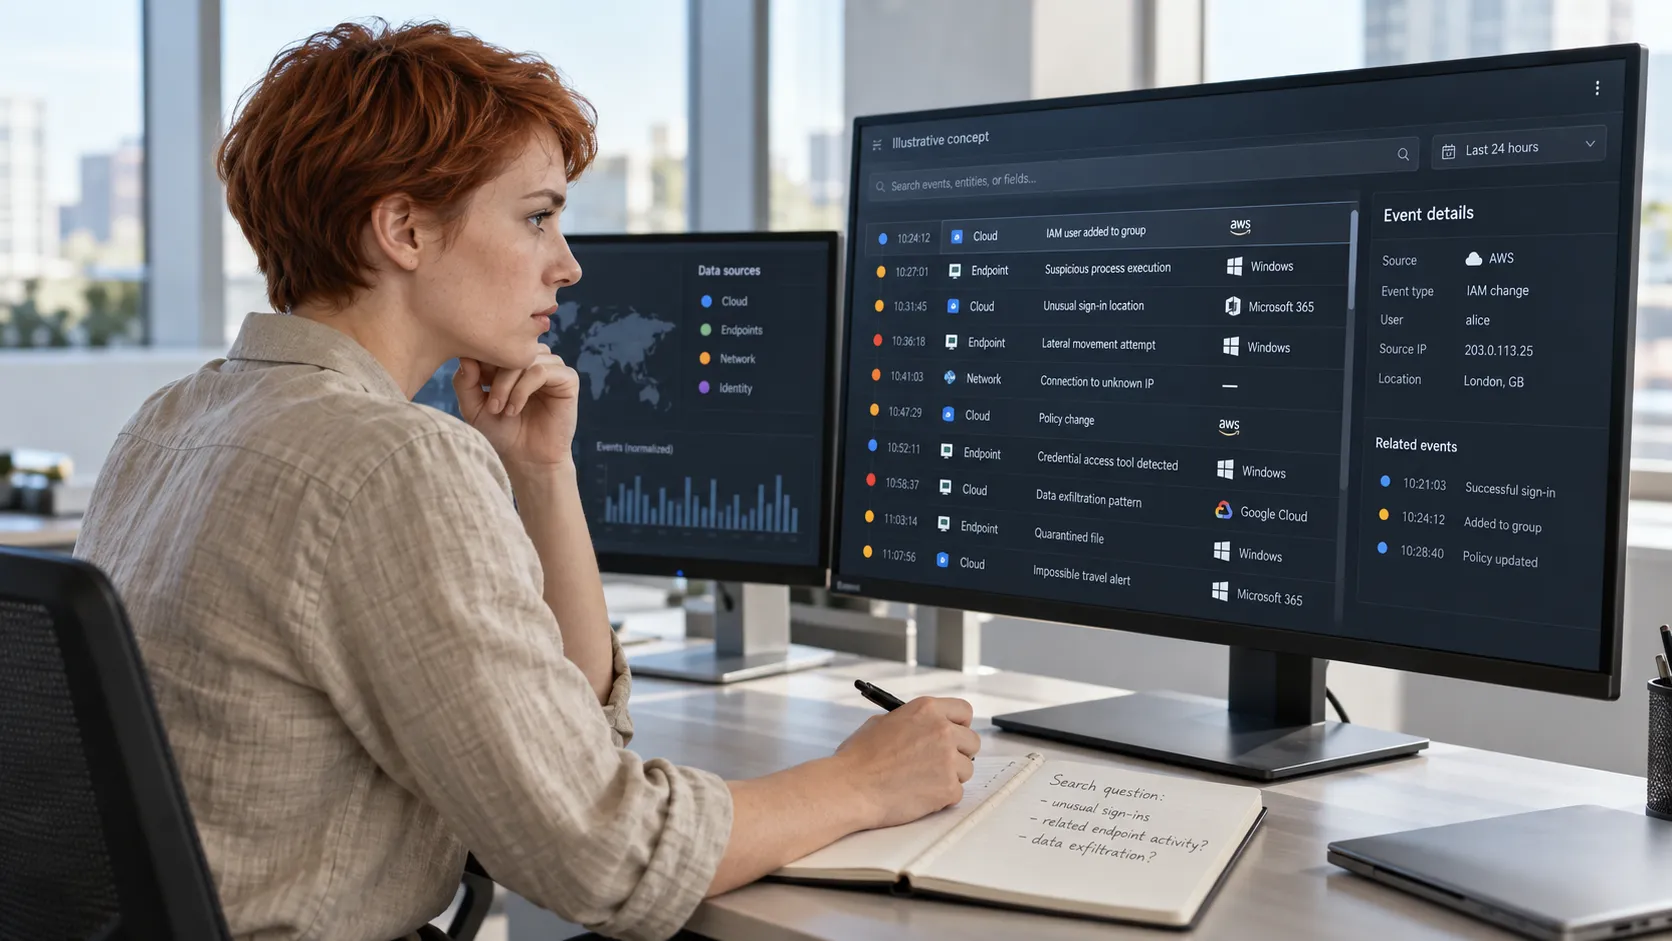
The next-gen label does not define one architecture or price model. Evaluate source coverage, detection, search, retention and the work behind the service.
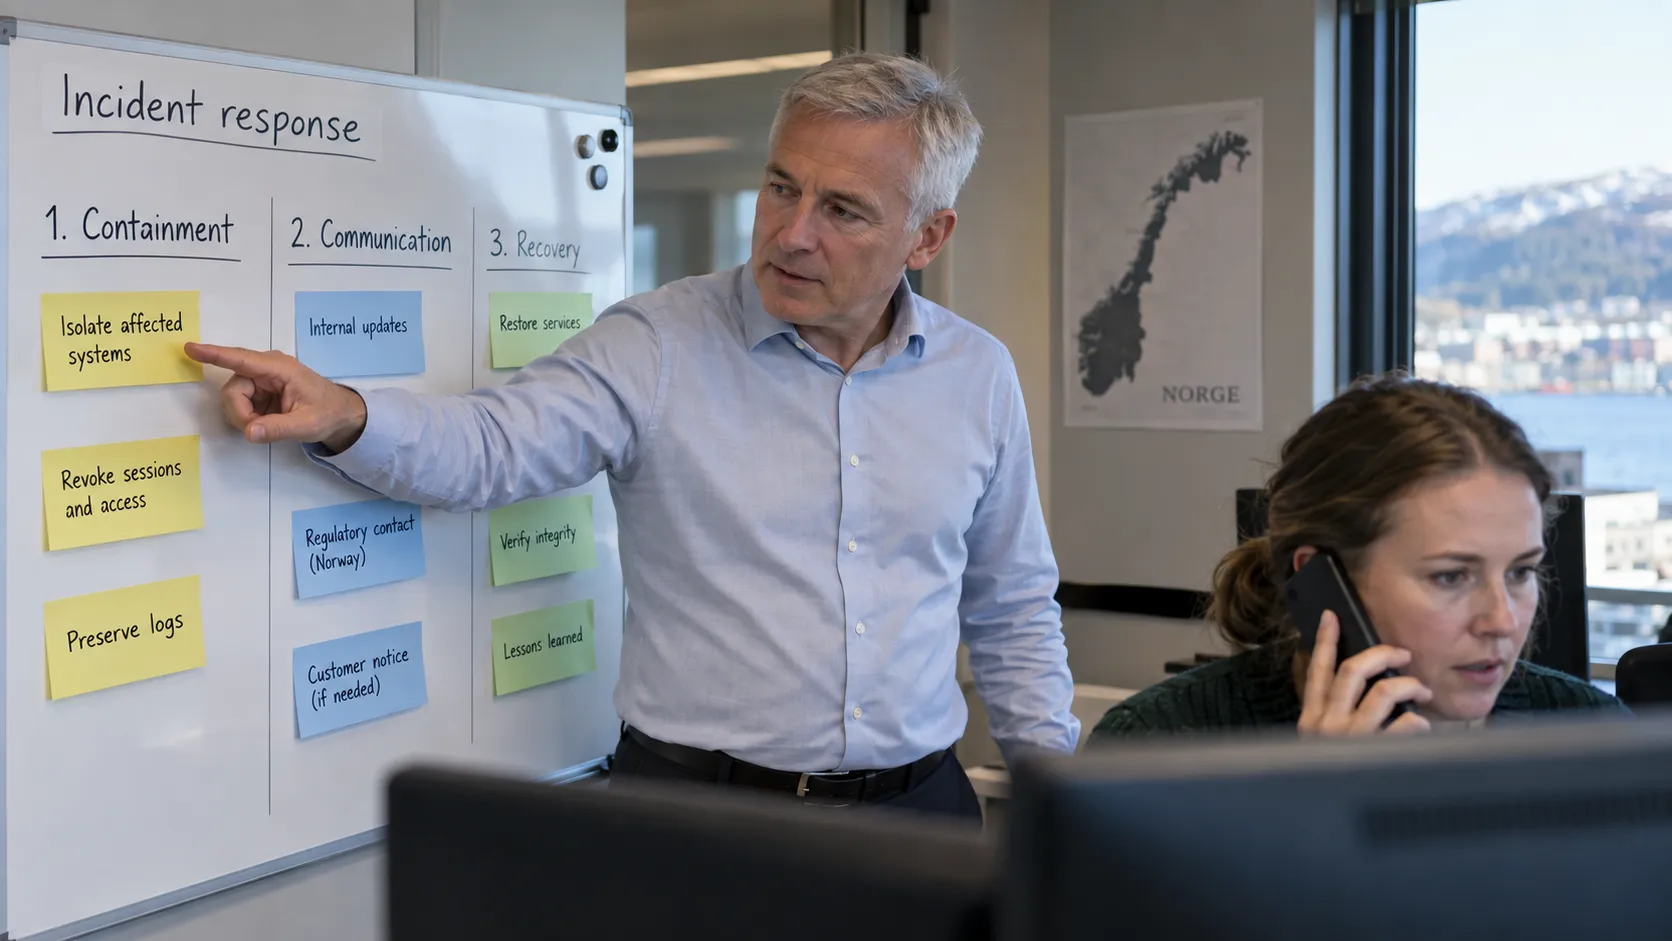
A response plan should identify who can act, how evidence is preserved and which notifications apply. The first decisions depend on the incident, not a fixed script.
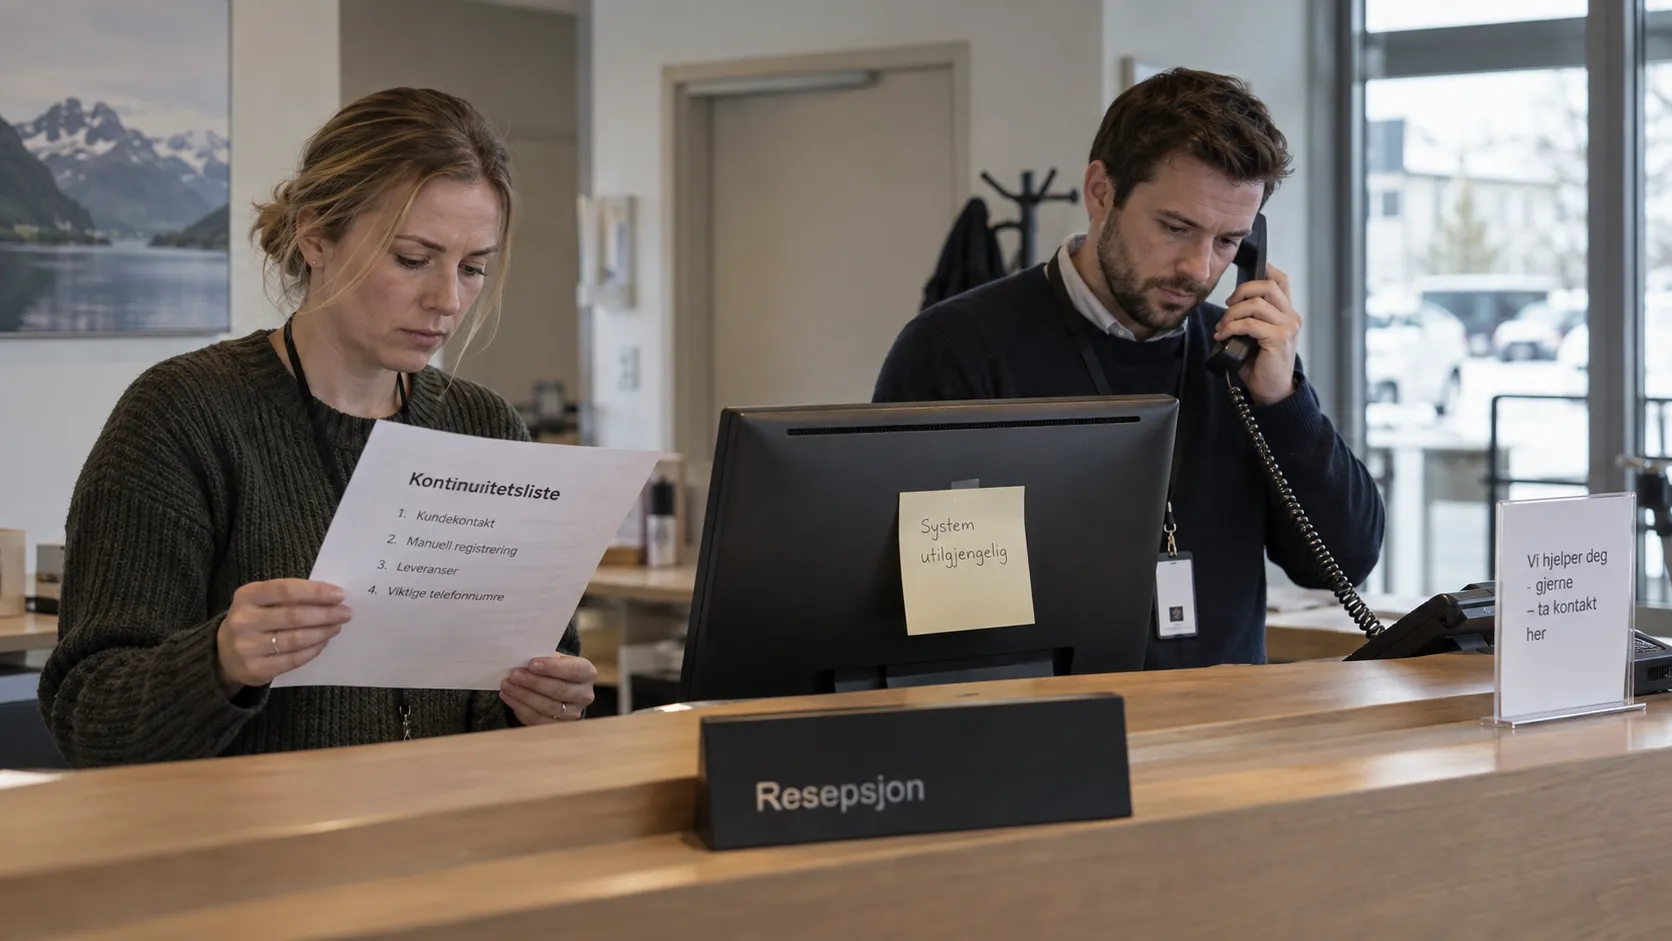
Ransomware can affect availability, confidentiality and recovery. Norwegian businesses need to assess operational harm and personal-data obligations together.
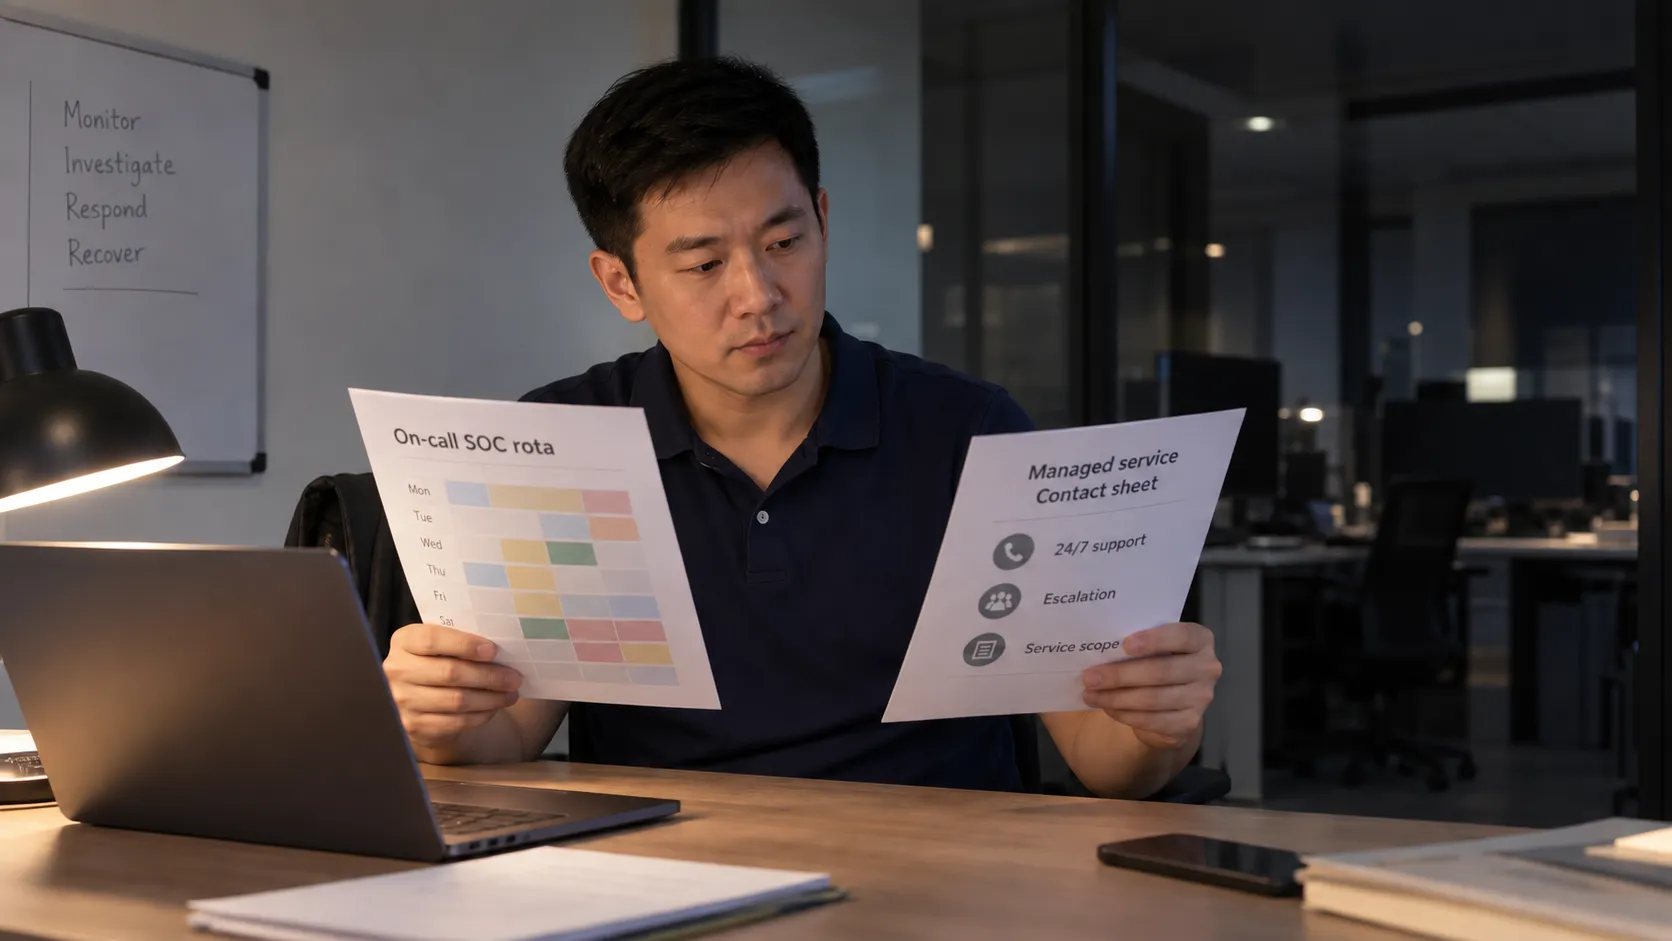
A security operations centre combines detection, investigation and response. In-house, managed and shared models should be compared against the same responsibilities.
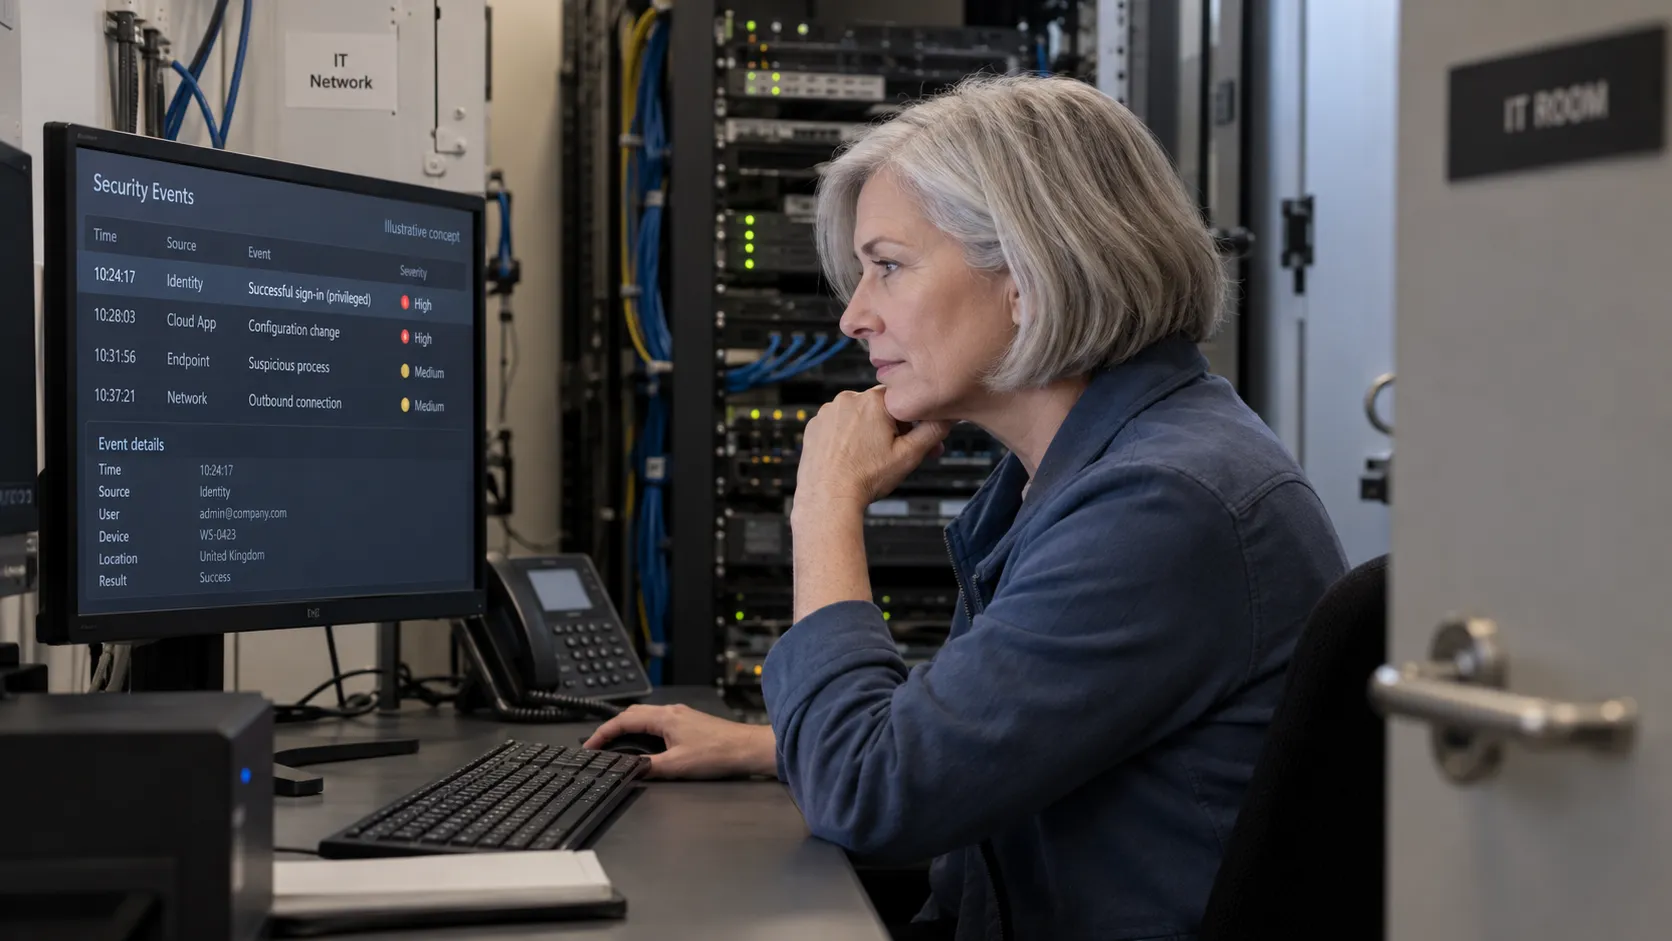
A SIEM collects and analyses security events across systems. Start with the detection and investigation gaps, then decide how the service will be operated.
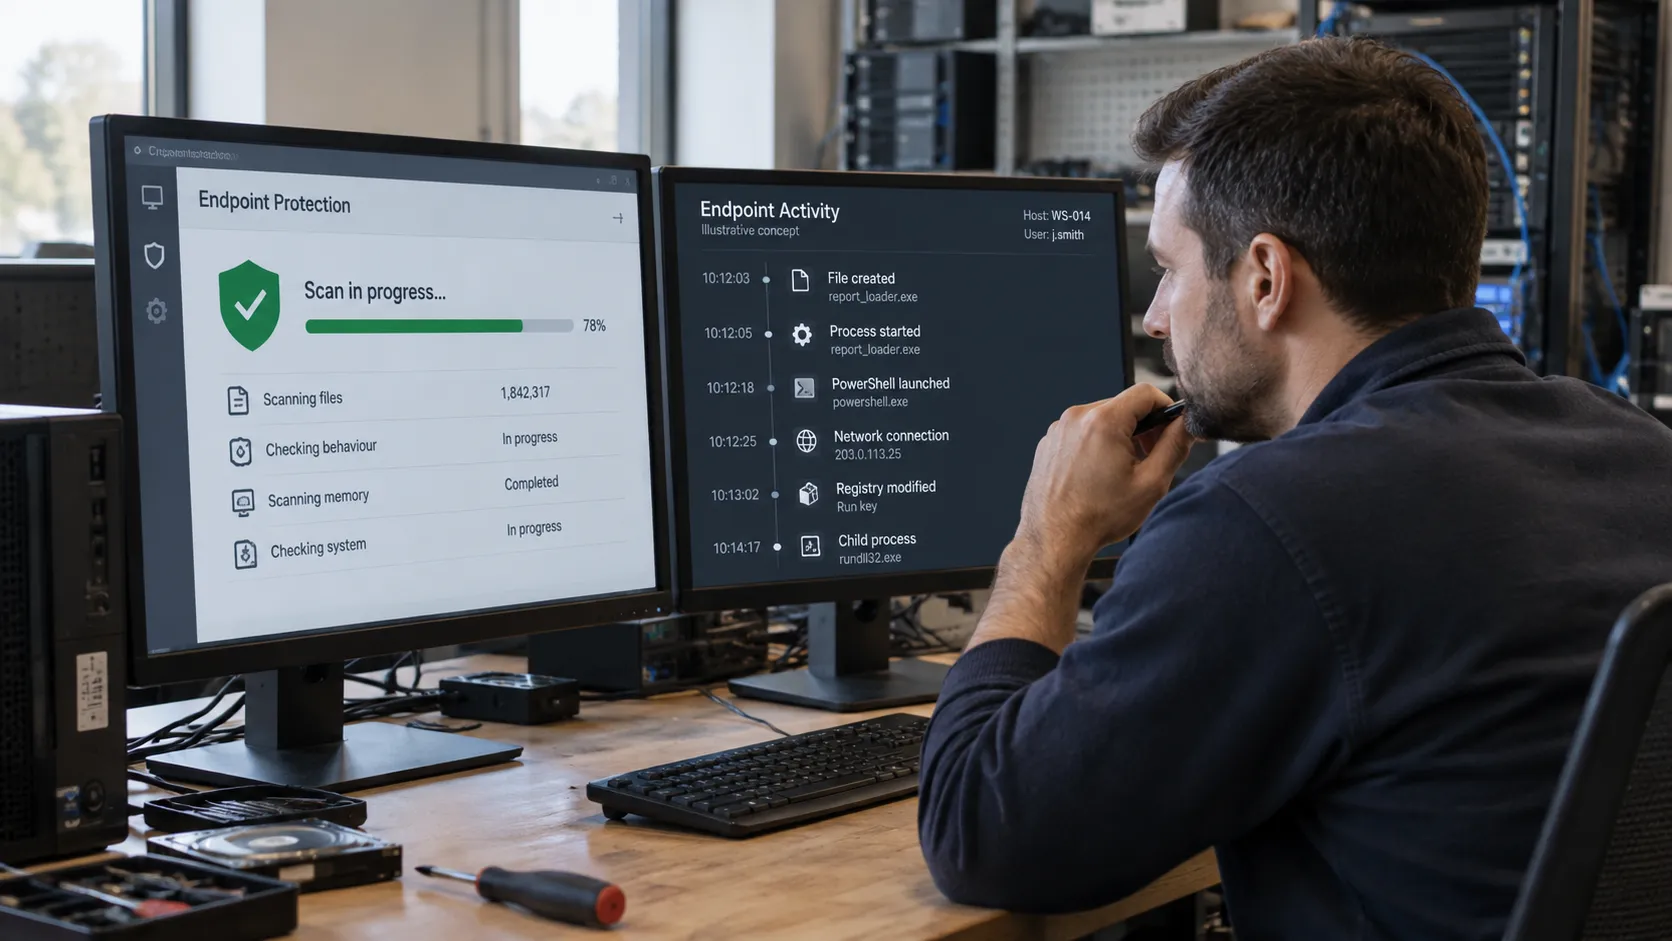
Modern antivirus does more than match known files. EDR adds investigation and response capabilities. Check the coverage and who acts on the alerts.
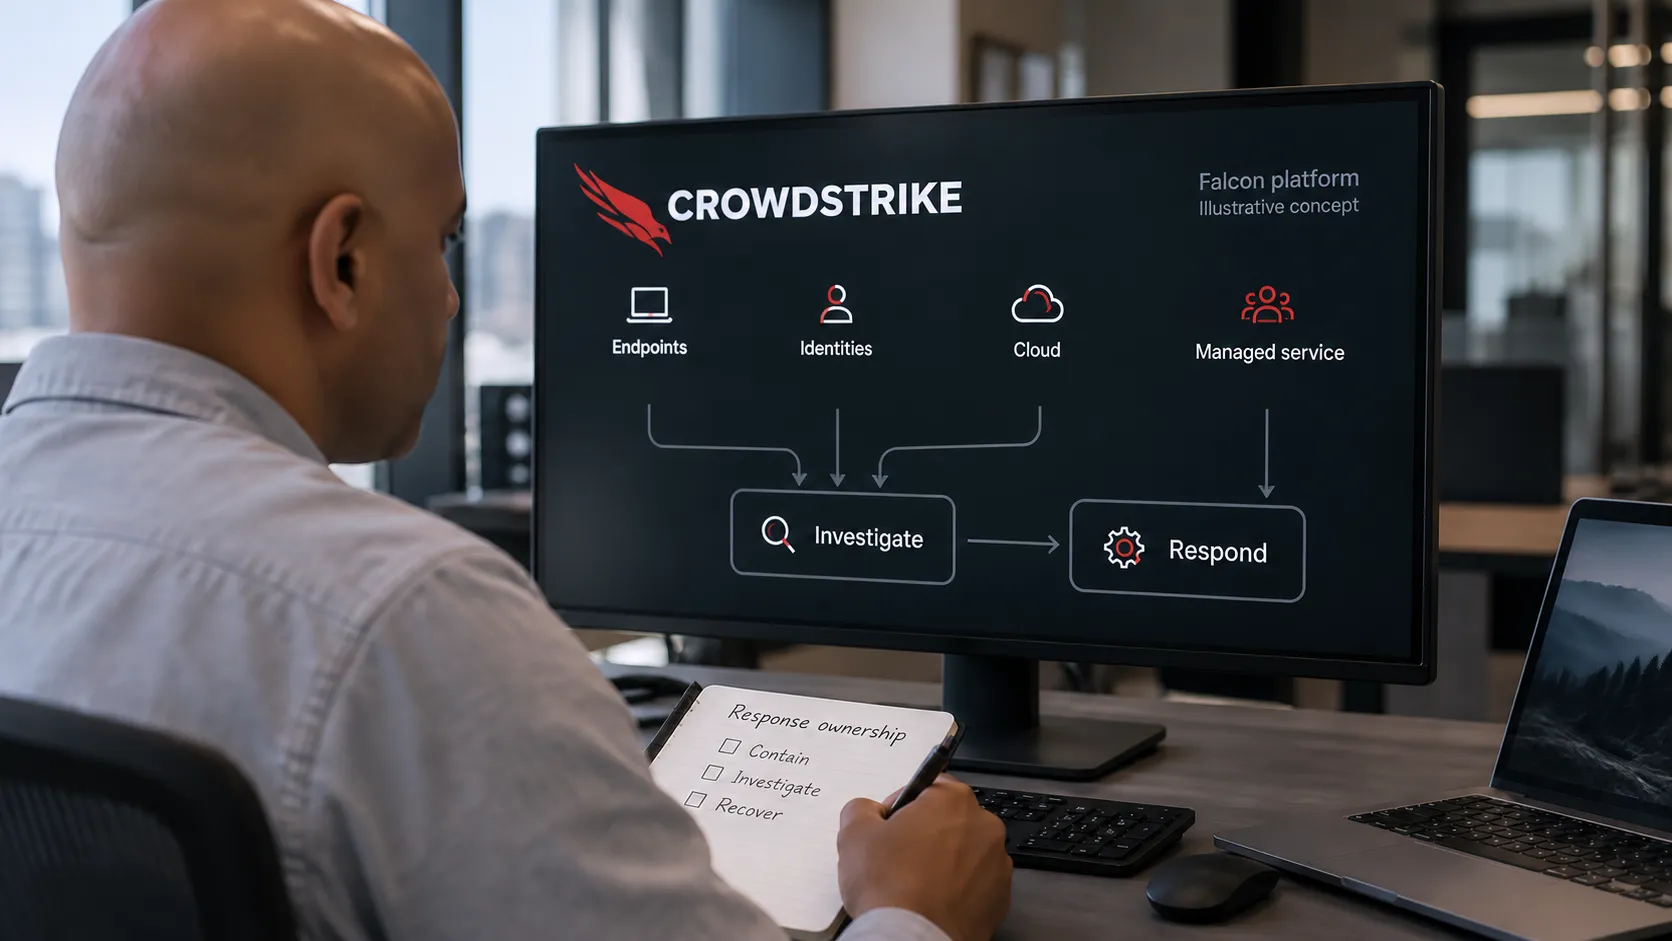
Falcon brings endpoint, identity and other security capabilities into a shared platform. Modules, integrations and the managed service have different roles.
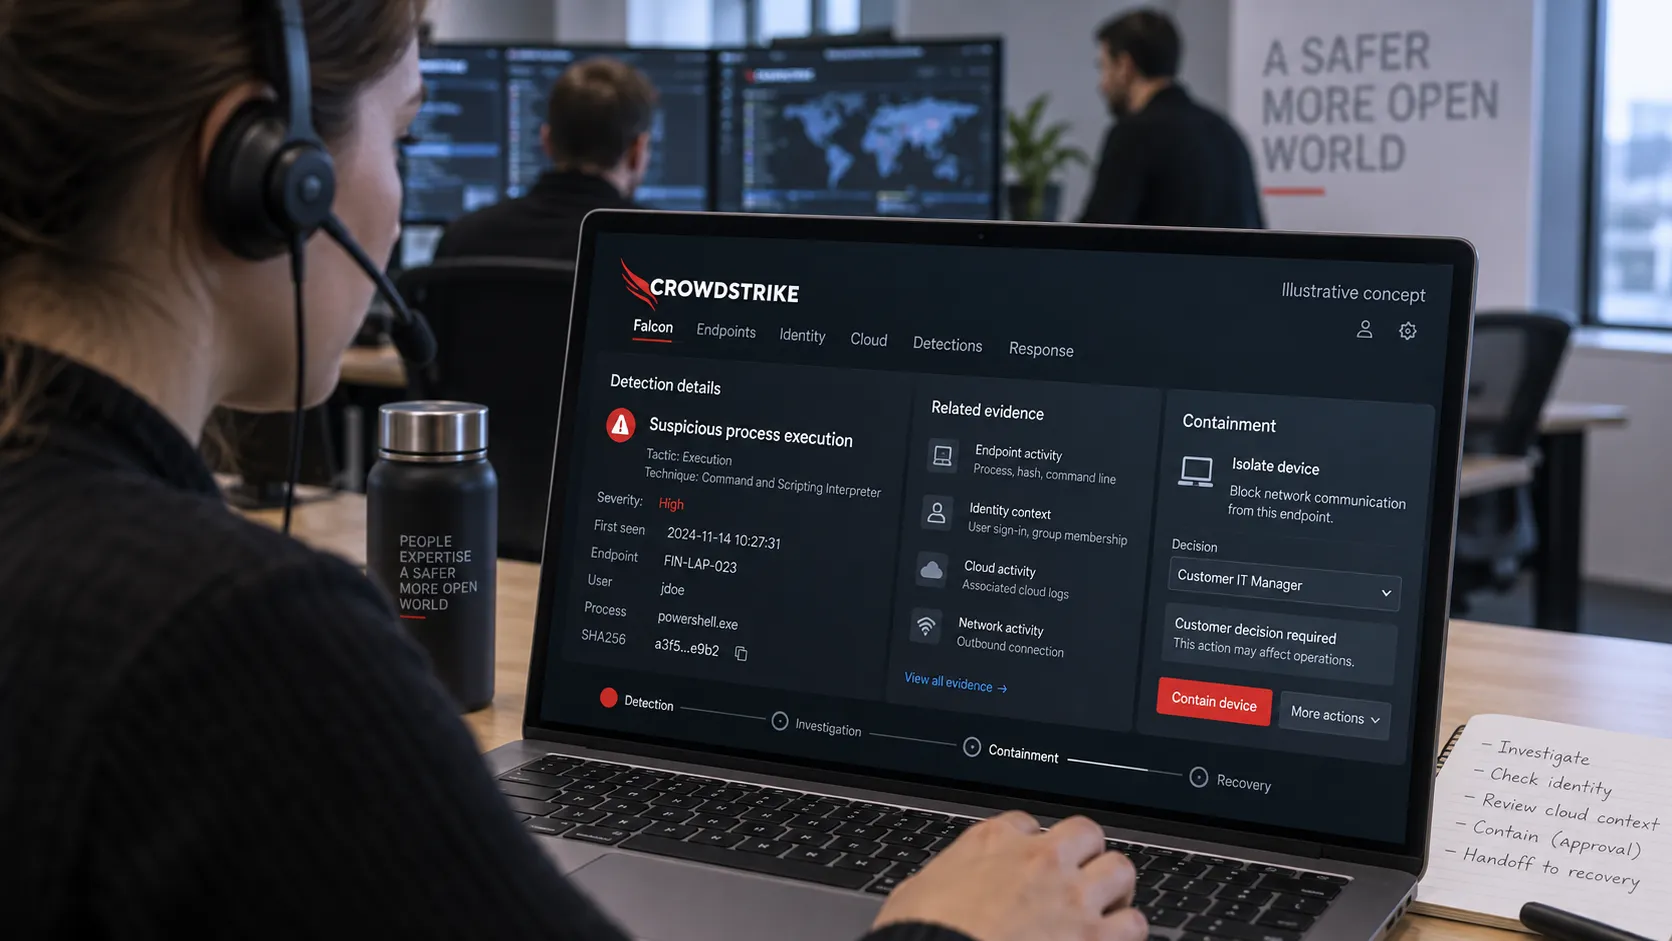
Endpoint and identity signals need an agreed response process. Falcon provides the platform; the service agreement defines who monitors, contains and escalates.