What to check in a next-generation SIEM proposal
The next-gen label does not define one architecture or price model. Evaluate source coverage, detection, search, retention and the work behind the service.
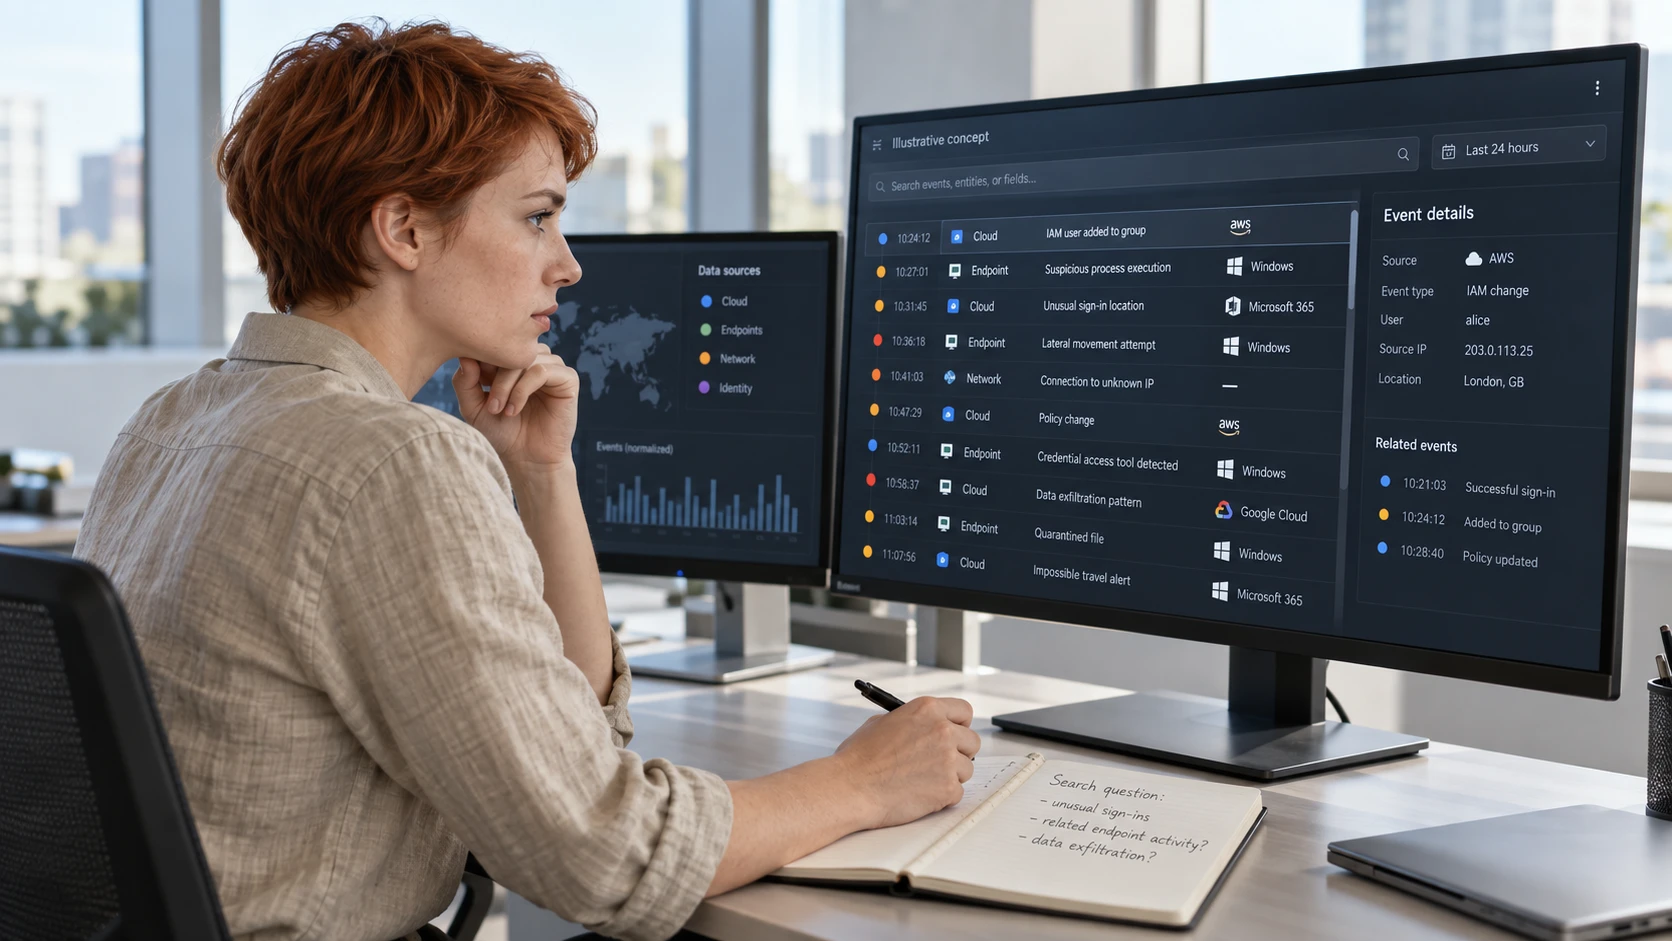
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
“Next-generation SIEM” is a product category label, not a technical standard. Vendors use it for changes in data handling, detection, automation and investigation. The label alone does not establish which architecture or commercial terms a product uses.
CrowdStrike’s Falcon Next-Gen SIEM combines third-party data with its security platform. Evaluate the specific capabilities against your sources and workflows rather than assuming every next-gen product works the same way.
Test the questions your analysts will ask
Use representative data to evaluate search, parsing and detection. A fast query over a demonstration dataset may not reflect your volume, field quality or retention needs.
For each important source, identify the supported integration and the detections that use its events. Verify the fields needed and how missing data is reported. A large library of rules is useful only where relevant rules have the data they require.
AI-assisted investigation also needs review. Check whether the system shows evidence behind a conclusion and what it can do without approval. Automation permissions deserve the same scrutiny as analyst permissions.
Measure the inputs to the quote
Collect a representative period of log volume, including peaks and routine changes. Clarify whether the quote meters raw data, processed data, storage, search or another unit.
Then separate included allowances from paid capacity. Ask how overages, additional sources and growth affect the price. There is no substitute for reading the specific subscription terms.
Retention needs its own discussion. Immediately searchable data, archived data and data queried from external storage can have different costs and retrieval times. Choose against actual investigation and contractual requirements.
Confirm what “managed” includes
An operated service may cover only selected sources or detection use cases. Agree who maintains connectors, tunes rules, investigates alerts and performs containment.
For a Falcon Complete arrangement, confirm the purchased third-party coverage and the split between CrowdStrike, FM and your own team. Do not infer that every log ingested by the platform receives the same managed response.
The SIEM decision guide covers whether the capability is needed. Once that is clear, a good proposal should make its coverage, costs and responsibilities reviewable without relying on the next-gen label.