Data breaches and ransomware: different consequences, connected response
Ransomware can affect availability, confidentiality and recovery. Norwegian businesses need to assess operational harm and personal-data obligations together.
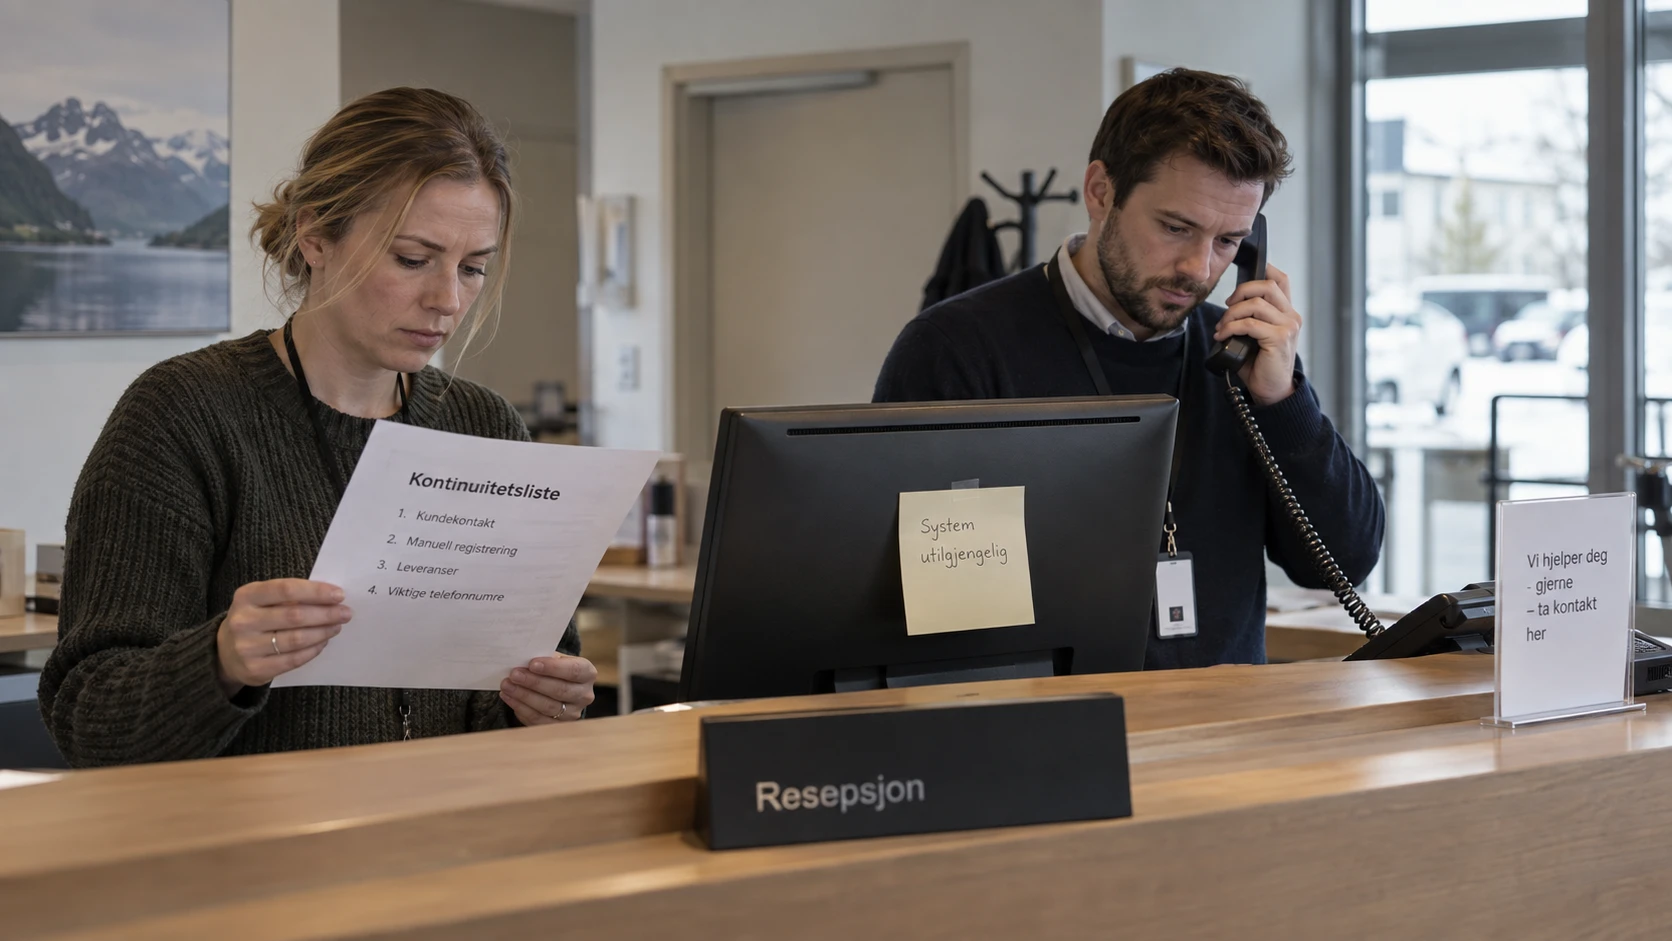
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
A ransomware incident can interrupt operations and expose data at the same time. Restoring systems addresses availability. It does not establish whether information was copied, disclosed or altered.
The distinction matters for response planning. Recovery, privacy assessment and customer communication may need to proceed together, with different people responsible for each.
A personal data breach is broader than theft
Datatilsynet’s definition includes accidental or unlawful loss, destruction, alteration, disclosure of or access to personal data. An incident can therefore raise privacy questions even without confirmed exfiltration.
Ransomware can also threaten publication of stolen information. NSM’s guidance on digital extortion advises against paying. Payment does not itself demonstrate that data has been deleted or remove the need to investigate and recover.
Build the cost picture from the affected service
There is no single useful bill for “a Norwegian breach.” Identify the interrupted work, restoration effort, external assistance, contractual consequences and obligations toward affected people.
An unavailable service can have consequences beyond IT costs. Consider manual workarounds, delayed deliveries and dependencies on the same identity or backup infrastructure. Those dependencies should also inform the recovery order.
A denial-of-service event primarily affects availability, but it can coexist with other malicious activity. Investigate it proportionately rather than assuming no other compromise is possible.
Assess reporting early
For a reportable personal data breach, the controller generally has to notify Datatilsynet without undue delay and, where feasible, within 72 hours of awareness. The exception applies when risk to people’s rights and freedoms is unlikely. Datatilsynet sets out that test.
High risk can also trigger communication to affected people, subject to the applicable exceptions. Record the reasoning and revisit it as facts emerge. Restoration from backup does not decide the reporting question by itself.
Prepare for both interruption and investigation
Protect backups from the same credentials and administrative paths as production where possible, and exercise recovery. Keep the logs and contacts needed to investigate access and meet relevant obligations.
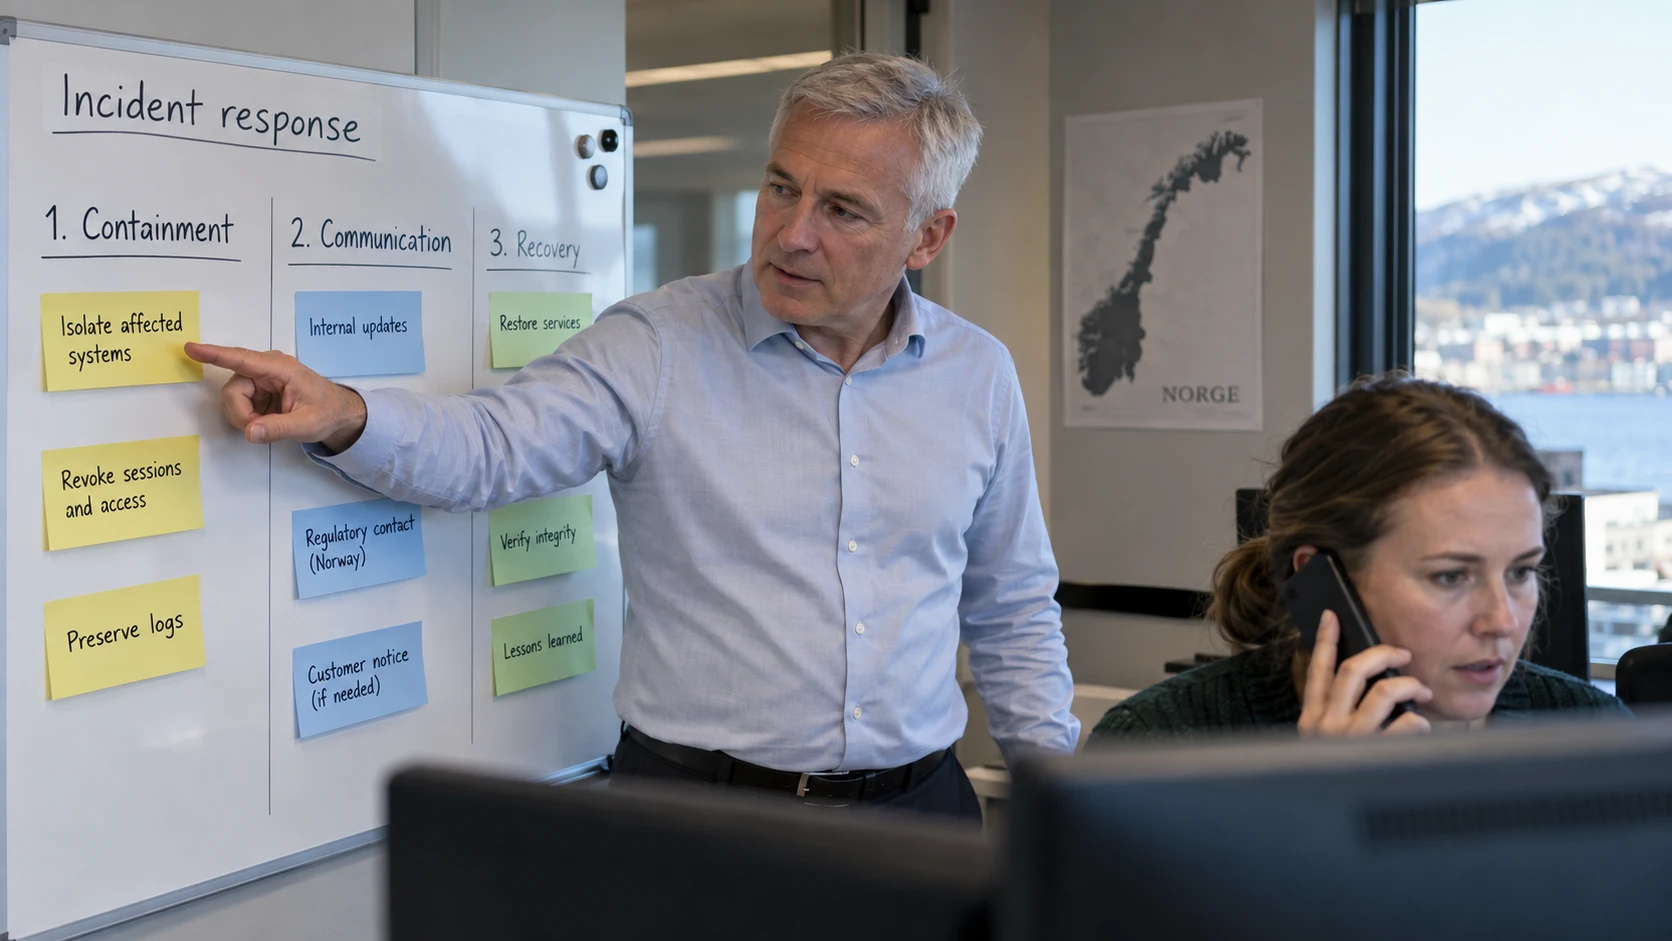
Agree who can authorise containment and who decides when a service is safe to restore. The incident response guide covers those responsibilities. Endpoint monitoring is one part of the preparation; it should sit alongside recovery, identity protection and a workable response plan.