DORA testing: the annual programme and threat-led penetration tests
DORA distinguishes general resilience testing from designated TLPT. Choose methods against risk, document coverage and verify remediation.
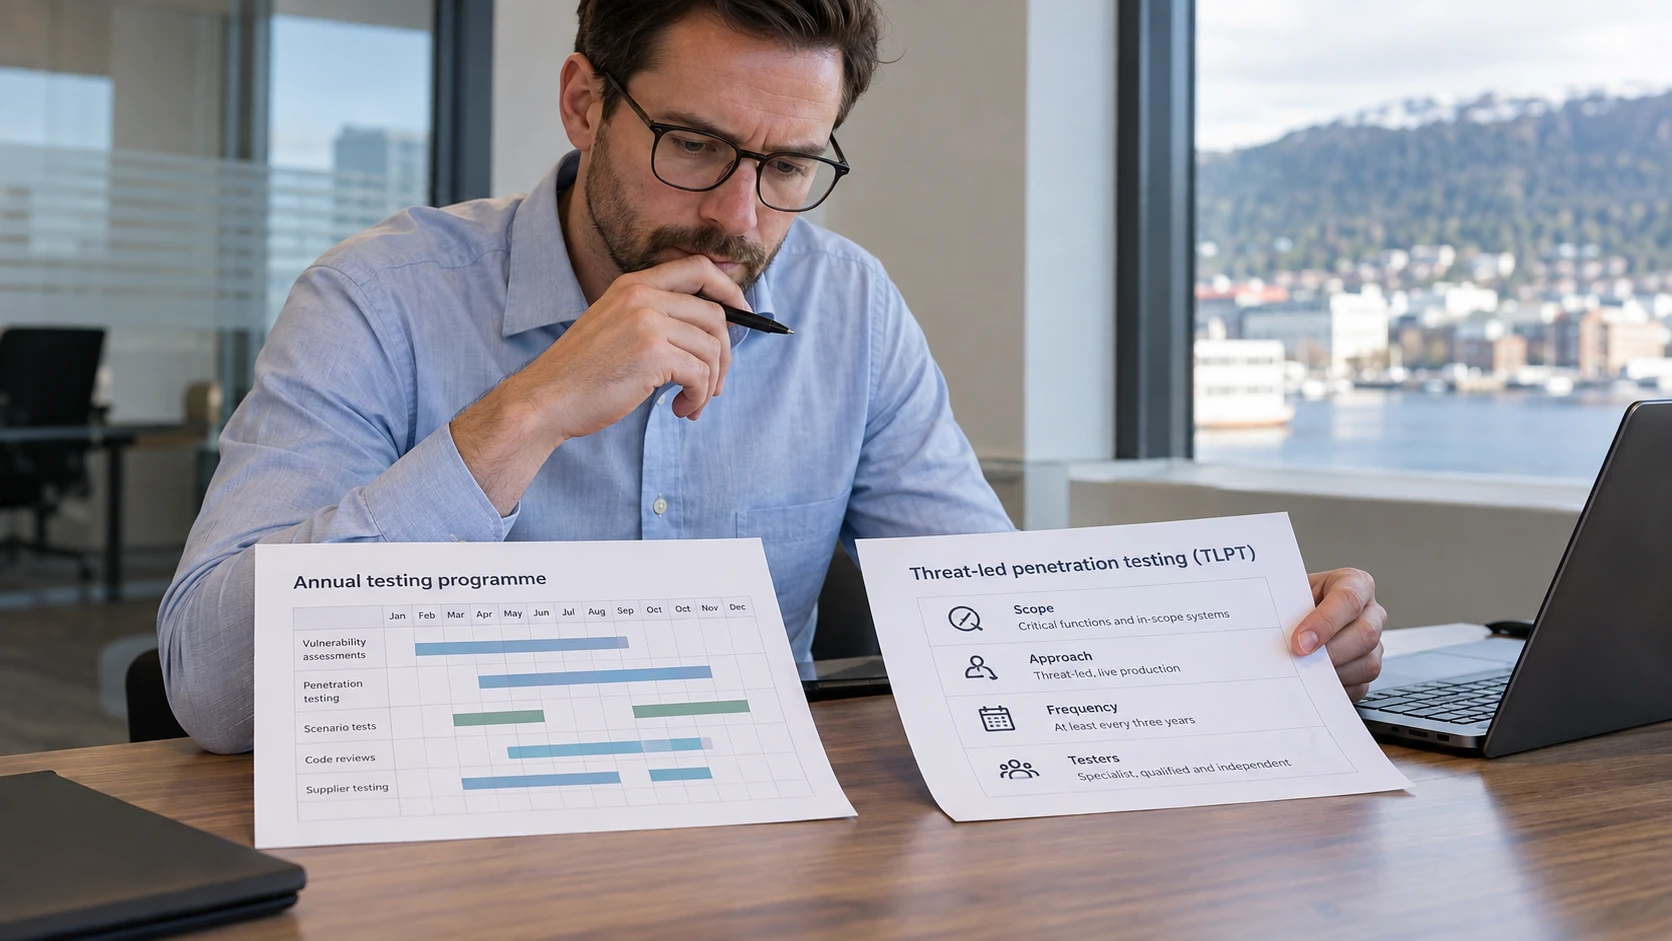
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
DORA separates the general resilience-testing programme from threat-led penetration testing, TLPT. They have different scopes and conditions. Buying an ordinary penetration test does not automatically satisfy either obligation in full.
Begin by confirming the regime that applies to the entity, including microenterprise provisions, the simplified framework and any Norwegian adaptations. The DORA checklist covers that first decision.
General testing is broader than a pentest
Articles 24 and 25 of DORA establish the general testing requirements. For entities covered by Article 24(6), appropriate tests must cover all ICT systems and applications supporting critical or important functions at least yearly.
Article 25 gives a range of methods, including vulnerability assessments, code reviews where feasible, scenario tests and penetration testing. The point is to select appropriate methods and coverage. It is not a universal requirement for one annual manual pentest, nor permission to substitute one automated scan for the entire programme.
Record why each method fits the risk, who performs it and how independence is achieved. Include relevant suppliers and agree authorisation and operational safeguards.
TLPT is a separate, specialised obligation
Under Articles 26 and 27, designated entities must undertake threat-led testing under specific requirements for scope, process and testers. The normal interval is at least every three years, with supervisory discretion over frequency.
This work involves live production and needs controlled planning. The authority’s designation and applicable technical rules govern the obligation. Do not rely on an old public statement that no firms have yet been selected.
FM’s application testing through Aikido is not a substitute for TLPT or TIBER-NO. A designated engagement requires appropriately qualified providers and the prescribed process.
Coverage and closure are part of the result
Map tests to the systems supporting each important function. Record limitations, unavailable components and changes since the last test. A report title cannot establish complete coverage.
Findings need classification, priority, ownership and corrective action. Verify that important weaknesses have been addressed and preserve that evidence alongside the original report.
Automation can help repeat supported checks and identify changes. Its suitability depends on the target, method, independence and wider programme. The DORA reporting article explains how to keep this evidence connected to governance and review.