What CISSP certification means when picking a cybersecurity consultant
CISSP is a broad security credential with experience requirements. Verify it, then assess the person's fit for your specific systems and assignment.
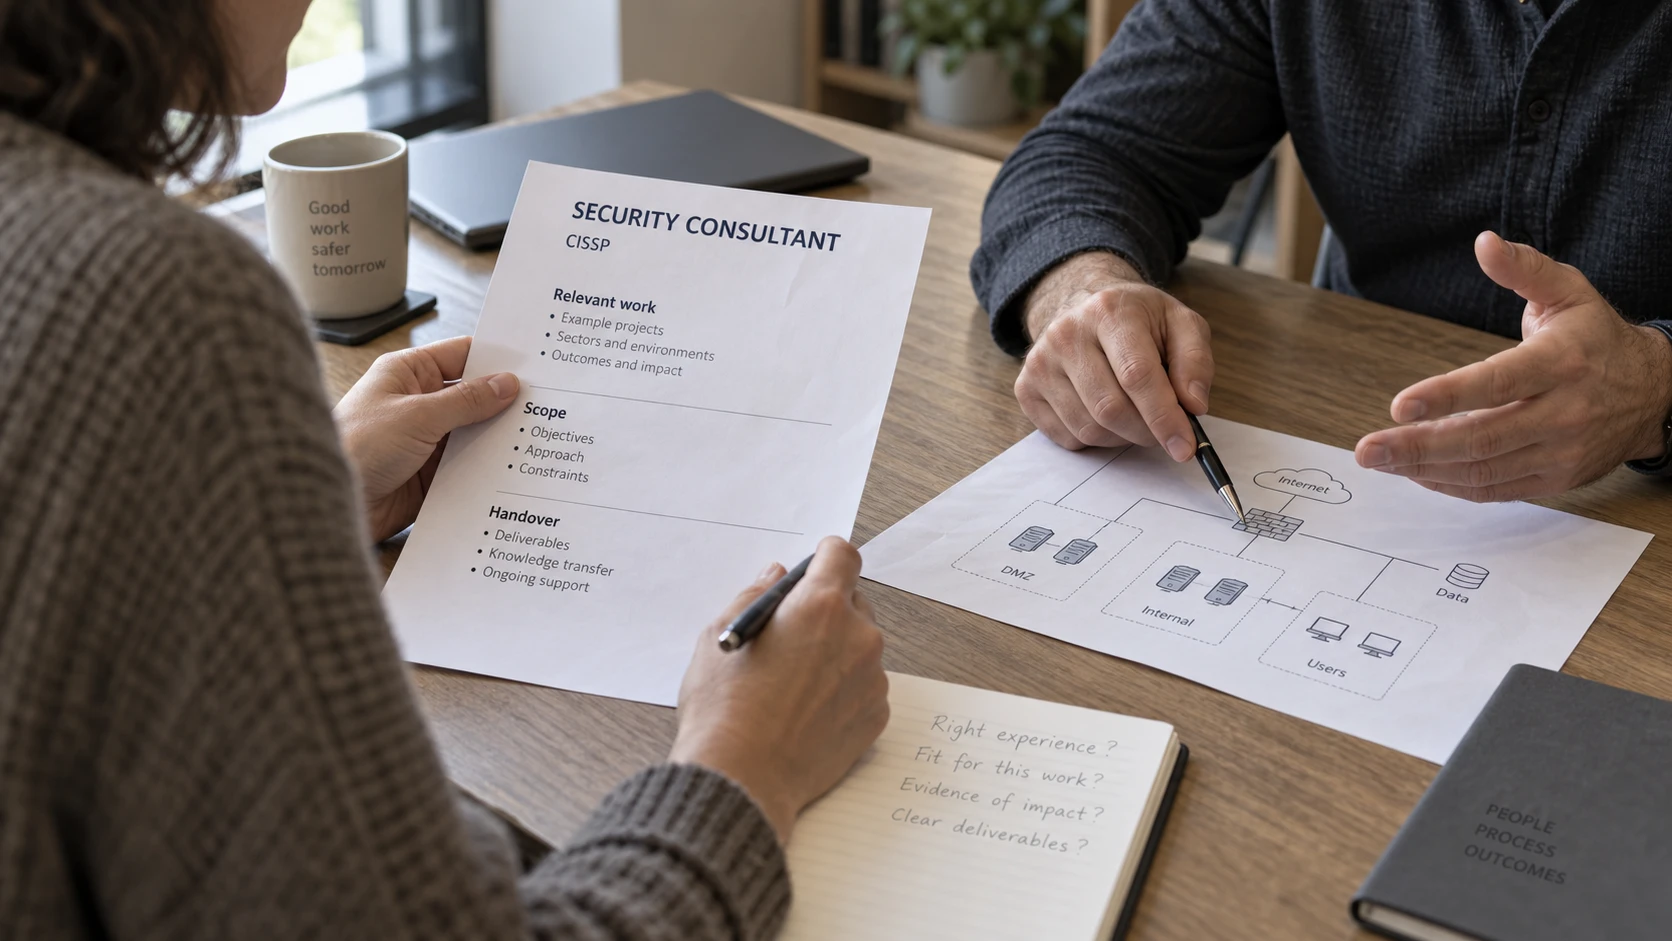
The cover image is an AI-generated editorial illustration. Screens and documents are illustrative concepts.
CISSP can help you assess a cybersecurity consultant’s background. It should not be the whole selection process.
The certification covers broad security knowledge. It does not establish that the holder can configure your particular platform, lead your migration or deliver the exact assessment you need.
What the credential establishes
CISSP stands for Certified Information Systems Security Professional and is issued by ISC2. Its exam outline covers eight domains, including risk, architecture, identity, operations and software security.
ISC2’s experience requirements normally call for five years across at least two domains. An eligible degree or approved credential can waive up to one year. Someone who passes the exam without the required experience may become an Associate of ISC2; that is not the CISSP designation.
Check the credential’s current status through the issuer’s verification process. A course certificate or a claim to have passed the exam is different from current certification.
Assess the work you are buying
Describe the assignment before comparing profiles. Advice on risk ownership, an identity implementation and incident-response support need different capabilities.
Ask the candidate to explain a relevant decision: how they would scope the work, what assumptions they need to verify, which access they require and what could prevent completion. The answer should make sense to the people who will own the result.
Request appropriate evidence of relevant competence, such as platform credentials, a sample deliverable without confidential material or a reference that can be shared. A strong technical specialist may also be suitable without CISSP.
Put expectations in the agreement
Name the person who will do the work, the deliverables, review points and handover requirements. Clarify which changes require your approval and what access ends when the assignment ends.
For ISO 27001 work, the Lead Implementer guide explains another relevant credential. Use qualifications to support a decision about competence, while judging the proposal on what your business actually needs.